
November 6 CISO Defense Blueprint: Hardening Xen Dom0, Alpine musl OpenSSH, LXD mTLS, cPGuard/CWP Hosting Panels, Cold-Chain OT Controllers & Enterprise AD CS

📌
Security Roundup Series: Week of November 6, 2026 • 9 min read deep dive
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-119977, CVE-2026-107441, XSA-523, CVE-2026-112816, CVE-2026-123158 & CVE-2026-58868 (Hypervisor Grant Copy, mTLS Chain Validation, musl crypt(a.plerdy.com) Error Handling, TOCTOU & OT Access Control)
Severity: PRODUCTION HARDENING & DETECTION ENGINEERING PLAYBOOK (CVSS 10.0 (LXD / GitLab) to 9.8 (Zyxel / Android / Linux TCP) & 8.1 (WordPress / OpenSSH))
Threat Actor: UTA0576, Kapibala, APT29, TraderTraitor, Kali365/VoidProxy & Cold-Chain OT Saboteurs
Status: Mandatory Remediation Playbook for the Week of November 6, 2026
Affected Systems: Xen Dom0, Canonical LXD, Alpine Linux OpenSSH, WordPress, Ivanti ICS, Zyxel GS1900, cPGuard/CWP, Android & Cold-Chain OT
Fixed In: Full Production Commands, WAF Rules, AD CS PowerShell Scripts & OT Firewall Policies Below
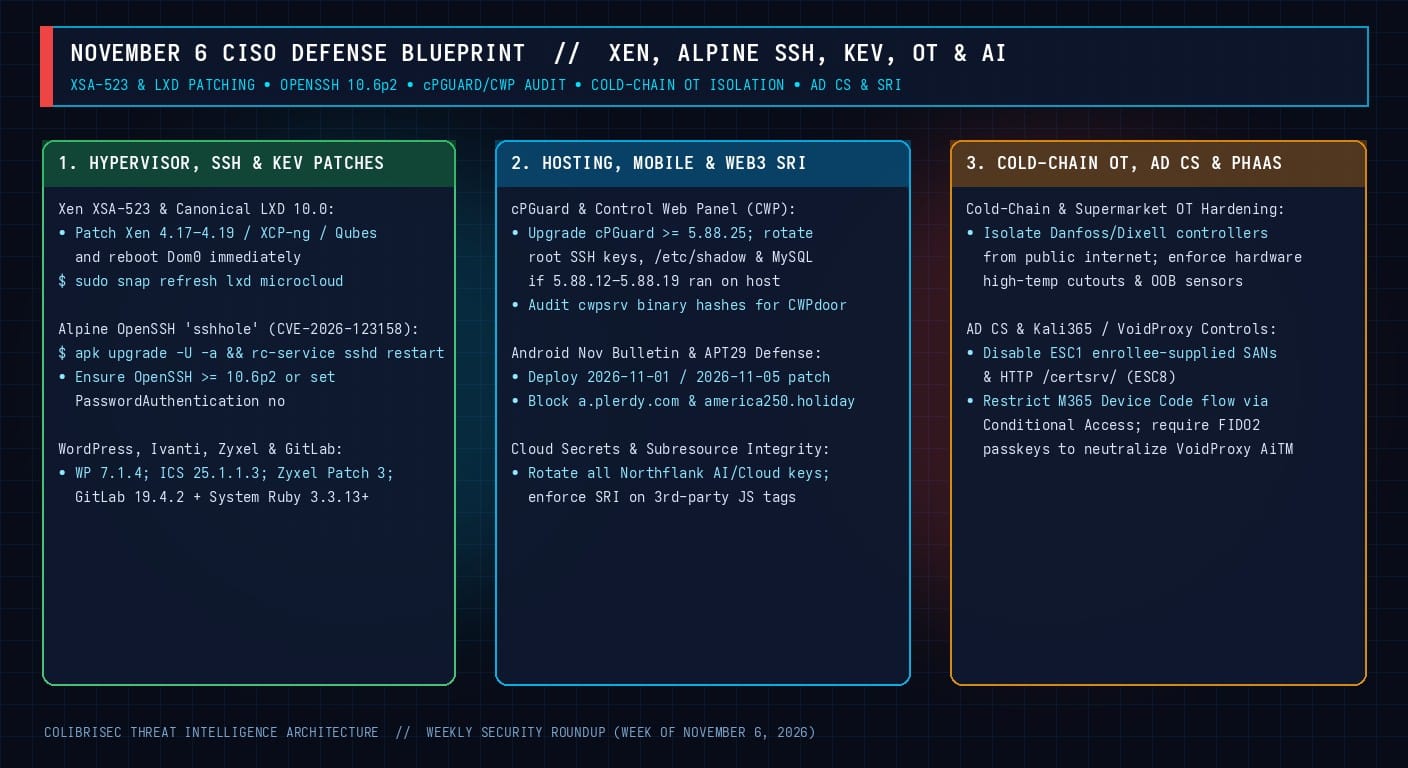
To help security engineering, cloud infrastructure, and SOC teams operationalize defenses against all ten threat tracks covered in the Week of November 6, 2026 Security Roundup, this blueprint consolidates copy-pasteable verification commands, emergency configuration mitigations, WAF rules, Active Directory Certificate Services (AD CS) hardening scripts, and operational technology (OT) isolation controls into a single reference guide.
Layer 1: Hypervisor (Xen XSA-523), Container Cluster (LXD 10.0) & Alpine OpenSSH ("sshhole")
# 1A. Alpine Linux & musl Container Fleet — Patch OpenSSH "sshhole" (CVE-2026-123158):
apk update && apk upgrade -U -a
rc-service sshd restart || kill -HUP $(cat /var/run/sshd.pid)
# Enforce key-only auth and disable password auth as defense-in-depth:
sed -i -E 's/^#?PasswordAuthentication.*/PasswordAuthentication no/' /etc/ssh/sshd_config
sed -i -E 's/^#?KbdInteractiveAuthentication.*/KbdInteractiveAuthentication no/' /etc/ssh/sshd_config
rc-service sshd restart

# 1B. Canonical LXD & MicroCloud — Patch CVSS 10.0 mTLS Bypass (CVE-2026-112816):
sudo snap refresh lxd microcloud
# Verify patched versions (LXD >= 6.10.1 / 5.21.9 / 5.0.11 / 4.0.15; MicroCloud >= 3.4.1 / 2.1.5):
snap list lxd microcloud

# 1C. Xen Hypervisor — Patch Grant Copy Dom0 Escape (XSA-523 / CVE-2026-102703 & 102704):
# Apply vendor Dom0 hypervisor packages (Xen 4.17–4.19, XCP-ng, Debian, Qubes QSB-121) and reboot:
xl info | grep -E "xen_version|xen_changeset"

# 1D. GitLab CE/EE (CVE-2026-97229 CVSS 10.0) — Audit Both GitLab AND System Ruby:
gitlab-rake gitlab:env:info | grep -E "GitLab|Ruby"
ruby -v  # Must be >= 3.3.13, 3.4.12, or 4.0.9 on Alpine/distro/source installs!
Layer 2: CISA KEV Perimeter & Hosting Supply-Chain Forensics (WordPress, Ivanti, Zyxel, cPGuard & CWP)
# 2A. Nginx WAF Block for WordPress Core TOCTOU Upgrade Race (CVE-2026-119977 - BOD Due Nov 6):
location ~* ^/wp-content/upgrade/ {
    deny all;
    return 403;
}
# 2B. cPGuard CDN Compromise Triage (Versions 5.88.12 through 5.88.19):
# If any cPanel/DirectAdmin server installed 5.88.12–5.88.19 during the 70-minute window:
# 1. Update cPGuard to >= 5.88.25
# 2. Rotate root password and all /etc/shadow hashes
# 3. Rotate MySQL root password in /root/.my.cnf
# 4. Audit /root/.ssh/authorized_keys, /etc/cron*, and /etc/systemd/system/ for backdoors:
find /etc/cron* /var/spool/cron /etc/systemd/system -mtime -7 -ls
# 2C. Control Web Panel (CWP) "CWPdoor" Binary Integrity Check:
sha256sum /usr/local/cwpsrv/bin/cwpsrv
strings /usr/local/cwpsrv/bin/cwpsrv | grep -iE "popen|system|/bin/sh|cwpdoor"Layer 3: Active Directory Certificate Services (ESC1/ESC8), AI PhaaS & Cold-Chain OT Isolation
# 3A. PowerShell Audit for AD CS Templates Vulnerable to ESC1 (Teams + Quick Assist Takeover):
Get-ADObject -SearchBase "CN=Certificate Templates,CN=Public Key Services,CN=Services,$((Get-ADRootDSE).configurationNamingContext)"   -Filter { objectClass -eq "pKICertificateTemplate" }   -Properties cn, msPKI-Certificate-Name-Flag, pKIExtendedKeyUsage |
  Where-Object { ($_.('msPKI-Certificate-Name-Flag') -band 1) -ne 0 } |
  Select-Object cn, msPKI-Certificate-Name-Flag, pKIExtendedKeyUsage

# Disable IIS HTTP Web Enrollment (/certsrv/) on AD CS servers to neutralize ESC8 NTLM relay:
Stop-Service -Name W3SVC -Force
Set-Service -Name W3SVC -StartupType Disabled- Neutralizing Kali365, VoidProxy & APT29 Watering Holes: Create a Microsoft Entra Conditional Access policy blocking the Device Code authentication flow across all non-admin users (stopping Kali365); enforce phishing-resistant FIDO2 / WebAuthn passkeys to defeat VoidProxy AiTM session proxying; and block
a.plerdy[.]com/public/js/click/main.jsandamerica250[.]holidayat corporate DNS/SWG resolvers. - Cold-Chain & Supermarket OT Isolation: Audit all retail and warehouse networks for exposed Danfoss, Dixell, Modbus (TCP 502), and BACnet (UDP 47808) interfaces; place HVAC/R controllers on isolated OT VLANs behind zero-trust jump hosts; and install independent out-of-band thermal sensors and physical high-temperature heater cutouts.
🧭
More Deep Dives from this Roundup:
CISA KEV Directives & Perimeter Zero-Days: WordPress Core Upgrade Race RCE (CVE-2026-119977), Ivanti Connect Secure 3-Bug Root Chain & Zyxel GS1900 Switch Patch-Bypass (CVE-2026-107441)
Hypervisor & Cloud Cluster Breakouts: Xen Grant Copy Dom0 Escape Found by Claude (XSA-523 / CVE-2026-102703 & 102704) & Canonical LXD CVSS 10.0 mTLS Bypass (CVE-2026-112816)
Linux Authentication & Regex Traps: Dissecting OpenSSH musl libc "sshhole" Auth Bypass (CVE-2026-123158) on Alpine Linux & The GitLab CVSS 10.0 System Ruby Onigmo Trap (CVE-2026-97229)
Android November 2026 Security Bulletin: Zero-Click FrameDecoder.cpp RCE (CVE-2026-58868), libpng UAF (CVE-2026-58936) & The 8-Byte WAP Push "SMS of Death" (CVE-2026-58882)
Hosting & Gaming Supply-Chain Backdoors: cPGuard CDN Update Poisoning Across 3,000 Linux Servers, Control Web Panel "CWPdoor" Implant & Goddess of Victory: NIKKE PC Launcher Compromise
Frontier AI in Cybersecurity: OpenAI "GPT-6 Cyber" Synthesizes 948 Linux Kernel Root Exploits, Chainalysis "Offensive Agentic" Breach, Unit 42 SysGoRAT & Check Point "Haiou" Codex Adware
Cloud Secrets, Web3 & Hardware Supply Chain: Northflank PaaS "LLMjacking" Breach, Polymarket $3.9M DebugBear DNS Hijack, Trezor Safe 5 Cellular PCB Implant & FBI Binance TraderTraitor IOCs
European Cold-Chain OT Sabotage: Inside the 50°C Supermarket Refrigeration Cyberattacks Across 7 Countries & The Joint FBI/CISA Industrial Cold-Chain Advisory
APT29 "Poisoned Source" Mobile Watering Holes, AI-Lure PhaaS (Kali365 & VoidProxy), Teams-to-AD CS Takeover & Global Breaches (Queens Library, Myriad Genetics, mSecure & Japan $63M Package)
← Return to Weekly Overview: Full Roundup

