News

ColibriSec Weekly Security Roundup October 9 2026

News

Security Roundup: Atlassian Zero-Day, Citrix NetScaler Flaw, AhsayCBS RCE Chain, FBI MicroScan Takedown (Week of October 9, 2026)

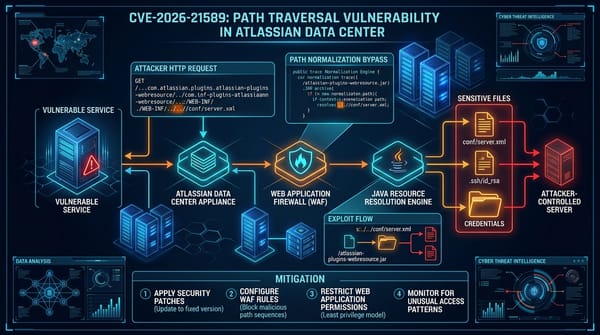
Executive Summary: The week of October 2 to October 9, 2026, delivered a rapid succession of perimeter breaches, critical zero-day weaponization, and historic multinational law enforcement actions. Atlassian self-hosted Data Center installations faced mass automated exploitation following proof-of-concept release for CVE-2026-21589 (CVSS 9.3), a path traversal vulnerability in web
By James Luther
AhsayCBS Dual Zero-Day Exploit Chain Architecture

News

AhsayCBS Dual Zero-Day Exploit Chain: CVE-2026-105133 & CVE-2026-105134 Chained for Unauthenticated RCE

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-105133 & CVE-2026-105134 (CWE-287 (Improper Authentication) / CWE-78 (OS Command Injection)) Severity: CRITICAL (CVSS 9.3) Status: Actively Exploited in the Wild (First Observed Oct 7, 2026 by Huntress) Affected Systems: AhsayCBS Enterprise Backup

By James Luther
Operation MicroScan and FishHub Global Takedown

News

Operation MicroScan & FishHub: FBI Takedown of Integrity Tech Infrastructure and Emergency CISA KEV Order

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️OPERATION MICROSCAN & FISHHUB: INFRASTRUCTURE TAKEDOWN Multinational law enforcement action led by FBI, DOJ, CISA, NSA, and Five Eyes + Spain + Japan targeting Beijing-based Integrity Technology Group. 7 core command and operational domains seized under federal court warrants

By James Luther
ASOS Push Notification Security Breach Concept

News

ASOS Global Push Notification Breach: Xuanye Group Hijacks Customer Engagement Pipeline

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: ASOS.com (Global Online Fashion & Retail) Threat Actor / Attribution: Xuanye Group (Cyber Extortion Collective) Impact / Records Compromised: Customer names, email addresses, phone numbers, delivery addresses, search histories Initial Attack Vector: Social engineering

By James Luther
Photon Health Healthcare Data Breach Concept

News

Photon Health Data Breach: Zero-Day SQL Injection in Self-Hosted Metabase Exposes Patient Prescriptions

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Photon Health, Inc. (Digital E-Prescription SaaS Infrastructure) Threat Actor / Attribution: Unidentified Threat Actor (Financial / Data Extortion) Impact / Records Compromised: Patient names, street addresses, phone numbers, dates of birth, sensitive prescription medications Initial Attack

By James Luther
Apache HTTP Server Security Vulnerabilities Architecture

News

Apache HTTP Server Security Advisory: Critical RCE and Request Splitting Vulnerabilities in Version 2.4.68

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-42356 & CVE-2026-42528 (CWE-444 (Inconsistent Interpretation of HTTP Requests) / CWE-120 (Buffer Overflow)) Severity: HIGH / CRITICAL (CVSS 8.8 / 7.5) Status: Official Vendor Security Release Issued October 9, 2026 Affected Systems: Apache HTTP

By James Luther
Q3 2026 Ransomware Threat Statistics and Extortion Trends

News

Q3 2026 Threat Landscape Analysis: Ransomware Surge (+61% YoY) and the Strategic Pivot to Pure Exfiltration

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️Q3 2026 RANSOMWARE THREAT INTELLIGENCE SYNTHESIS Quarterly cybercrime analytics released October 9, 2026, documenting a massive surge in extortion activity and structural operational pivots. Ransomware incident volume rose 27% compared to Q2 2026 and surged 61% year-over-year

By James Luther
Technical University of Denmark DTU DTUBasen Identity Management Breach

News

Technical University of Denmark (DTU) Breach: 200,000 Identities Exposed via DTUBasen IAM

📌Security Roundup Series: Weekend of October 5, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Technical University of Denmark (Danmarks Tekniske Universitet - DTU) Threat Actor / Attribution: Unauthenticated Cyber Threat Actor / Credential Abuse Impact / Records Compromised: Up to 200,000 Current and Former Students, Faculty, and Researchers Initial

By ColibriSec
ColibriSec Weekend Security Roundup October 5 2026

News

Security Roundup: Citrix NetScaler SAML Zero-Day, Denmark 8.8M Registry Breach, Rejetto AI RCE, Asian Financial Infiltrations (Weekend of October 5, 2026)

Executive Summary: The weekend of October 3–5, 2026, delivered an unprecedented surge of critical perimeter exploits, monumental government and enterprise data leaks, and AI-driven intrusion vectors. Headlining the emergency alerts, Citrix confirmed active targeted exploitation of CVE-2026-88779—a high-severity memory overflow zero-day in NetScaler ADC and Gateway configured as

By ColibriSec