Ruby2Shell (CVE-2026-132825 / GHSA-34m4-m9fh-gqp5): Analyzing Ruby’s Single-Byte Encoding Case-Conversion Heap Overflow and the November 2026 Regexp Advisory Suite
A code-level teardown of Ruby2Shell (CVE-2026-132825 / GHSA-34m4-m9fh-gqp5) and the six companion November 18, 2026 Ruby advisories: how a 1-to-2 byte character expansion (0xDF 'ß' -> 'SS') in legacy ISO-8859-x and Windows-125x encodings causes an off-by-one heap write in Ruby 2.4 through 4.0.9.

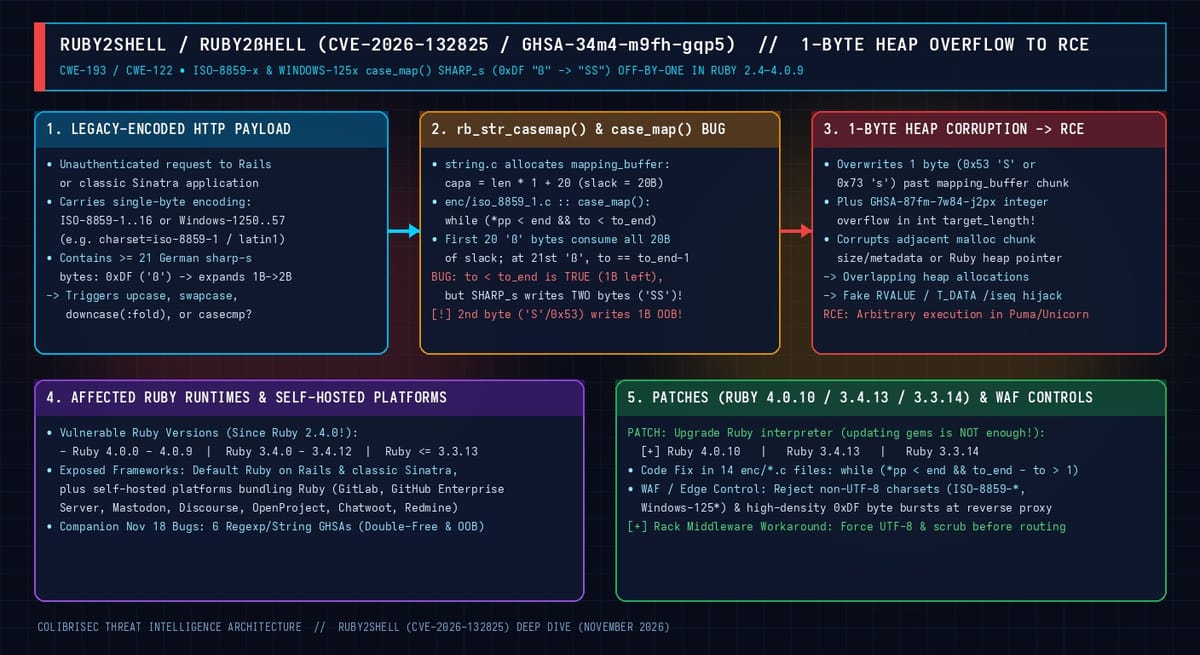
CVE-2026-132825 / GHSA-34m4-m9fh-gqp5 ("Ruby2Shell" / "ruby2ßhell") + 6 Companion String & Regexp GHSAs (CWE-193 Off-by-One Error, CWE-122 Heap-Based Buffer Overflow & CWE-190 Integer Overflow)
Severity: CRITICAL (1-BYTE HEAP BUFFER OVERFLOW IN CORE STRING CASE CONVERSION) (CVSS Critical / High (Core Ruby String & Onigmo Regexp Memory Corruption))
Threat Actor: Stephan Lipp (Ada Logics) & Anthropic; baba__yaga; aphantom; Hiroya Fujinami & Hiroshi SHIBATA (Nov 18, 2026)
Status: Emergency Patched Ruby Releases Shipped Nov 18, 2026; Runtime Upgrade Required
Affected Systems: Ruby <= 3.3.13 (since 2.4.0), Ruby 3.4.0–3.4.12, and Ruby 4.0.0–4.0.9 (Rails, Sinatra, GitLab, GitHub Enterprise, Mastodon, Discourse)
Fixed In: Ruby 4.0.10, Ruby 3.4.13, and Ruby 3.3.14
On November 18, 2026, the Ruby core team released emergency security updates (Ruby 4.0.10, 3.4.13, and 3.3.14) to remediate seven memory-corruption vulnerabilities spanning Ruby’s String case-mapping subsystem and its Onigmo regular expression engine. The headline flaw—tracked as CVE-2026-132825 (GHSA-34m4-m9fh-gqp5) and dubbed "Ruby2Shell" (or "ruby2ßhell")—is a classic off-by-one heap buffer overflow (CWE-193) that has lived inside Ruby’s C encoding handlers (enc/iso_8859_*.c and enc/windows_125*.c) since Ruby 2.4.0 introduced non-ASCII case mapping in 2016. When methods such as String#upcase, String#swapcase, String#downcase(:fold), or String#casecmp? process a string encoded in a single-byte legacy charset (ISO-8859-1 through ISO-8859-16 or Windows-1250/1252/1254/1257), the German lowercase sharp-s character (ß, byte 0xDF) expands from one input byte into two output bytes ("SS" or "ss"). Because the inner C loop checked to < to_end (verifying room for only one byte) before writing two bytes, an input containing 21 or more 0xDF bytes exhausts Ruby’s 20-byte buffer slack cushion (CASE_MAPPING_ADDITIONAL_LENGTH) and writes one byte past the end of the xmalloc-allocated heap buffer.
1. Matrix of the Seven November 18, 2026 Ruby Security Advisories
| Advisory ID | Component & Files | Vulnerability Class | Root Cause Summary | Credits |
|---|---|---|---|---|
CVE-2026-132825GHSA-34m4-m9fh-gqp5("Ruby2Shell") |
enc/iso_8859_*.c (10)& enc/windows_125*.c (4) |
1-Byte Heap Buffer Overflow (CWE-193) |
case_map() checks to < to_end (1 byte left) before expanding SHARP_s (0xDF 'ß') into 2 bytes ("SS" / "ss"). |
Stephan Lipp (Ada Logics) & Anthropic |
| GHSA-87fm-7w84-j2px | string.c( rb_str_casemap) |
Integer Overflow -> Heap Overflow (CWE-190) |
32-bit int target_length accumulator in rb_str_casemap() overflows when summing multi-buffer expansions. |
baba__yaga |
| GHSA-7x2q-68qv-6p8x | regparse.c |
Heap Double Free (CWE-415) |
Error return in parse_char_class() (TK_CHAR_TYPE) skips error cleanup label, causing a double free during Regexp compilation. |
Stephan Lipp (Ada Logics) & Anthropic |
| GHSA-wpqw-5qxg-m68r | regexec.c |
Out-of-Bounds Read (CWE-125) |
Case-insensitive regular expression matching reads past buffer bounds on malformed multibyte inputs. | Stephan Lipp (Ada Logics) & Anthropic |
| GHSA-3p8q-wmhx-vm2w | regcomp.c |
Integer Overflow -> Heap Overflow (CWE-190) |
Integer overflow when computing compiled bytecode size for crafted regular expression patterns. | aphantom |
| GHSA-7whj-cfh7-xgm4 | re.c (Regexp#to_s) |
Heap Buffer Overflow (CWE-122) |
Buffer sizing error when serializing a compiled Regexp back to a String via Regexp#to_s. |
Stephan Lipp (Ada Logics) & Anthropic |
| GHSA-pvgc-g7gj-pv6h | regexec.c |
Out-of-Bounds Read (CWE-125) |
Out-of-bounds read during case-insensitive backreference matching. | Hiroya Fujinami & Hiroshi SHIBATA |
2. Code-Level Root Cause of Ruby2Shell (CVE-2026-132825)
When Ruby performs a case conversion on a string containing non-ASCII bytes (>= 0x80), execution enters rb_str_casemap() in string.c. On the first pass (buffer_count == 1), rb_str_casemap() allocates a temporary mapping_buffer on the heap sized to the input string length plus a 20-byte slack cushion (CASE_MAPPING_ADDITIONAL_LENGTH = 20):
/* Ruby v3.4.12: string.c :: rb_str_casemap() */
#define CASE_MAPPING_ADDITIONAL_LENGTH 20

while (source_current < source_end) {
    size_t capa = (size_t)(source_end - source_current) * ++buffer_count
                  + CASE_MAPPING_ADDITIONAL_LENGTH;
    current_buffer = xmalloc(offsetof(mapping_buffer, space) + capa);
    /* ... */
    buffer_length_or_invalid = enc->case_map(
        flags, &source_current, source_end,
        current_buffer->space,
        current_buffer->space + current_buffer->capa, enc);
}
Now examine case_map() in enc/iso_8859_1.c (and duplicated across iso_8859_2/3/4/9/10/13/14/15/16.c and windows_1250/1252/1254/1257.c):
/* Ruby v3.4.12: enc/iso_8859_1.c :: case_map() */
static int
case_map(OnigCaseFoldType* flagP, const OnigUChar** pp,
         const OnigUChar* end, OnigUChar* to, OnigUChar* to_end,
         const struct OnigEncodingTypeST* enc)
{
  OnigCodePoint code;
  OnigUChar *to_start = to;
  OnigCaseFoldType flags = *flagP;

  /* BUG: Verifies only 1 byte of remaining space (to < to_end)! */
  while (*pp < end && to < to_end) {
    code = *(*pp)++;
    if (code == SHARP_s) {           /* 0xDF ('ß') */
      if (flags & ONIGENC_CASE_UPCASE) {
        flags |= ONIGENC_CASE_MODIFIED;
        *to++ = 'S';                 /* <--- Byte 1 written */
        code = (flags & ONIGENC_CASE_TITLECASE) ? 's' : 'S';
      }
      else if (flags & ONIGENC_CASE_FOLD) {
        flags |= ONIGENC_CASE_MODIFIED;
        *to++ = 's';                 /* <--- Byte 1 written */
        code = 's';
      }
    }
    /* ... */
    *to++ = code;                    /* <--- Byte 2 written! */
  }
  *flagP = flags;
  return (int)(to - to_start);
}0xDF ('ß') Byte Overflows the Heap
Each 0xDF byte in the input writes two bytes to to, consuming one byte of the 20-byte CASE_MAPPING_ADDITIONAL_LENGTH slack cushion. After 20 0xDF bytes, the slack is zero. When the loop reaches a 21st 0xDF byte at the end of the buffer (where to == to_end - 1), the loop condition to < to_end evaluates to true because 1 byte remains—but the SHARP_s branch writes two bytes, placing 0x53 ('S') or 0x73 ('s') at *to_end (1 byte out of bounds)!The Upstream Patch in Ruby 4.0.10, 3.4.13, and 3.3.14
--- a/enc/iso_8859_1.c
+++ b/enc/iso_8859_1.c
@@ -264,7 +264,7 @@ case_map(OnigCaseFoldType* flagP, const OnigUChar** pp,
   OnigUChar *to_start = to;
   OnigCaseFoldType flags = *flagP;

-  while (*pp < end && to < to_end) {
+  while (*pp < end && to_end - to > 1) {
     code = *(*pp)++;
     if (code == SHARP_s) {
       if (flags & ONIGENC_CASE_UPCASE) {
3. Why Default Ruby on Rails, Classic Sinatra & Self-Hosted Apps Are Exposed
- HTTP Charset Negotiation (
charset=ISO-8859-1/Windows-1252): When an incoming HTTP request or multipart form field declares a legacy single-byte charset inContent-Type, parameter parsers tag the resulting RubyStringwithEncoding::ISO_8859_1orEncoding::Windows_1252. - Silent Case-Folding via
String#casecmp?: Even if an application never calls.upcaseexplicitly, Ruby’s case-insensitive comparison methodString#casecmp?(used across Rack, Rails, and Sinatra for header, token, MIME, and route comparisons) invokesONIGENC_CASE_FOLDinsidecase_map()whenever a single-byte encoded string contains bytes>= 0x80. - Bundled Ruby Runtimes in Self-Hosted Platforms: Omnibus and container deployments of GitLab, GitHub Enterprise Server, Mastodon, Discourse, OpenProject, and Chatwoot bundle their own Ruby interpreter and must be updated to vendor builds shipping Ruby
3.3.14+,3.4.13+, or4.0.10+.
4. Exploit Telemetry & Production Detection Rules (ModSecurity, Suricata, Sigma & SIEM)
1. ModSecurity / Coraza WAF Rules (IDs 950035–950036)
# SPDX-License-Identifier: GPL-2.0-only
# Copyright (C) 2026 James Luther <[email protected]>
# ColibriSec Detection Rules for Ruby2Shell (CVE-2026-132825 / GHSA-34m4-m9fh-gqp5)

# --- 950035: Legacy single-byte charset declaration in Content-Type or body ---
SecRule REQUEST_HEADERS:Content-Type|REQUEST_BODY \
  "@rx charset[[:space:]]*=[[:space:]]*[\"']?(?:iso-?8859-(?:1[03-6]?|[1-49])|windows-?125[0247]|cp125[0247]|latin[1-9])" \
  "id:950035,phase:2,deny,status:403,log,auditlog,t:none,t:lowercase,\
msg:'Ruby2Shell (CVE-2026-132825): Legacy single-byte charset negotiation (ISO-8859/Windows-125x)',\
tag:'attack-rce',tag:'cve-2026-132825',tag:'ruby2shell'"

# --- 950036: >=21 SHARP_s (0xDF / %DF) bytes in request parameters or body ----
SecRule REQUEST_URI|REQUEST_BODY|ARGS|REQUEST_HEADERS \
  "@rx (?:\\xdf|%[dD][fF]){21,}" \
  "id:950036,phase:2,deny,status:403,log,auditlog,t:none,\
msg:'Ruby2Shell (CVE-2026-132825): High-density 0xDF (SHARP_s) heap-overflow sequence (>=21 bytes)',\
tag:'attack-rce',tag:'cve-2026-132825',tag:'ruby2shell'"
2. Suricata IDS Signatures (sid:2026132825–2026132826)
alert http $EXTERNAL_NET any -> $HOME_NET any (msg:"COLIBRISEC EXPLOIT Ruby2Shell CVE-2026-132825 High-Density 0xDF Sharp-S Heap Overflow Payload"; flow:established,to_server; pcre:"/(?:\xdf|%[dD][fF]){21,}/"; reference:cve,2026-132825; classtype:attempted-admin; sid:2026132825; rev:1;)

alert http $EXTERNAL_NET any -> $HOME_NET any (msg:"COLIBRISEC EXPLOIT Ruby2Shell CVE-2026-132825 Legacy ISO-8859/Windows-125x Charset with 0xDF Bytes"; flow:established,to_server; http.content_type; pcre:"/charset\s*=\s*[\x22\x27]?(?:iso-?8859-|windows-?125|cp125|latin)/i"; http.request_body; pcre:"/(?:\xdf|%[dD][fF]){10,}/"; reference:cve,2026-132825; classtype:attempted-admin; sid:2026132826; rev:1;)
3. Sigma Rules for Ruby VM Crash Telemetry & Worker Process Creation
title: Ruby VM Segmentation Fault in rb_str_casemap or Onigmo Regexp (CVE-2026-132825 / Ruby2Shell)
id: 3c71b8e4-5f20-59a1-8c34-132825009201
status: experimental
author: James Luther (ColibriSec)
date: 2026/11/19
logsource:
  product: linux
  service: syslog
detection:
  selection_ruby_bug:
    - '[BUG] Segmentation fault'
    - 'corrupted size vs. prev_size'
    - 'malloc(): corrupted top size'
  selection_symbol:
    - 'rb_str_casemap'
    - 'mapping_buffer_free'
    - 'rb_str_upcase'
    - 'rb_str_casecmp'
    - 'onig_'
  condition: selection_ruby_bug and selection_symbol
level: critical
tags:
  - attack.t1190
  - cve.2026.132825
5. Remediation & Rack Middleware Hardening Playbook
bundle update Does Not Patch CVE-2026-132825
Because CVE-2026-132825 and its six companion advisories reside inside the C implementation of the Ruby interpreter itself (libruby.so / /usr/bin/ruby), updating Ruby gems will not fix the vulnerability. You must upgrade the Ruby runtime binary to 4.0.10, 3.4.13, or 3.3.14 and restart all Puma, Unicorn, Pitchfork, Passenger, and Sidekiq processes.# 1. Verify active Ruby runtime version:
ruby -v
# Upgrade to Ruby 4.0.10, 3.4.13, or 3.3.14:
mise install [email protected] && mise use -g [email protected]
# 2. Restart all Ruby application servers and background workers:
sudo systemctl restart puma sidekiq
# 3. Hunt application/container logs for Ruby VM rb_str_casemap segmentation faults:
grep -rnE "\[BUG\] Segmentation fault|rb_str_casemap|mapping_buffer_free" /var/log/ 2>/dev/null