
Hosting & Gaming Supply-Chain Backdoors: cPGuard CDN Update Poisoning Across 3,000 Linux Servers, Control Web Panel "CWPdoor" Implant & Goddess of Victory: NIKKE PC Launcher Compromise

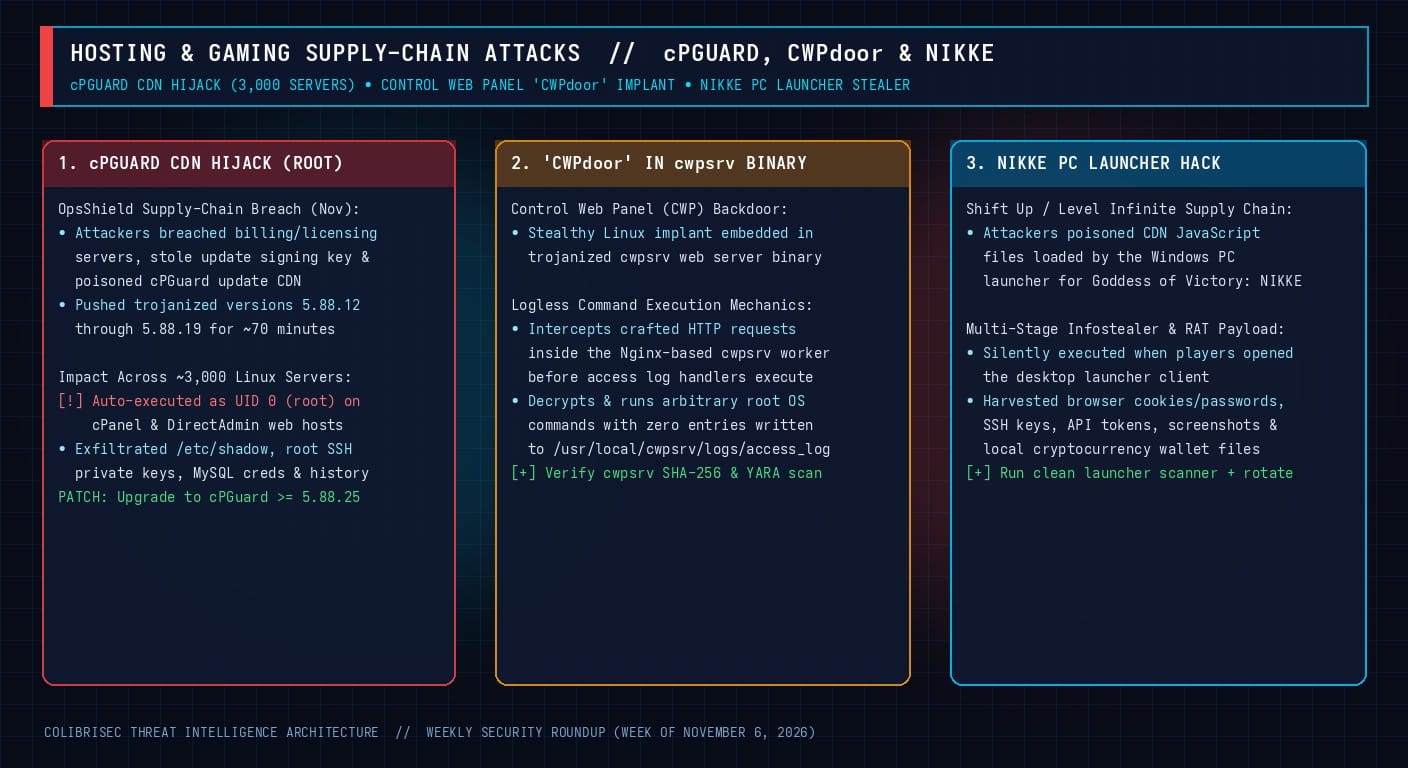
Software update channels and web-hosting control panels represent high-leverage targets: compromising a single vendor CDN allows threat actors to execute code as root across thousands of downstream servers simultaneously. During the first week of November 2026, three major supply-chain and hosting-panel compromises came to light. First, OpsShield—the vendor behind the widely deployed cPGuard security suite for cPanel and DirectAdmin Linux servers—confirmed that attackers breached its licensing and billing infrastructure, stole an update key, and poisoned its CDN to push malicious updates (versions 5.88.12 through 5.88.19) that automatically executed with root privileges across nearly 3,000 web servers during a 70-minute window. Second, malware researchers uncovered "CWPdoor", a stealthy backdoor compiled directly into trojanized cwpsrv binaries on Control Web Panel (CWP) Linux servers that executes attacker commands without leaving access log trails. Third, publisher Level Infinite and developer Shift Up confirmed a CDN supply-chain attack against the Windows PC launcher for the hit RPG shooter Goddess of Victory: NIKKE that silently delivered a multi-stage credential and crypto-wallet infostealer.
1. The cPGuard CDN Supply-Chain Compromise (Versions 5.88.12–5.88.19)
Ironically, cPGuard is installed by Linux web hosting providers specifically to provide Web Application Firewall (WAF) protection, real-time malware scanning, and rootkit detection on multi-tenant cPanel and DirectAdmin servers. Because cPGuard’s background daemon runs as UID 0 (root) and polls OpsShield’s update CDN automatically to pull signature and engine updates, compromising the update pipeline turned the security agent into an automated root deployment vehicle.
What the Malicious Update Script Stole in 70 Minutes
- Credential & Key Harvesting: Upon automatic installation of versions
5.88.12through5.88.19, the injected shell script immediately harvested/etc/shadow(all system and hosting account password hashes),/root/.ssh/private keys andauthorized_keys,/root/.my.cnf(MySQL/MariaDB root credentials), and root shell history (/root/.bash_history). - Selective Root Backdoor Persistence: On a targeted subset of the ~3,000 affected servers, the script planted an unauthorized SSH key, registered a hidden cron/systemd persistence task, and deployed an obfuscated root shell accessible over HTTP.
While OpsShield revoked the compromised signing credentials and released clean version 5.88.25, simply upgrading the plugin does not undo the theft of /etc/shadow, root SSH keys, or MySQL root passwords on any server that pulled a build between 5.88.12 and 5.88.19.
2. "CWPdoor": The Logless Backdoor Inside Control Web Panel’s cwpsrv
In a separate Linux hosting disclosure, researchers dissected CWPdoor, a binary-level implant targeting Control Web Panel (CWP) (formerly CentOS Web Panel). CWP uses a dedicated Nginx-derived web server binary—/usr/local/cwpsrv/bin/cwpsrv—to serve its administrative and user management interfaces on ports 2030/2031 and 2082/2083.
Instead of dropping a detectable PHP web shell into /usr/local/cwpsrv/htdocs/, CWPdoor replaces or patches the compiled cwpsrv ELF binary itself. By hooking the HTTP request-handling phase in memory prior to Nginx’s standard log phase handler, CWPdoor inspects incoming HTTP headers/cookies for a cryptographic trigger, executes the embedded OS command as root, returns the output in the HTTP response, and terminates request processing without writing a single line to /usr/local/cwpsrv/logs/access_log.
3. Goddess of Victory: NIKKE Windows PC Launcher Supply-Chain Attack
Rounding out the supply-chain wave, attackers compromised CDN assets serving JavaScript files to the embedded Chromium/CEF login and update window inside the Windows PC launcher for Goddess of Victory: NIKKE. When players launched the game on Windows, the poisoned JavaScript silently staged a multi-stage remote access agent and infostealer that:
- Extracted saved passwords, session cookies, and OAuth tokens from Chrome, Edge, Brave, and Firefox browser profiles;
- Scanned the filesystem for developer secrets (
.ssh/keys, AWS/cloud credentials,.envfiles) and desktop cryptocurrency wallet vaults; and - Captured desktop screenshots and system metadata before Shift Up and Level Infinite purged the CDN script and pushed a launcher verification and cleanup update.
Forensic Hunting & Remediation Commands
# 1. cPGuard Supply-Chain Audit (Linux cPanel / DirectAdmin Servers):
# Check current version and update logs for versions 5.88.12 through 5.88.19:
grep -E "5.88.(1[2-9])" /var/log/cpguard* /var/cpanel/logs/* 2>/dev/null

# Force upgrade to clean cPGuard >= 5.88.25:
# Then IMMEDIATELY rotate root password, /root/.my.cnf MySQL root password,
# and inspect /root/.ssh/authorized_keys & /etc/crontab for unauthorized entries!

# 2. Hunt for "CWPdoor" on Control Web Panel (CWP) Linux Hosts:
sha256sum /usr/local/cwpsrv/bin/cwpsrv
rpm -Vf /usr/local/cwpsrv/bin/cwpsrv 2>/dev/null
# Inspect running cwpsrv worker processes for deleted/replaced ELF binaries or unexpected child shells:
ls -l /proc/$(pgrep -f cwpsrv | head -n1)/exe
ps -ef --forest | grep -A5 cwpsrv
