
Enterprise ERP & Firewall Megapatches: SAP 4x CVSS 10.0 ("ICM2SHELL" & "PROXYGATE"), Fortinet FGFM/OSPF & Adobe Connect/AEM

📌
Security Roundup Series: Weekend of November 16, 2026 • 8 min read deep dive
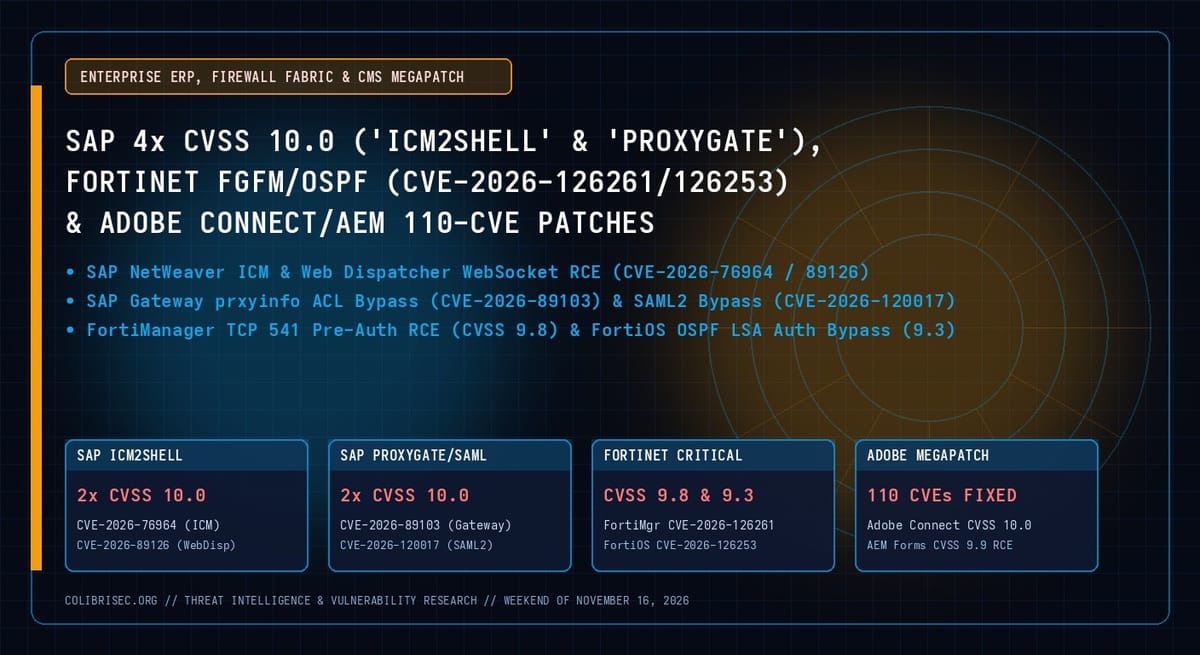
Enterprise ERP administrators, network firewall engineers, and digital experience teams faced an unprecedented cluster of maximum-severity advisories this week: SAP patched four CVSS 10.0 vulnerabilities led by Onapsis’s ICM2SHELL and PROXYGATE disclosures; Fortinet published critical advisories for FortiManager’s FGFM protocol (CVE-2026-126261, CVSS 9.8) and FortiOS/FortiSASE OSPF routing (CVE-2026-126253, CVSS 9.3); and Adobe remediated 110 CVEs across nine products including CVSS 10.0 and 9.9 flaws in Adobe Connect and Adobe Experience Manager (AEM).
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-76964, CVE-2026-89126, CVE-2026-89103, CVE-2026-120017, CVE-2026-126261 & CVE-2026-126253 (CWE-119 / CWE-787 (Memory Corruption), CWE-284 / CWE-863 (Broken Access Control) & CWE-305 (OSPF Auth Bypass))
Severity: CRITICAL (4x CVSS 10.0 SAP RCE/Auth Bypass, CVSS 9.8 FortiManager & CVSS 10.0 Adobe Connect) (CVSS 10.0 (SAP ICM2SHELL, PROXYGATE, SAML2 & Adobe Connect) / 9.8 (FortiManager FGFM) / 9.3 (FortiOS OSPF))
Status: Critical Vendor Patches Released — Immediate Deployment Required
Affected Systems: SAP NetWeaver AS ABAP ICM, SAP Web Dispatcher, SAP Gateway & SAML2; FortiManager 7.2–8.0; FortiOS 7.0–8.0; Adobe Connect & AEM
Fixed In: SAP Notes 3778530, 3778556, 3798345 (gw/acl_mode_proxy=1) & 3849308; FortiManager/FortiOS Updates; APSB26-191 & APSB26-189
1. SAP’s Four CVSS 10.0 Vulnerabilities: ICM2SHELL, PROXYGATE & SAML2 Bypass
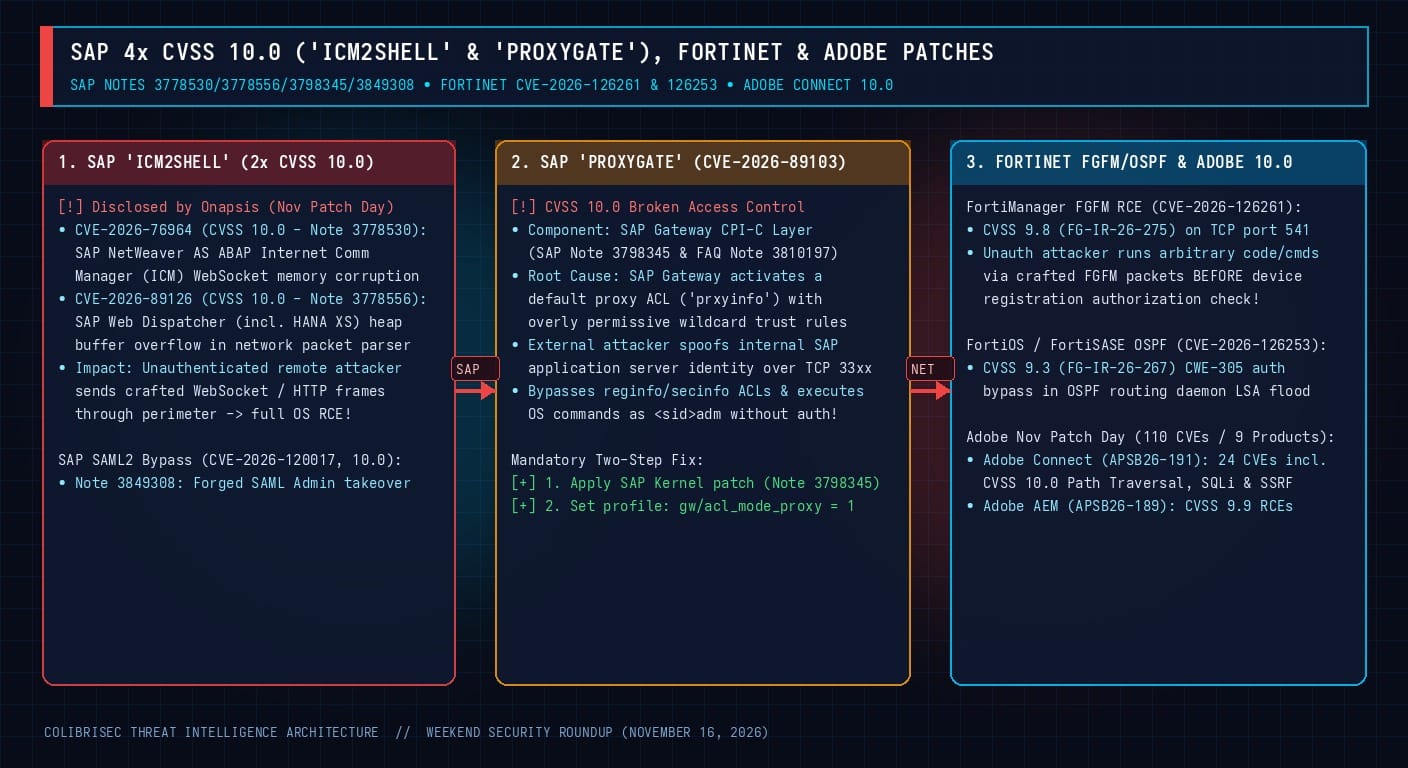
ICM2SHELL— Unauthenticated WebSocket Memory Corruption RCE (CVE-2026-76964 & CVE-2026-89126, CVSS 10.0): Discovered by Onapsis, these flaws affect the Internet Communication Manager (ICM) in SAP NetWeaver AS ABAP (Note3778530) and SAP Web Dispatcher / SAP HANA XS (Note3778556). Because ICM and Web Dispatcher sit at the perimeter terminating inbound HTTP/HTTPS and WebSocket connections, an unauthenticated remote attacker can send specially crafted WebSocket frames that trigger heap memory corruption in the network packet parser—achieving pre-authentication OS command execution without ever touching ABAP application authentication.PROXYGATE— SAP Gateway DefaultprxyinfoACL Bypass (CVE-2026-89103, CVSS 10.0): Tracked under SAP Note3798345(and FAQ Note3810197), the SAP Gateway CPI-C layer activates a default proxy Access Control List (prxyinfo) containing permissive wildcard trust rules. An external unauthenticated attacker who can reach the SAP Gateway port (TCP33xx) can spoof the identity of a trusted internal SAP application server, bypassreginfoandsecinforestrictions, and execute arbitrary OS commands as<sid>adm. Crucially, applying the kernel patch alone is not enough: administrators must also set the profile parametergw/acl_mode_proxy = 1.- SAP NetWeaver SAML 2.0 Service Provider Signature Bypass (CVE-2026-120017, CVSS 10.0): Patched in Note
3849308, improper cryptographic validation allows an attacker to forge SAML 2.0 assertions and authenticate as any SAP user, including administrative accounts.
2. Fortinet FortiManager FGFM Pre-Auth RCE (CVE-2026-126261) & FortiOS OSPF Bypass (CVE-2026-126253)
Surfaced during internal AI-assisted vulnerability auditing, Fortinet disclosed two critical network infrastructure flaws:
- FortiManager
FGFMImproper Authorization RCE (CVE-2026-126261, CVSS 9.8,FG-IR-26-275): Affects FortiManager8.0.0,7.6.0–7.6.7,7.4.0–7.4.5, and7.2.0–7.2.8. An unauthenticated attacker with network reachability to the FortiGate-FortiManager management port (TCP 541) can send craftedFGFMprotocol messages that invoke privileged command handlers before device registration authorization is enforced. - FortiOS & FortiSASE OSPF LSA Authentication Bypass (CVE-2026-126253, CVSS 9.3,
FG-IR-26-267): An authentication bypass by primary weakness (CWE-305) in the OSPF routing daemon allows an adjacent attacker to inject forged Link State Advertisements (LSAs) and hijack enterprise routing tables.
# 1. SAP Gateway PROXYGATE (CVE-2026-89103 - Note 3798345) DEFAULT.PFL / Instance Profile Lock:
gw/acl_mode_proxy = 1
gw/acl_mode = 1

# 2. FortiManager FGFM (CVE-2026-126261): Restrict TCP 541 via local-in-policy to known FortiGate IPs
config system local-in-policy
    edit 1
        set intf "port1"
        set srcaddr "Trusted_FortiGate_Subnets"
        set dst port 541
        set protocol tcp
        set action accept
    next
    edit 2
        set intf "port1"
        set dst port 541
        set protocol tcp
        set action deny
    next
end
🧭
More Deep Dives from this Roundup:
CISA KEV & Hypervisor Wipers: Check Point Gaia LPE (CVE-2026-123039) to ESXi Wiper, UnrealIRCd (CVE-2026-114713), GPUStack & FreeSWITCH
MSP RMM Crisis: N-able N-central 33-Bug "Able2Shell", "4EverAble2Shell" Apache Axis RCE (CVE-2026-90436) & "Agent2Shell" Exploits
Microsoft Nov 2026 Patch Tuesday (1,235 CVEs) & Zero-Days: Outlook NTLMv2 Leak (CVE-2026-124194), Search/LDAP 9.8 RCEs & CLFS "SignDrop"
Web Servers, Browsers & Runtimes: Apache mod_http2 RCE (CVE-2026-119618), Chrome XML 0-Day (CVE-2026-125350) & Node.js TLS Key Leak
AI IDE & CI/CD Supply-Chain Attacks: Cursor x Fireworks AI Trojanized "Claude Code" Extension & GitHub "wfx-loot" Across 61,000+ Repos
Messaging Sandbox RCE & AI Lures: Telegram QuickJS Widget Escape ("WebRAT" Stealer) & 186 "TypoPrompting" ClickFix AI Domains
Operation Endgame Seizes 235 Servers, Nitori 37.62M Breach, Maersk 100GB & Inside the FAA / Microsoft 365 Outage Cyber Panic
November 16 Weekend CISO Defense Blueprint: Hardening Gaia OS, N-central, Outlook/CLFS, Apache 2.4.71, SAP 10.0 & AI/CI Pipelines
← Return to Weekly Overview: Full Roundup

