
Operation Endgame Seizes 235 Servers, Nitori 37.62M Breach, Maersk 100GB & Inside the FAA / Microsoft 365 Outage Cyber Panic

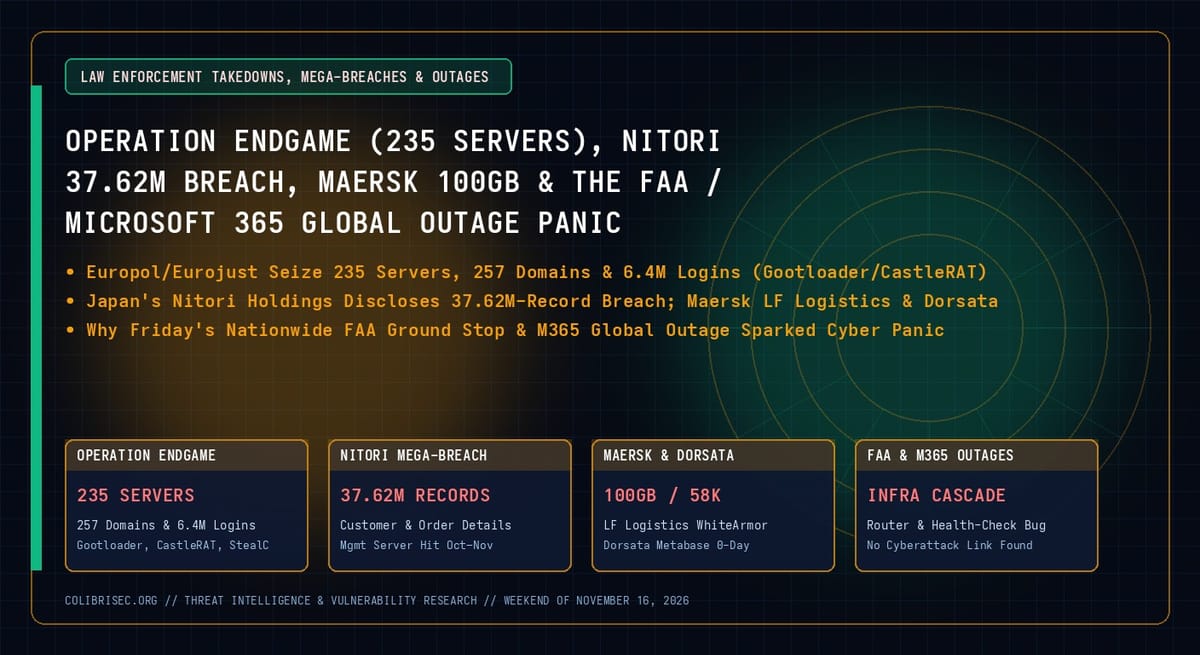
The weekend of November 13–16, 2026 paired one of the largest international cybercrime takedowns of the year with a 37.62-million-record retail breach in Japan and a dramatic Friday the 13th critical infrastructure scare in the United States. While Europol, Eurojust, and nine partner nations executed the latest wave of Operation Endgame—seizing 235 servers and 257 domains across Gootloader, CastleRAT, and StealC—Japanese retail giant Nitori Holdings disclosed unauthorized access affecting up to 37.62 million customer and corporate records, and White House, FAA, and Microsoft officials moved quickly to dispel viral rumors that Friday’s simultaneous FAA nationwide ground stop and worldwide Microsoft 365 outage were a coordinated cyberattack.
1. Operation Endgame (November 2026): 235 Servers, 257 Domains & 6.4M Stolen Logins Seized
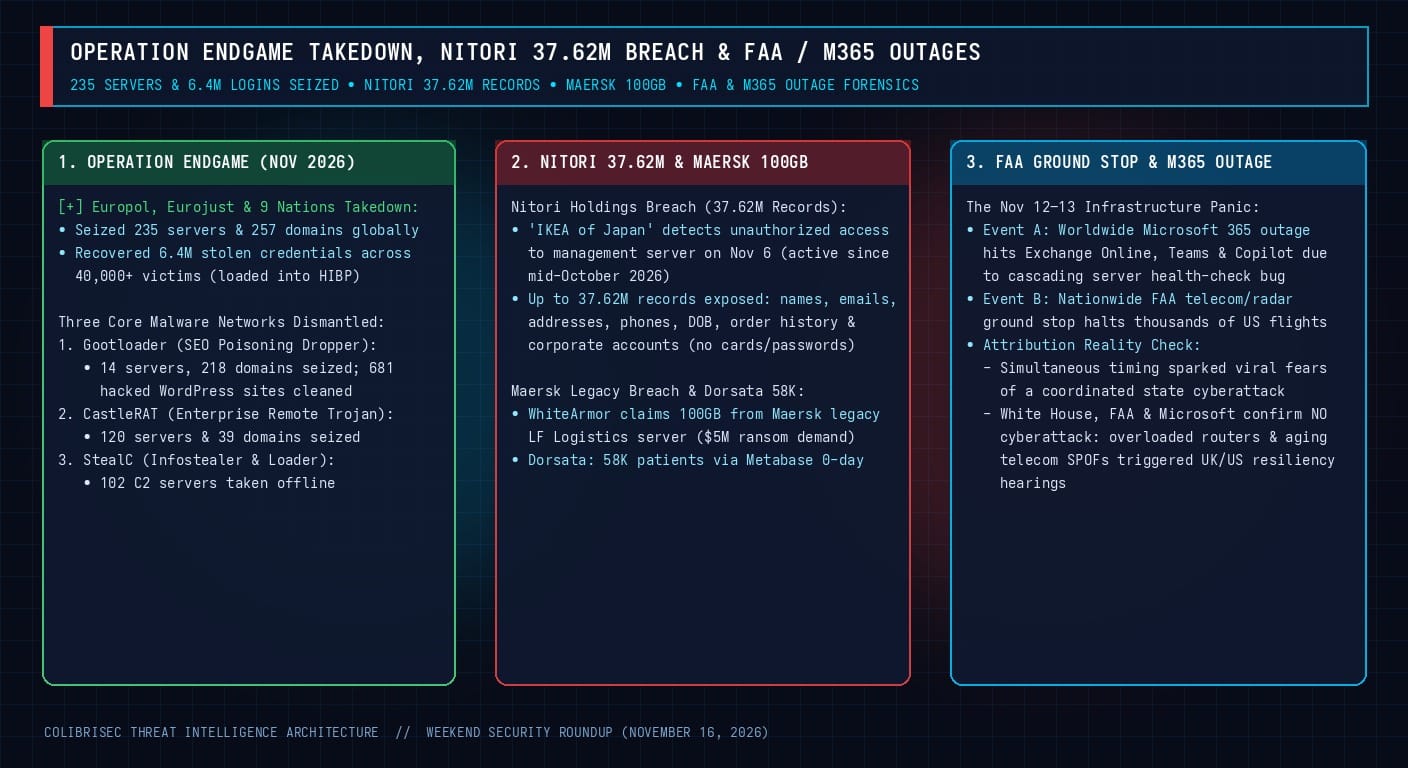
Coordinated by Europol, Eurojust, the U.S. DOJ, Germany’s BKA, the UK’s NCA, and law enforcement across nine nations, the November 2026 phase of Operation Endgame struck three foundational initial-access and infostealer ecosystems:
- Gootloader (SEO Poisoning & Legal-Document Lure Dropper): Law enforcement seized 14 core servers and 218 domains, while notifying and remediating 681 compromised WordPress websites used by Gootloader operators to poison search results for business contracts and legal agreements.
- CastleRAT (Enterprise Remote Access Trojan): Authorities seized 120 servers and 39 domains supporting the CastleRAT command-and-control network.
- StealC (Infostealer & Loader): An additional 102 C2 servers were taken offline, and investigators recovered 6.4 million stolen login credentials spanning more than 40,000 primary victims—feeding the dataset directly into Have I Been Pwned (HIBP) so organizations can force password resets.
2. Nitori Holdings Discloses 37.62-Million-Record Breach, Plus Maersk & Dorsata
- Nitori Holdings ("The IKEA of Japan") — Up to 37.62 Million Records Exposed: Nitori announced that on November 6, 2026, it detected unauthorized third-party access to an internal management server, with forensic logs indicating intruder activity dating back to mid-to-late October 2026. Up to 37.62 million total records across individual customers, app members, and corporate partners may have been exposed—including full names, membership IDs, email addresses, physical postal addresses, phone numbers, dates of birth, gender, and online purchase/order histories. Nitori confirmed that credit card details and login passwords were not stored in the affected files, notified Japan’s Personal Information Protection Commission (PPC) and police, and warned customers against targeted delivery-scam phishing.
- Maersk 100GB Legacy System Claim (
WhiteArmor) & Dorsata 58K Healthcare Breach: Extortion actor WhiteArmor demanded $5 million after claiming to exfiltrate 100GB of customs, waybill, and financial data from a local legacy system originally belonging to LF Logistics (acquired by A.P. Moller - Maersk in 2022); Maersk confirmed its core global shipping networks and customer APIs were unaffected. In healthcare, maternity EHR vendor Dorsata disclosed a breach affecting 58,000 patients after attackers exploited a zero-day in an analytics server running Metabase.
3. The Friday November 13 "Cyberattack vs. Outage" Panic: FAA Ground Stop & Microsoft 365
Between November 12 and November 14, two massive operational disruptions overlapped: a worldwide Microsoft 365 outage that degraded Exchange Online, Microsoft Teams, and Copilot (triggered by an internal server health-check processing bug that cascaded across load-balanced clusters), and a nationwide FAA telecommunications and radar ground stop on Friday, November 13 that halted thousands of U.S. flights. Because the two events struck simultaneously, social media and initial news alerts ignited fears of a coordinated nation-state cyberattack. However, the White House, the FAA, and Microsoft confirmed that no cyberattack or foul play occurred, attributing the FAA ground stop to overloaded network routers and aging telecommunications infrastructure—an incident that immediately prompted UK and U.S. lawmakers to call for mandatory national resilience stress-testing.

