
November 16 Weekend CISO Defense Blueprint: Hardening Gaia OS, N-central, Outlook/CLFS, Apache 2.4.71, SAP 10.0 & AI/CI Pipelines

📌
Security Roundup Series: Weekend of November 16, 2026 • 9 min read deep dive
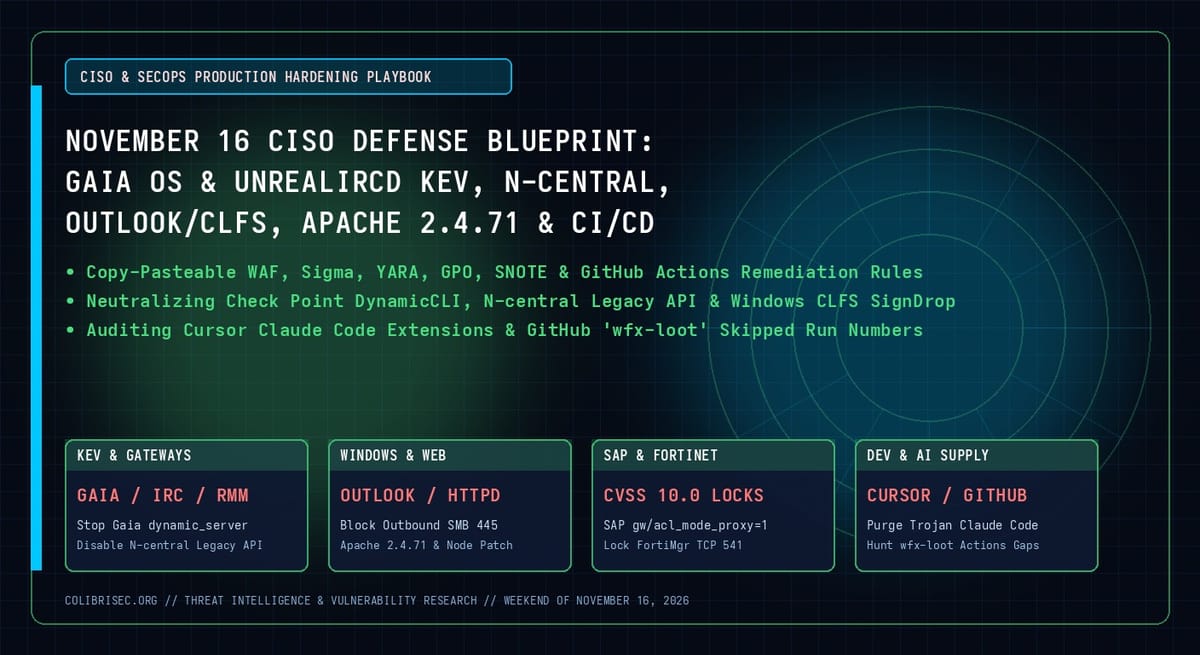
To help Security Operations Centers (SOCs), Managed Service Providers, and infrastructure engineering teams operationalize every disclosure from the November 16, 2026 Weekend Security Roundup, this blueprint consolidates copy-pasteable hardening commands, WAF/firewall rules, SAP profile locks, and CI/CD forensic checks mapped by asset tier.
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-123039, CVE-2026-114713, CVE-2026-90436, CVE-2026-124194, CVE-2026-119618, CVE-2026-89103 & CVE-2026-126261 (Defense-in-Depth Hardening, Virtual Patching, Socket Lockdown & Secret Rotation)
Severity: MANDATORY MONDAY MORNING REMEDIATION PLAYBOOK (CVSS 9.8 – 10.0 Across Perimeter Gateways, RMMs, Web Servers, ERP Systems & Developer Pipelines)
Status: Action Required Across Enterprise Production Environments
Affected Systems: Check Point Gaia OS, UnrealIRCd, N-able N-central, Microsoft Outlook/Exchange/LDAP/CLFS, Apache httpd, Chrome, Node.js, SAP, Fortinet, Cursor & GitHub Actions
Fixed In: Consolidated Vendor Updates & Compensating Controls Below
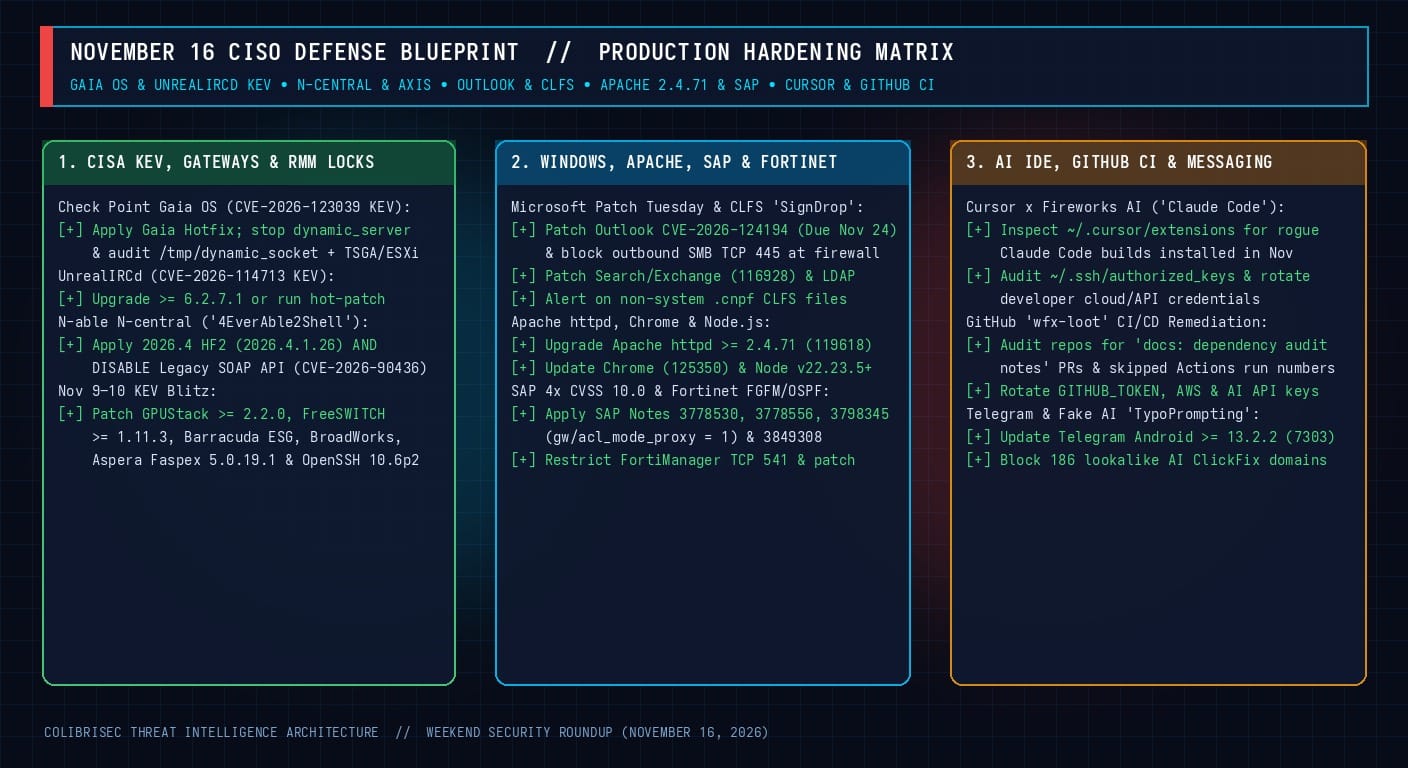
Tier 1: Check Point Gaia OS (CVE-2026-123039), UnrealIRCd (CVE-2026-114713) & N-central (CVE-2026-90436)
# 1. Check Point Gaia OS (CVE-2026-123039 - CISA KEV):
# Apply Check Point's Gaia OS Hotfix immediately. If a maintenance window is pending,
# stop dynamic_server, remove the world-writable socket, and hunt for TSGA/TSProxy:
tellpm process:dynamic_server
killall -9 dynamic_server 2>/dev/null
rm -f /tmp/dynamic_socket
find / -name "*TSGA*" -o -name "*TSProxy*" -o -name "*destroy_v6*" -o -name "DREAM_ANNEXATION.txt" 2>/dev/null

# 2. UnrealIRCd (CVE-2026-114713 - CISA KEV):
# Upgrade to UnrealIRCd 6.2.7.1+ or apply the live hot-patch bundle:
./unrealircd hot-patch bundle-20261107

# 3. N-able N-central "4EverAble2Shell" (CVE-2026-90436):
# Step A: Upgrade to N-central 2026.4 Hotfix 2 (build 2026.4.1.26)
# Step B: Disable the Legacy SOAP API in Administration -> User Management
# Step C: Block external requests containing SOAP Fault exceptionName gadgets at Nginx/WAF:
# if ($request_body ~* "exceptionName") { return 403; }
Tier 2: Microsoft Patch Tuesday (CVE-2026-124194, CVE-2026-116928) & Windows CLFS "SignDrop"
# 1. Block Outbound SMB (TCP 445/139) & WebDAV to Neutralize Outlook CVE-2026-124194 NTLMv2 Leaks
New-NetFirewallRule -DisplayName "ColibriSec-Block-Outbound-SMB" -Direction Outbound -Protocol TCP -RemotePort 445,139 -Action Block
Stop-Service -Name "WebClient" -Force
Set-Service -Name "WebClient" -StartupType Disabled

# 2. Detect Windows CLFS "SignDrop" Zero-Day (.blf / .cnpf Creation by Non-System Users)
# Alert in EDR/Sysmon (Event ID 11 FileCreate) when TargetFilename ends with .cnpf or .blf
# inside C:Users*, C:ProgramData*, or C:WindowsTemp*
Tier 3: Apache mod_http2 (CVE-2026-119618), Node.js (CVE-2026-123864), SAP CVSS 10.0 & FortiManager
# 1. Upgrade Apache HTTP Server to 2.4.71+ (CVE-2026-119618, CVSS 9.8)
# And upgrade Node.js to v22.23.5+, v24.22.3+, or v26.13.1+ (CVE-2026-123864 TLS Key Leak)
httpd -v && node -v

# 2. SAP NetWeaver & Gateway 4x CVSS 10.0 Remediation:
# - Apply SAP Notes 3778530 & 3778556 (ICM2SHELL: CVE-2026-76964 & CVE-2026-89126)
# - Apply SAP Note 3798345 AND set gw/acl_mode_proxy = 1 in DEFAULT.PFL (PROXYGATE: CVE-2026-89103)
# - Apply SAP Note 3849308 (SAML2 Signature Bypass: CVE-2026-120017)

# 3. Audit Developer Workstations (Cursor Claude Code) & GitHub Actions ("wfx-loot")
# Rotate any AWS, GCP, Azure, GitHub, OpenAI, or Anthropic API keys exposed in repositories
# where sequential GitHub Actions run_number gaps or "docs: dependency audit notes" PRs appear.
🧭
More Deep Dives from this Roundup:
CISA KEV & Hypervisor Wipers: Check Point Gaia LPE (CVE-2026-123039) to ESXi Wiper, UnrealIRCd (CVE-2026-114713), GPUStack & FreeSWITCH
MSP RMM Crisis: N-able N-central 33-Bug "Able2Shell", "4EverAble2Shell" Apache Axis RCE (CVE-2026-90436) & "Agent2Shell" Exploits
Microsoft Nov 2026 Patch Tuesday (1,235 CVEs) & Zero-Days: Outlook NTLMv2 Leak (CVE-2026-124194), Search/LDAP 9.8 RCEs & CLFS "SignDrop"
Web Servers, Browsers & Runtimes: Apache mod_http2 RCE (CVE-2026-119618), Chrome XML 0-Day (CVE-2026-125350) & Node.js TLS Key Leak
Enterprise ERP & Firewall Megapatches: SAP 4x CVSS 10.0 ("ICM2SHELL" & "PROXYGATE"), Fortinet FGFM/OSPF & Adobe Connect/AEM
AI IDE & CI/CD Supply-Chain Attacks: Cursor x Fireworks AI Trojanized "Claude Code" Extension & GitHub "wfx-loot" Across 61,000+ Repos
Messaging Sandbox RCE & AI Lures: Telegram QuickJS Widget Escape ("WebRAT" Stealer) & 186 "TypoPrompting" ClickFix AI Domains
Operation Endgame Seizes 235 Servers, Nitori 37.62M Breach, Maersk 100GB & Inside the FAA / Microsoft 365 Outage Cyber Panic
← Return to Weekly Overview: Full Roundup

