
CISA KEV & Hypervisor Wipers: Check Point Gaia LPE (CVE-2026-123039) to ESXi Wiper, UnrealIRCd (CVE-2026-114713), GPUStack & FreeSWITCH

Between November 9 and November 13, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a wave of actively exploited vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog under Binding Operational Directive (BOD) 26-04. Leading Friday’s November 13 additions are CVE-2026-123039—a zero-day local privilege escalation in Check Point Gaia OS that threat actors chained with perimeter web exploits to deploy root backdoors and wipe downstream VMware ESXi hypervisors—and CVE-2026-114713, an actively exploited server-command injection flaw in UnrealIRCd, alongside critical KEV mandates for GPUStack, SignalWire FreeSWITCH, Barracuda ESG, Cisco BroadWorks, and IBM Aspera Faspex.
CVE-2026-123039, CVE-2026-114713, CVE-2026-102895, CVE-2026-116779 & CVE-2026-116606 (CWE-276 (Incorrect Permissions), CWE-140 (Delimiter Neutralization), CWE-287 & CWE-94)
Severity: CRITICAL / HIGH (Actively Exploited CISA KEV Additions) (CVSS 7.8 (Gaia OS) / 8.6 (UnrealIRCd) / 9.8 (GPUStack, FreeSWITCH & Faspex))
Status: Actively Exploited in the Wild — Added to CISA KEV (Nov 9–13, 2026)
Affected Systems: Check Point Gaia OS Gateways/Management; UnrealIRCd 6.0.0–6.2.7; GPUStack < 2.2.0; FreeSWITCH < 1.11.3; Barracuda ESG
Fixed In: Check Point Gaia Hotfix; UnrealIRCd 6.2.7.1+; GPUStack 2.2.0; FreeSWITCH 1.11.3; Aspera Faspex 5.0.19.1
1. Root Cause & Kill Chain: Check Point Gaia OS DynamicCLI LPE (CVE-2026-123039) to VMware ESXi destroy_v6 Wiper
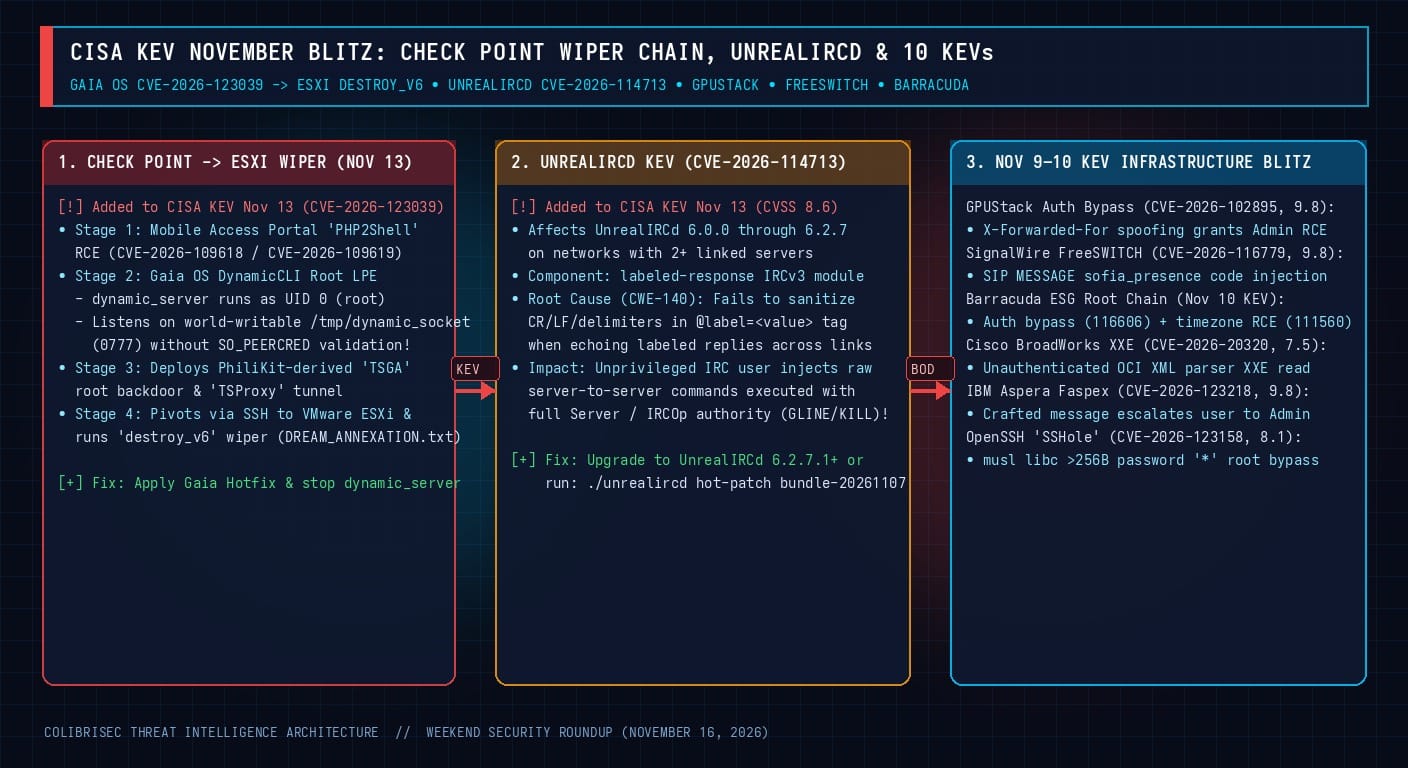
Incident responders tracking destructive intrusions across enterprise networks detailed a four-stage attack chain that transforms an unpatched Check Point Security Gateway into a launchpad for hypervisor destruction:
- Stage 1 — Initial Web Access via Mobile Access Portal (
PHP2Shell): Attackers target internet-exposed Check Point Security Gateways with the Mobile Access blade enabled, exploiting PHP engine vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to gain unprivileged command execution under the web portal service account and drop an initial staging webshell. - Stage 2 — Gaia OS
DynamicCLIUnauthenticated Socket Root LPE (CVE-2026-123039): On Gaia OS, theDynamicCLIdaemon (dynamic_server) executes withUID 0 (root)privileges and binds a local UNIX domain socket at/tmp/dynamic_socketwith world-writable permissions (srwxrwxrwx/0777). Critically,dynamic_serverfails to callgetsockopt(fd, SOL_SOCKET, SO_PEERCRED, ...)or verify client tokens before parsing and executing administrative CLI requests—allowing any local low-privileged user to send a crafted IPC payload to/tmp/dynamic_socketand execute arbitrary commands asroot. - Stage 3 — Persistent Backdooring with
TSGA&TSProxy: Once elevated toroot, the operators deployTSGA(a modified Check Point variant of thePhiliKitbackdoor framework previously observed on Ivanti appliances) alongsideTSProxy, establishing a covert SOCKS/TCP tunnel from the perimeter gateway into internal infrastructure management VLANs. - Stage 4 — SSH Pivot & VMware ESXi
destroy_v6Wiper Execution: Harvesting SSH keys and administrator credentials stored on or passing through the gateway, the attackers pivot over SSH to internal VMware ESXi hosts and execute a custom Linux/ESXi wiper binary nameddestroy_v6. The wiper terminates running guest VMs viaesxcli, overwrites VMFS volume headers and.vmdkflat files, and drops a ransom/sabotage note namedDREAM_ANNEXATION.txt.
2. Protocol Mechanics: UnrealIRCd labeled-response Injection (CVE-2026-114713) & the Nov 9–10 KEV Blitz
Added to CISA KEV alongside Check Point on November 13, CVE-2026-114713 (CVSS 8.6) targets UnrealIRCd 6.0.0 through 6.2.7 on networks with two or more linked IRC servers. When a client sends a command tagged with an IRCv3 @label=... message tag, the labeled-response module echoes that label across server-to-server links without stripping or neutralizing protocol delimiters. By crafting a malicious @label payload containing raw server-to-server protocol framing, an ordinary unprivileged user can inject inter-server commands that linked servers execute with full Server / IRCOp authority (enabling arbitrary KILL, GLINE, or network takeover).
# 1. Check Point Gaia OS (CVE-2026-123039): Inspect /tmp/dynamic_socket & stop dynamic_server workaround
ls -la /tmp/dynamic_socket
ps aux | grep -E "dynamic_server|TSGA|TSProxy"

# Emergency workaround on Gaia OS if hotfix cannot be applied immediately:
tellpm process:dynamic_server
killall -9 dynamic_server 2>/dev/null
rm -f /tmp/dynamic_socket

# 2. UnrealIRCd (CVE-2026-114713): Apply official hot-patch without restarting IRCd
cd /home/ircd/unrealircd
./unrealircd hot-patch bundle-20261107

# 3. SignalWire FreeSWITCH (CVE-2026-116779): Disable SIP MESSAGE chat parsing in Sofia profiles
grep -rn "enable-chat" /etc/freeswitch/sip_profiles/
# Set <param name="enable-chat" value="false"/> and reload mod_sofia:
fs_cli -x "reload mod_sofia"
3. Summary of the November 9–10 Infrastructure & Telecom KEV Additions
- GPUStack Authentication Bypass (CVE-2026-102895, CVSS 9.8): Versions prior to
2.2.0trust spoofed loopback/forwarded headers, allowing unauthenticated attackers to obtain built-in Admin access, mint API tokens, and execute arbitrary commands across AI GPU worker nodes. - SignalWire FreeSWITCH SIP RCE (CVE-2026-116779, CVSS 9.8): Code injection inside
sofia_presence_handle_sip_i_message()lets unauthenticated SIPMESSAGEpackets invoke internal FreeSWITCH API commands (fixed in1.11.3). - Barracuda ESG Root Exploit Chain (CVE-2026-116606 & CVE-2026-111560): Attackers chain an unauthenticated backup-import authentication bypass (
CVE-2026-116606, CVSS 9.3) with shell metacharacter injection in the timezone configuration parameter (CVE-2026-111560, CVSS 8.6). - Cisco BroadWorks XXE (CVE-2026-20320) & IBM Aspera Faspex (CVE-2026-123218, CVSS 9.8): Unauthenticated XXE file read in BroadWorks OCI XML parsing, and crafted message privilege escalation to Admin in Aspera Faspex
5.0.0–5.0.19(fixed in5.0.19 Patch Level 1).

