
Corporate & Legal Extortion Wave: SilentRansomGroup Targets Susman Godfrey LLP, Qilin Hits Proterial (Hitachi Metals) & Rhysida Academic Breaches

Between October 28 and October 30, 2026, ransomware and extortion leak portals registered a sharp escalation against two of the highest-value verticals in the global economy: elite U.S. litigation law firms and tier-one Japanese industrial materials manufacturers. On October 30, the extortion syndicate SilentRansomGroup (SRG)—tracked as Luna Moth and Chatty Spider—claimed responsibility for breaching powerhouse U.S. trial law firm Susman Godfrey LLP alongside additional corporate victims. Just 24 hours earlier, on October 29, the Qilin ransomware group added Japanese manufacturing giant Proterial, Ltd. (formerly Hitachi Metals) to its leak site, while Rhysida and N0n listed international higher-education targets including INTI International University and Colleges. Together with CrowdStrike’s disclosure this week of Warp Panda targeting U.S. law firms via ESXi zero-days, legal and industrial CISOs face an unprecedented pincer movement of state-sponsored espionage and financially motivated extortion.
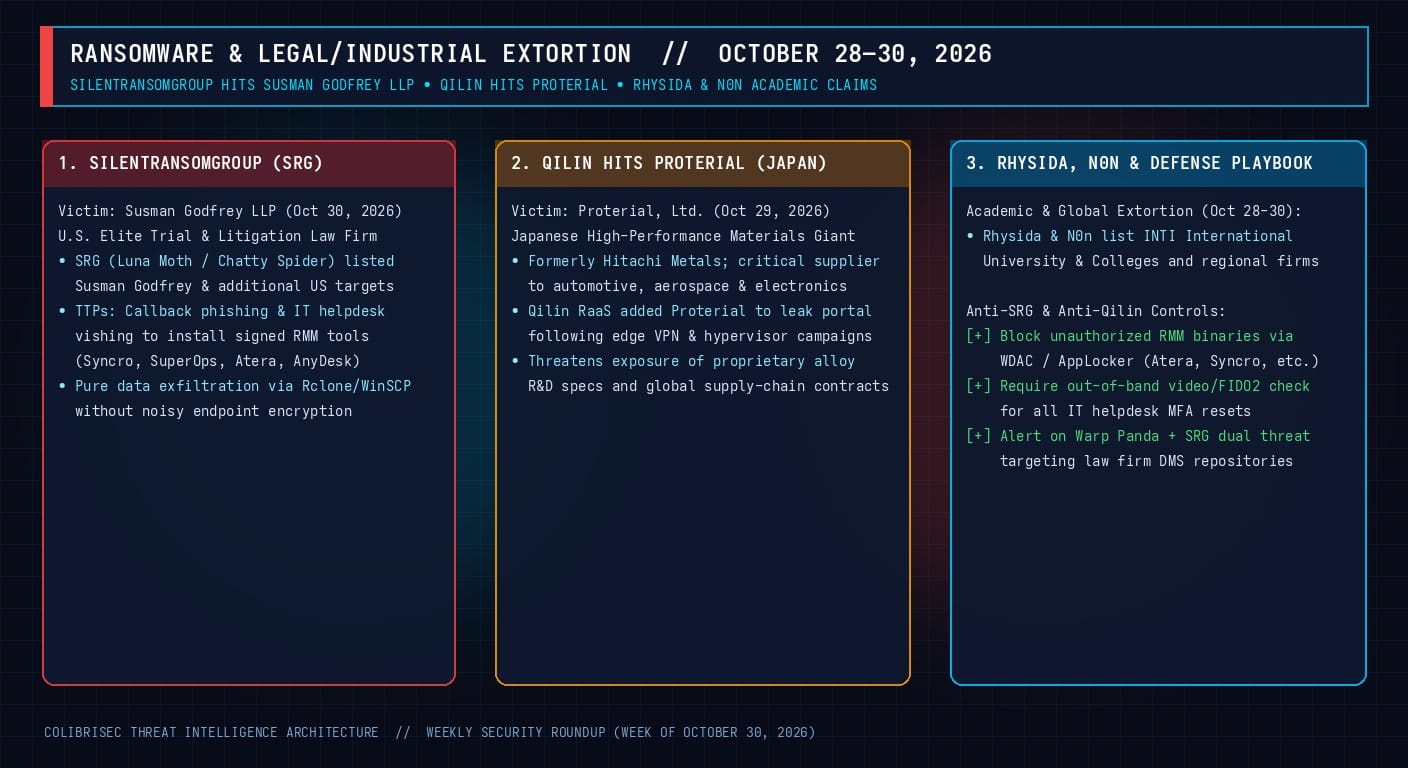
1. SilentRansomGroup (SRG) Claims Susman Godfrey LLP: How "Encryptionless" Law Firm Extortion Works
Susman Godfrey LLP is one of the most prominent commercial litigation and trial law firms in the United States, representing Fortune 500 corporations in multibillion-dollar antitrust, intellectual property, and securities disputes. Why are elite law firms the number-one target for both SilentRansomGroup (SRG) and state-sponsored groups like Warp Panda? Because a single law firm’s Document Management System (DMS—such as iManage or NetDocuments) holds the unredacted M&A blueprints, source-code exhibits, and regulatory defense strategies of hundreds of corporate clients simultaneously.
Inside SilentRansomGroup’s (Luna Moth) Vishing & RMM Tradecraft
Unlike traditional ransomware affiliates that deploy noisy file-encrypting binaries, SilentRansomGroup operates a stealthy, human-driven social engineering and living-off-the-land RMM playbook designed to evade endpoint behavioral blockers:
- Callback Phishing & Helpdesk Impersonation: SRG operators send targeted emails (or place direct voice calls impersonating internal IT support) to attorneys, paralegals, and legal secretaries regarding urgent MFA re-enrollment or software updates.
- Abusing Legitimate Signed RMM Binaries: Rather than dropping custom malware, the operator guides the user to download a validly signed, commercial Remote Monitoring and Management (RMM) installer—most frequently Syncro, SuperOps, Atera, Zoho Assist, AnyDesk, or ScreenConnect. Because these binaries carry valid Authenticode/Apple Developer signatures, standard antivirus policies allow them to execute.
- Silent Exfiltration via Rclone & WinSCP: Once unattended remote access is established, SRG operators install a second redundant RMM tool in the background, harvest browser session cookies and DMS tokens, and use Rclone or WinSCP to stream hundreds of gigabytes of litigation files directly to attacker-controlled cloud buckets before delivering an extortion demand.
2. Qilin Ransomware Targets Proterial (Formerly Hitachi Metals)
On Thursday, October 29, 2026, the Qilin Ransomware-as-a-Service (RaaS) syndicate listed Proterial, Ltd. on its dark-web extortion portal. Headquartered in Tokyo and known globally as Hitachi Metals prior to its 2023 rebranding, Proterial is a foundational supplier of high-performance specialty steels, neodymium rare-earth magnets, aircraft engine components, and semiconductor manufacturing materials.
Qilin (tracked by Unit 42 as Spikey Scorpius) has spent October 2026 aggressively exploiting perimeter VPN appliances—including Palo Alto Networks GlobalProtect (CVE-2026-0257) and Fortinet gateways sourced from initial access brokers—before pivoting into VMware ESXi hypervisors to steal Domain Controller VMDKs and deploy Rust/Go encryptors across manufacturing and OT-adjacent networks.
Detection & Hardening Controls for Law Firms and Manufacturers
# 1. DNS / Firewall Blocklist: Block outbound connections to unapproved RMM infrastructure
# Add to enterprise DNS sinkhole / proxy deny list (exclude your single approved corporate RMM):
*.syncromsp.com
*.superops.ai
*.atera.com
*.zohoassist.com
*.anydesk.com
*.Splashtop.com

# 2. CrowdStrike / Defender / SIEM Query: Hunt for Rclone or WinSCP execution on attorney endpoints
event_simpleName=ProcessRollup2
| where FileName in ("rclone.exe", "winscp.exe", "Syncro.App.Runner.exe", "AteraAgent.exe")
Remediation & Prevention Playbook
- Enforce Strict RMM Allowlisting via WDAC / AppLocker / Jamf: Law firms and enterprises must explicitly block all commercial RMM executables and MSI installers except the single tool used by their internal IT department.
- Mandate Out-of-Band Video + FIDO2 Verification for Helpdesk Requests: Train attorneys and staff that IT support will never ask them to download an external remote-support executable via phone or email, and require live video verification for any MFA device reset.
- Apply Conditional Access & Mass-Download Limits on Legal DMS Platforms: Configure iManage / NetDocuments / SharePoint to require hardware-bound FIDO2 passkeys and automatically suspend any user session that downloads more than 500 matter documents within a 15-minute window.

