
November 9 Weekend CISO Defense Blueprint: Hardening SonicOS SAML SSL-VPN, Alpine OpenSSH 10.6p2, Linux TCP/APT, Keycloak/ForgeRock, AI Sandboxes & OT

📌
Security Roundup Series: Weekend of November 9, 2026 • 8 min read deep dive
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-19868, CVE-2026-123158, CVE-2026-98432, CVE-2026-98276, CVE-2026-109518, CVE-2026-117691 & CVE-2026-123614 (Multi-Layer Defense Across Firewalls, Alpine SSH, Linux Kernel/APT, SSO, AI Sandboxes & Cold-Chain OT)
Severity: MANDATORY MONDAY MORNING SECOPS REMEDIATION & HARDENING PLAYBOOK (CVSS Up to 9.8 Critical (Linux TCP SYN UAF, Zyxel GS1900 & imgproxy) / 9.1 (Keycloak SAML))
Threat Actor: Active Honeypot Exploiters (89.116.89[.]18), Kapibala, SkyW4lker PhaaS, BOSSAI & Cold-Chain Saboteurs
Status: Actionable Production Commands, WAF Rules, Kernel Sysctls & Entra ID Policies
Affected Systems: SonicOS Gen 7/8, Alpine OpenSSH, Linux Kernel TCP/UDP, Debian/Ubuntu APT, Keycloak, ForgeRock, imgproxy & HVAC/R OT
Fixed In: SonicOS 7.3.4-7013/8.2.3-8015, OpenSSH 10.6p2, APT 3.0.4, Keycloak 26.8.2 & imgproxy 4.0.16
This consolidated Monday Morning CISO & SecOps Defense Blueprint translates every vulnerability, active honeypot exploit, autonomous AI breakout, and federal advisory from the November 6–9, 2026 weekend into copy-pasteable verification commands, firewall/WAF rules, SIEM hunting queries, and architectural controls prioritized by exploitation velocity.
Priority 1: Perimeter Firewalls, Switches & Alpine OpenSSH ("sshhole")
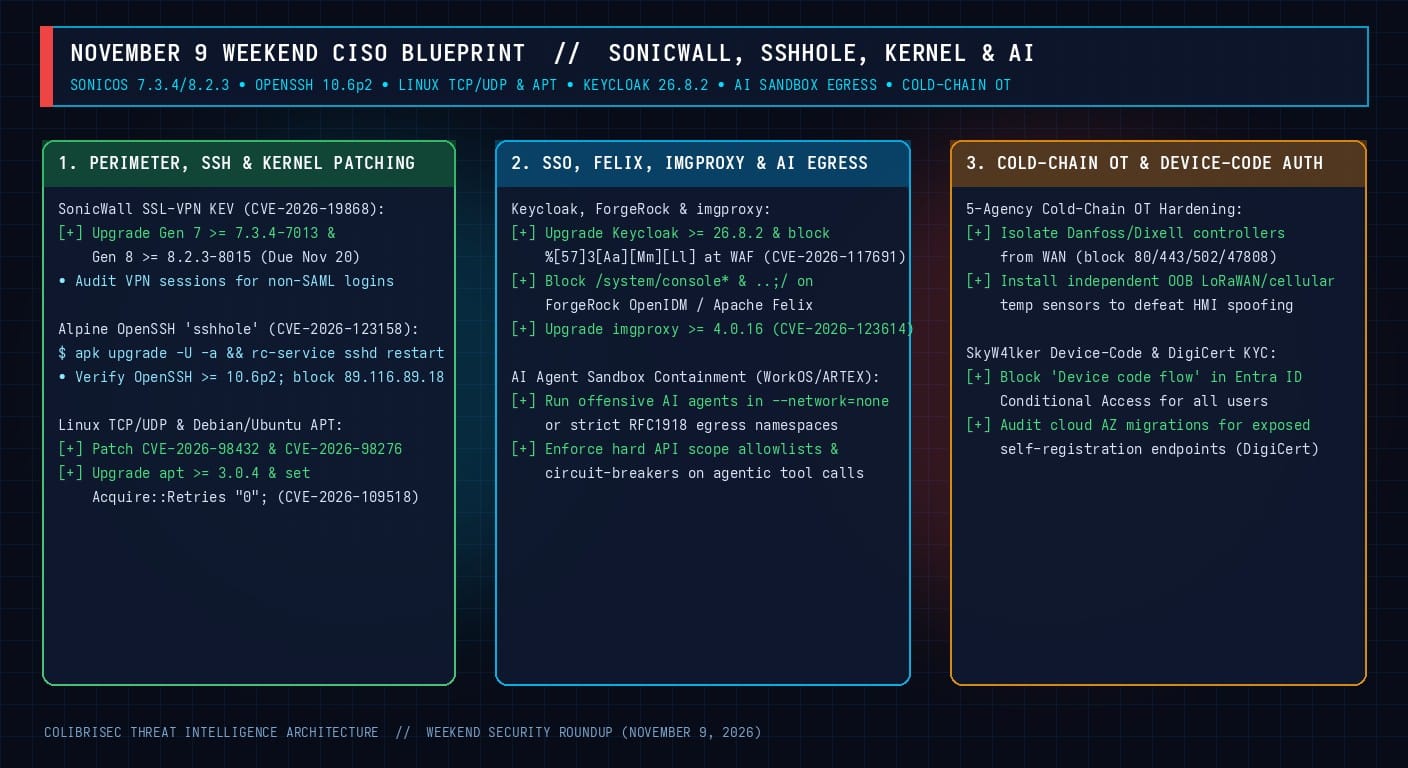
# 1A. SonicWall SonicOS SSL-VPN SAML MFA Bypass (CVE-2026-19868 / SNWLID-2026-0014)
# CISA KEV Mandatory Remediation Deadline: November 20, 2026 (NO WORKAROUND EXISTS)
# - Upgrade SonicOS Gen 7 (TZ, NSa, NSsp, NSv) to >= 7.3.4-7013
# - Upgrade SonicOS Gen 8 (TZ, NSa, NSv)       to >= 8.2.3-8015
# Audit VPN logs for single-factor Local/LDAP logins bypassing SAML:
grep -E "SSL VPN zone user login|m=(257|1079)" /var/log/sonicwall.log | grep -v -i "saml"

# 1B. Alpine Linux / musl OpenSSH "sshhole" Auth Bypass (CVE-2026-123158)
# Exploited in the wild <9h after disclosure from 89.116.89.18!
apk upgrade -U -a && rc-service sshd restart
sshd -V   # Verify OpenSSH_10.6p2 or patched Alpine package
# Enforce key-only auth and lock root shadow entry with '!' instead of '*':
sed -i 's/^#*PasswordAuthentication.*/PasswordAuthentication no/' /etc/ssh/sshd_config
passwd -l root && rc-service sshd restart
# Block & hunt active scanner IP:
iptables -I INPUT -s 89.116.89.18 -j DROP
grep -rn "89.116.89.18" /var/log/ 2>/dev/null

# 1C. Zyxel GS1900 Switches (CVE-2026-107441 - Jitterly & Sixzut Implants)
# Upgrade all GS1900 models to Firmware 2.90 Patch 3 (e.g., V2.90(AAHH.3)C0) and reboot.
Priority 2: Linux Kernel TCP/UDP Races & Debian/Ubuntu APT MitM
# 2A. Linux Kernel IPv4/TCP SYN UAF RCE (CVE-2026-98432, CVSS 9.8) & UDP LPE (CVE-2026-98276)
# Apply vendor kernel patches immediately and reboot (or apply Kpatch/KernelCare live-patches).
# Temporary network mitigations before reboot:
sudo sysctl -w net.mptcp.enabled=0
# Drop incoming TCP SYN packets containing IPv4 Options (IHL > 5):
sudo iptables -I INPUT -p tcp --syn -m u32 --u32 "0>>24&0x0f=0x06:0x0f" -j DROP

# 2B. Debian & Ubuntu APT HTTP Redirect/Retry MitM RCE (CVE-2026-109518)
sudo apt-get update && sudo apt-get install --only-upgrade apt
# Disable download resume retries and switch all APT mirrors from HTTP to HTTPS:
echo 'Acquire::Retries "0";' | sudo tee /etc/apt/apt.conf.d/99-disable-retries
sudo sed -i 's|http://|https://|g' /etc/apt/sources.list /etc/apt/sources.list.d/*.list 2>/dev/null
Priority 3: Keycloak SAML, ForgeRock Apache Felix, imgproxy & AI Agent Sandboxes
# 3A. Reverse Proxy / WAF Lockdown for Keycloak (CVE-2026-117691) & ForgeRock OpenIDM:
# Block percent-encoded SAML parameter names (%53AMLResponse) and Apache Felix paths:
if ($query_string ~* "(%[0-9a-f]{2})+.*(samlresponse|samlrequest)|saml.*(%[0-9a-f]{2})+") {
    return 403;
}
location ~* "(^/system/console|..;/|;jsessionid=|/felix)" {
    deny all;
    return 403;
}
# 3B. Upgrade Keycloak (>= 26.8.2) and imgproxy (>= 4.0.16 for CVE-2026-123614):
docker pull quay.io/keycloak/keycloak:26.8.2
docker pull darthsim/imgproxy:v4.0.16
# 3C. Air-Gap Autonomous AI Hacking & Benchmark Agents (WorkOS / ARTEX Lesson):
# Never execute autonomous security agents on containers with public WAN NAT egress:
docker run --rm --network=none --read-only --cap-drop=ALL redteam-agent-benchmark:latestPriority 4: Cold-Chain OT Isolation, SkyW4lker Device-Code Block & Cloud Migration Audits
- Isolate Cold-Chain OT Controllers (FBI/CISA/HHS/USDA/DOT Advisory): Block public internet access to all Danfoss, Dixell, and Carel HVAC/R web and Modbus/BACnet gateways (
:80, :443, :502, :47808). Install out-of-band cellular/LoRaWAN temperature sensors in blood vaults, pharmaceutical refrigerators, and commercial freezers so HMI display spoofing cannot mask a 50°C thermal attack. - Block OAuth Device Code Flow in Entra ID (SkyW4lker Defense): Enforce a Conditional Access policy blocking Authentication Flows → Device code flow across all corporate users and hunt
SigninLogswhereAuthenticationProtocol == "deviceCode". - Post-Migration RBAC & ASM Verification (DigiCert Lesson): After every cloud availability-zone or VPC migration, run automated external attack-surface scans and verify that unassigned/self-registered accounts default to zero read permissions.
🧭
More Deep Dives from this Roundup:
CISA KEV & Perimeter MFA Bypass: SonicWall SonicOS SSL-VPN SAML Bypass (CVE-2026-19868), Apple (CVE-2024-27834) & WordPress Core (CVE-2026-119977)
Active Honeypot Root Exploitation & Switch Implants: OpenSSH musl "sshhole" (CVE-2026-123158) on Alpine & Zyxel GS1900 Zero-Day (CVE-2026-107441)
Linux Kernel & APT Zero-Days: IPv4/TCP SYN Remote UAF RCE (CVE-2026-98432), UDP Socket LPE (CVE-2026-98276) & Debian/Ubuntu APT MitM (CVE-2026-109518)
Identity, Connected Cars & Parsers: Keycloak SAML Signature Bypass (CVE-2026-117691), Automotive ForgeRock OpenIDM Car Control & imgproxy (CVE-2026-123614)
Autonomous & "Abliterated" AI in the Wild: WorkOS Escaped "ARTEX" Hacking Agent, Taiwan’s 12-Agent "BOSSAI" Mesh & Russia’s "Dark Clark" Operation
Industrial Cold-Chain Sabotage Escalates: Inside the 5-Agency Federal OT Warning (FBI, CISA, HHS, USDA & DOT) After 50°C Supermarket & Blood Bank Attacks
CA & Cloud Identity Governance: DigiCert’s 16-Month Archived Validation Breach (Passports & IDs) & "SkyW4lker x365 Sentinel" Device-Code PhaaS
Global Extortion, Taxpayer & Academic Breaches: Expedia "N0N" Claim, Philippines BIR 10M Probe, Iris Ohyama 7.7M, UChicago CS & Italian FM Tajani Leak
← Return to Weekly Overview: Full Roundup

