
Industrial Cold-Chain Sabotage Escalates: Inside the 5-Agency Federal OT Warning (FBI, CISA, HHS, USDA & DOT) After 50°C Supermarket & Blood Bank Attacks

Following a destructive wave of operational technology (OT) cyberattacks that crippled commercial refrigeration systems across seven European countries between November 2 and November 5, 2026—and an earlier October wave that struck French grocery chains and blood storage facilities—five U.S. federal agencies (the FBI, CISA, HHS, USDA, and DOT) issued a joint Critical Infrastructure Warning over the weekend. The multi-agency alert warns that threat actors are actively scanning the public internet for exposed industrial and commercial cold-chain controllers, exploiting authentication bypasses and factory-default credentials to force freezers into heating/defrost modes up to 50°C (122°F) while simultaneously obscuring and spoofing temperature readings on operator displays so staff do not realize critical food, blood plasma, or biologics are spoiling until physical damage is irreversible.
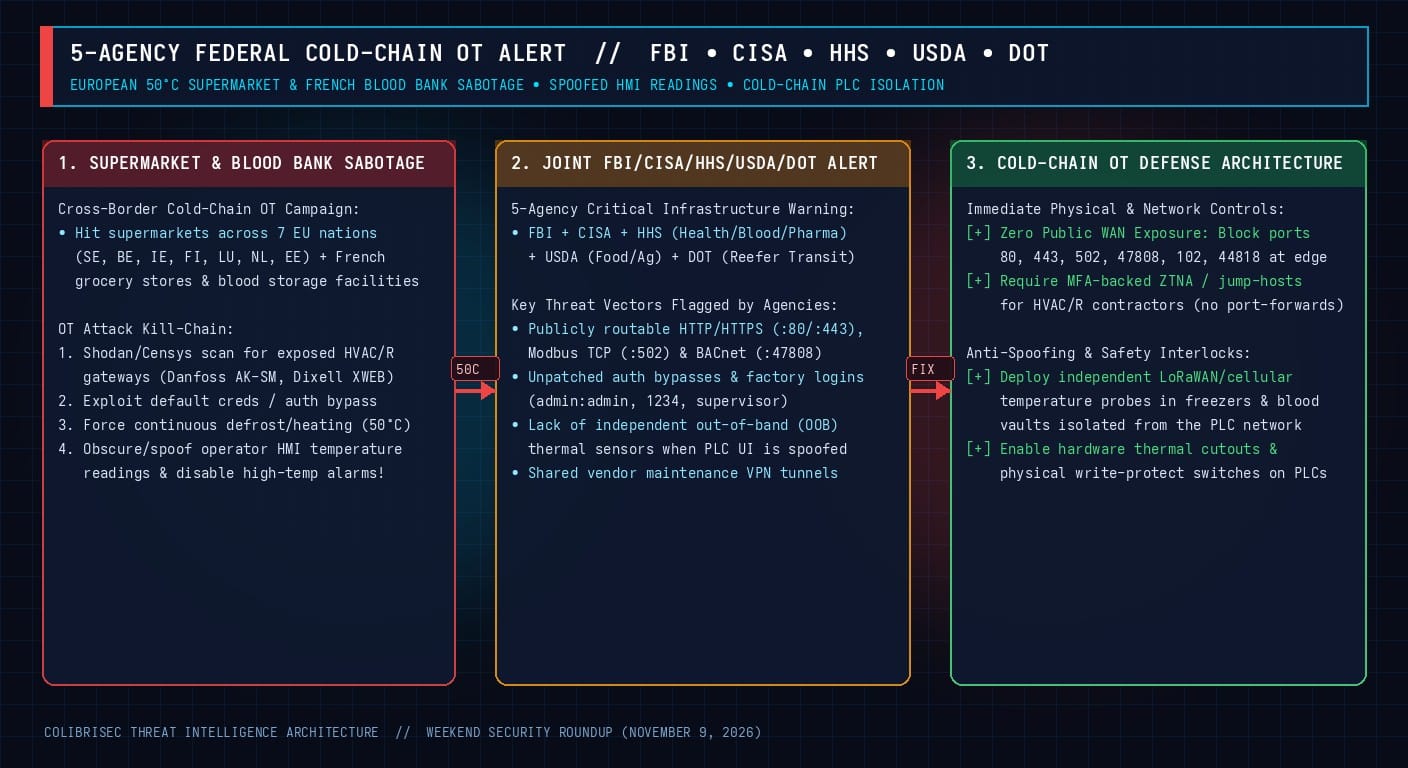
1. Technical Anatomy of the Cold-Chain OT Sabotage
Modern commercial supermarkets, pharmaceutical warehouses, blood banks, and refrigerated shipping terminals rely on centralized HVAC/R rack controllers and web-enabled supervisory gateways (such as Danfoss AK-SM 800/800A series, Emerson/Copeland Dixell XWEB 300D/500D/3000, and Carel PlantVisorPRO / boss) that bridge IT IP networks to downstream RS-485 Modbus RTU/TCP and BACnet field buses controlling compressor racks, expansion valves, and electric defrost heaters.
How Attackers Spoof Operator Displays While Heating Freezers to 50°C
The joint FBI, CISA, HHS, USDA, and DOT advisory highlights a particularly insidious technique observed in the European supermarket and French blood bank intrusions: attackers do not merely change a temperature setpoint—they manipulate the controller’s calibration offsets and display registers so local staff remain blind to the thermal spike:
- Initial Access via Exposed WAN Gateways & Auth Bypasses: Using Shodan and Censys queries for HTTP/HTTPS banners on ports
80,443,8080, and rawModbus TCP (:502)orBACnet (:47808), attackers log in using unrotated factory credentials (e.g.,admin:admin,supervisor,1234) or known web-interface authentication bypasses. - Forcing Continuous Defrost & Raising Cut-In Setpoints: The attacker writes to the controller’s holding registers or CGI configuration API to force all refrigeration zones into manual continuous electric/hot-gas defrost, shutting off cooling compressors and energizing heating elements until cabinet temperatures climb toward 50°C (122°F).
- Obscuring Readings & Silencing Alarms: Simultaneously, the attacker modifies the sensor calibration offset register (or freezes the HMI polling loop / sets alarm delay timers to
999 minutesand high-temp alarm thresholds to+60°C). As a result, a digital readout or central dashboard may continue showing a safe-18°Cor+4°C(for blood storage) while the physical interior of the vault or cabinet is actively baking!
2. Why Five Federal Agencies (FBI, CISA, HHS, USDA & DOT) Joined Forces
The inclusion of HHS, USDA, and DOT alongside the FBI and CISA reflects the systemic cross-sector risk of cold-chain sabotage:
- HHS (Healthcare & Public Health): Hospital blood banks, plasma fractionation centers, IVF clinics, and biologic/vaccine depots use the exact same commercial PLC gateways as grocery stores. A silent 6-hour thermal excursion with a spoofed HMI readout destroys irreplaceable blood supplies and life-saving medications.
- USDA (Food & Agriculture): Meatpacking plants, dairy processors, and regional grocery distribution centers face both massive financial spoilage and severe foodborne-pathogen safety hazards if thawed products are refrozen undetected.
- DOT (Transportation Systems): Intermodal refrigerated containers ("reefers"), cold-storage port terminals, and telematics-connected refrigerated truck fleets increasingly expose cellular/satellite management interfaces to the internet.
Mandatory Cold-Chain Hardening & Anti-Spoofing Controls
# 1. Immediate Perimeter Discovery — Scan Your Own External ASN/IP Space for Exposed HVAC/R Ports:
nmap -Pn -sT -p 80,443,502,102,47808,44818,8080,8443 --open -iL corporate_wan_ips.txt

# 2. Enforce Zero Public WAN Exposure at Store / Hospital / Warehouse Firewalls:
# Block all inbound WAN traffic to refrigeration VLANs and restrict outbound OT traffic:
iptables -I FORWARD -i wan0 -o vlan_ot_hvac -j DROP
iptables -I FORWARD -p tcp -m multiport --dports 502,47808,102,44818 -j DROP

# 3. Defeating HMI Display Spoofing (Physical & Out-of-Band Layer):
# - Deploy independent, battery-backed LoRaWAN or cellular temperature probes inside
#   every blood vault, pharma fridge, and supermarket freezer rack that report directly
#   to an isolated cloud/SMS alerting channel completely independent of the HVAC PLC.
# - Verify that physical bimetallic high-temperature limit thermostats (hardware cutouts)
#   are wired in series with defrost heater contactors so software cannot heat past +10°C.
