en

ColibriSec Weekend Security Roundup - November 16, 2026

News

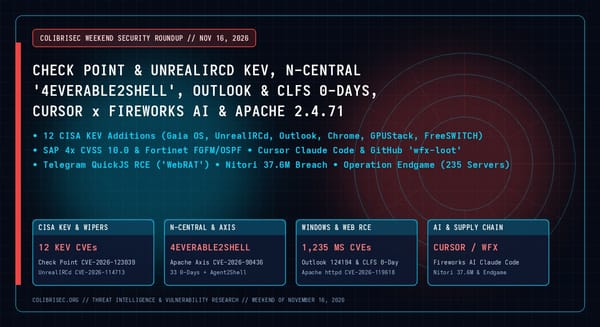
Security Roundup: Check Point & UnrealIRCd KEV, N-central "4EverAble2Shell", Outlook & CLFS 0-Days, Apache 2.4.71, Cursor AI & Nitori 37.6M Breach (Weekend Edition - November 16, 2026)

Executive Summary: The week and weekend culminating on November 16, 2026 delivered an extraordinary collision of perimeter-to-hypervisor destructive chains, MSP remote monitoring zero-days, record-shattering Patch Tuesday volumes, AI IDE supply-chain compromises, and critical infrastructure outage scares. On Friday (November 13), CISA added two actively exploited flaws to the Known Exploited

By James Luther
CISA KEV Check Point Gaia OS CVE-2026-123039 ESXi Wiper and UnrealIRCd CVE-2026-114713

News

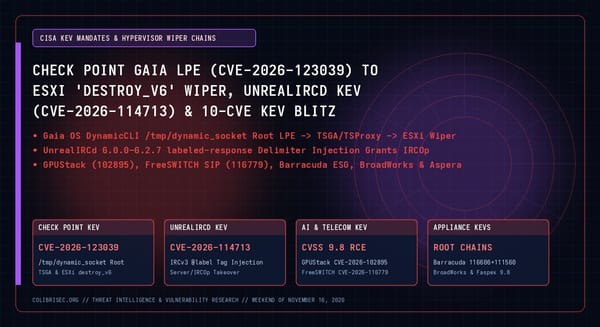
CISA KEV & Hypervisor Wipers: Check Point Gaia LPE (CVE-2026-123039) to ESXi Wiper, UnrealIRCd (CVE-2026-114713), GPUStack & FreeSWITCH

📌Security Roundup Series: Weekend of November 16, 2026 • 8 min read deep dive Between November 9 and November 13, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a wave of actively exploited vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog under Binding Operational Directive (BOD) 26-04. Leading

By James Luther
N-able N-central Able2Shell and 4EverAble2Shell CVE-2026-90436 Exploit Chain

News

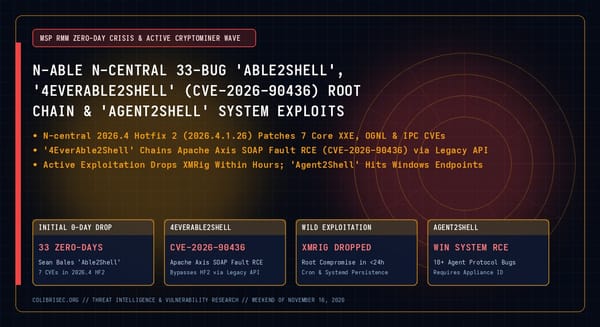
MSP RMM Crisis: N-able N-central 33-Bug "Able2Shell", "4EverAble2Shell" Apache Axis RCE (CVE-2026-90436) & "Agent2Shell" Exploits

📌Security Roundup Series: Weekend of November 16, 2026 • 8 min read deep dive Managed Service Providers (MSPs) and enterprise IT operations running on-premises N-able N-central remote monitoring and management (RMM) servers endured a relentless two-wave zero-day crisis between November 8 and November 15, 2026. After independent researcher Sean Bales (publishing

By James Luther
Microsoft November 2026 Patch Tuesday Outlook Zero-Day CVE-2026-124194 and Windows CLFS SignDrop

News

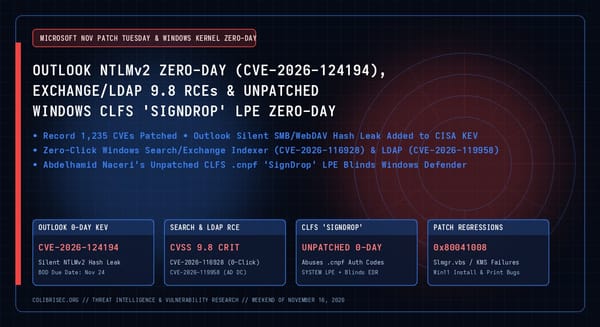
Microsoft Nov 2026 Patch Tuesday (1,235 CVEs) & Zero-Days: Outlook NTLMv2 Leak (CVE-2026-124194), Search/LDAP 9.8 RCEs & CLFS "SignDrop"

📌Security Roundup Series: Weekend of November 16, 2026 • 8 min read deep dive Microsoft’s November 2026 Patch Tuesday rollup shattered historical volume records—addressing between 1,093 and 1,235 CVEs across Microsoft and third-party components (including 64 Critical vulnerabilities)—while enterprise defenders simultaneously confronted an actively exploited Microsoft

By James Luther
SAP 4x CVSS 10.0 ICM2SHELL and PROXYGATE, Fortinet FGFM and Adobe Connect Patches

News

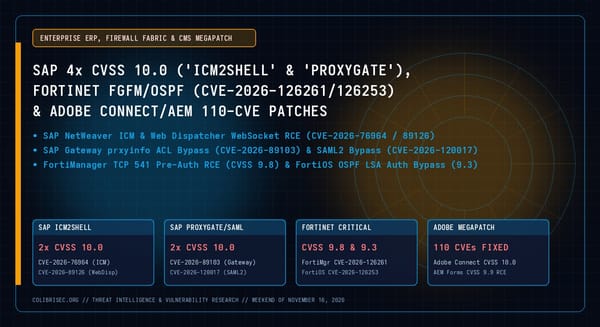
Enterprise ERP & Firewall Megapatches: SAP 4x CVSS 10.0 ("ICM2SHELL" & "PROXYGATE"), Fortinet FGFM/OSPF & Adobe Connect/AEM

📌Security Roundup Series: Weekend of November 16, 2026 • 8 min read deep dive Enterprise ERP administrators, network firewall engineers, and digital experience teams faced an unprecedented cluster of maximum-severity advisories this week: SAP patched four CVSS 10.0 vulnerabilities led by Onapsis’s ICM2SHELL and PROXYGATE disclosures; Fortinet published critical

By James Luther
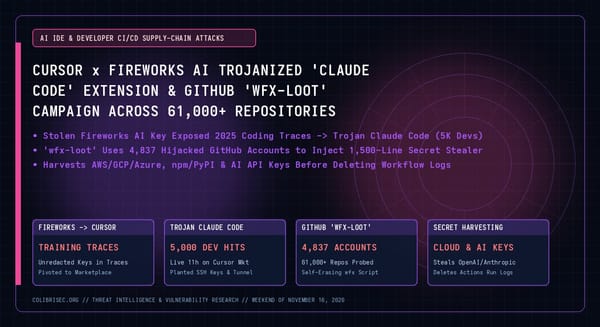
Cursor Fireworks AI Trojanized Claude Code Extension and GitHub wfx-loot Supply Chain Attack

News

AI IDE & CI/CD Supply-Chain Attacks: Cursor x Fireworks AI Trojanized "Claude Code" Extension & GitHub "wfx-loot" Across 61,000+ Repos

📌Security Roundup Series: Weekend of November 16, 2026 • 8 min read deep dive Two major software supply-chain disclosures this weekend underscored how threat actors are systematically targeting AI-assisted software development pipelines, IDE marketplaces, and CI/CD secret stores. First, AI coding platform Cursor published a detailed post-mortem revealing that a

By James Luther
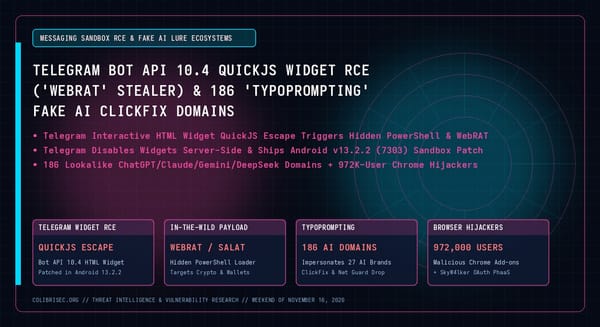
Telegram QuickJS Widget RCE WebRAT Stealer and 186 TypoPrompting Fake AI Domains

News

Messaging Sandbox RCE & AI Lures: Telegram QuickJS Widget Escape ("WebRAT" Stealer) & 186 "TypoPrompting" ClickFix AI Domains

📌Security Roundup Series: Weekend of November 16, 2026 • 7 min read deep dive Messaging platforms and AI browser workflows came under intense fire this weekend. Following Telegram’s rollout of Bot API 10.4—which introduced interactive HTML/JavaScript message widgets executing inside an embedded QuickJS sandbox—security researchers at

By James Luther