en
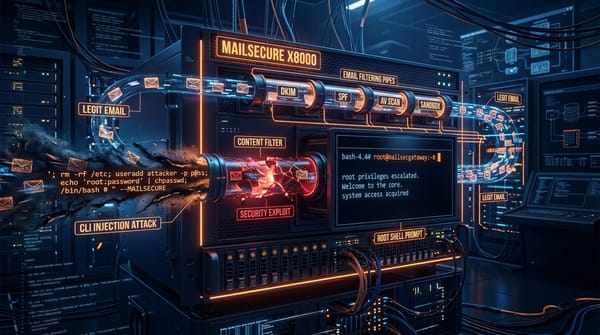
CVE-2026-66149 & CVE-2026-66150: SonicWall Email Security Appliance Code Injection & Root Execution
Analysis of CVE-2026-66149 and CVE-2026-66150 in SonicWall Email Security: CLI breakout mechanics, root privilege escalation, and patch details.

en
Analysis of CVE-2026-66149 and CVE-2026-66150 in SonicWall Email Security: CLI breakout mechanics, root privilege escalation, and patch details.
en
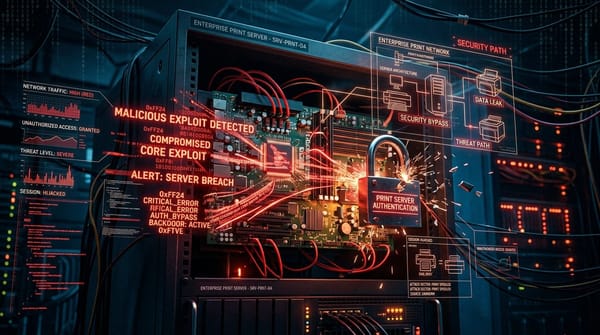
Technical teardown of the active PaperCut NG/MF pre-auth RCE zero-day flaw: root cause mechanics, process telemetry detection rules, and emergency hardening steps.
en
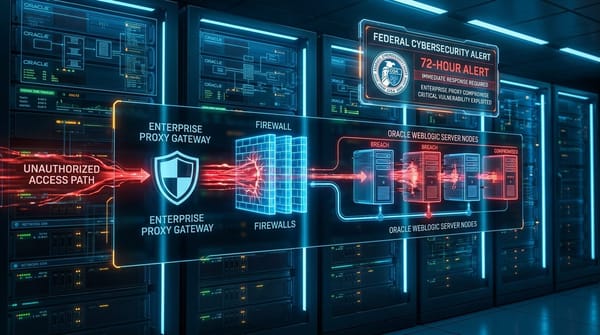
Deep dive into CVE-2026-21962: how threat actors bypass Oracle WebLogic reverse proxy security boundaries, and why CISA mandated an emergency 72-hour patch deadline.
en
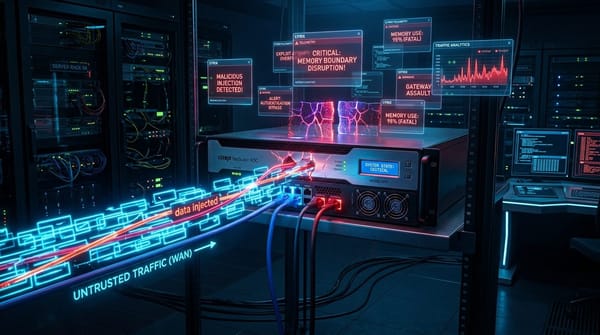
Technical breakdown of CVE-2026-8452 affecting Citrix NetScaler ADC and Gateway appliances: memory state failure, active exploitation telemetry, and remediation.
en
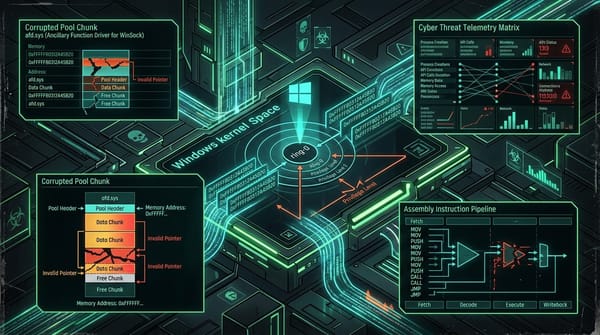
Technical deep dive into the actively exploited CVE-2026-68820 Windows kernel afd.sys zero-day: pool spraying, token manipulation, and Lazarus evasion tradecraft.
en
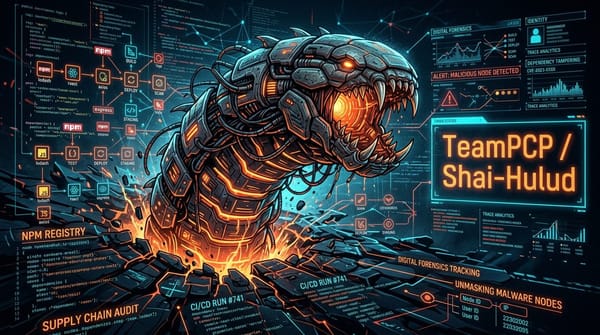
A forensic investigation has unmasked the operator behind TeamPCP and the Shai-Hulud supply chain worms as Ruben Thomson of Perth, Australia. Here is the full breakdown of the OPSEC blunders, C2 infrastructure, and transitive build-pipeline attacks.
en
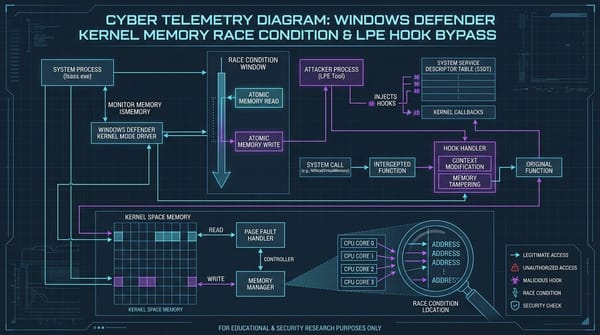
Threat briefing on the unpatched Windows Defender ShieldBreak zero-day (CVE-2026-69414) allowing local privilege escalation to SYSTEM.
en
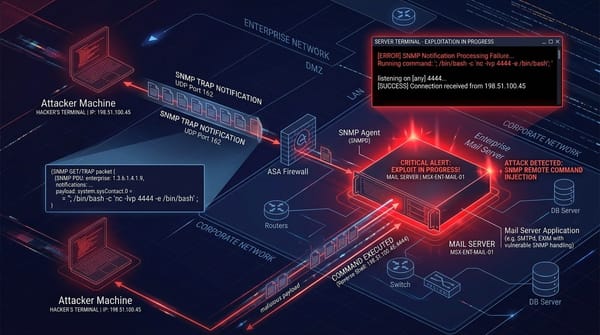
How threat actors exploit CVE-2026-73570 in Zimbra's SNMP service to achieve unauthenticated remote code execution on enterprise mail servers.
en
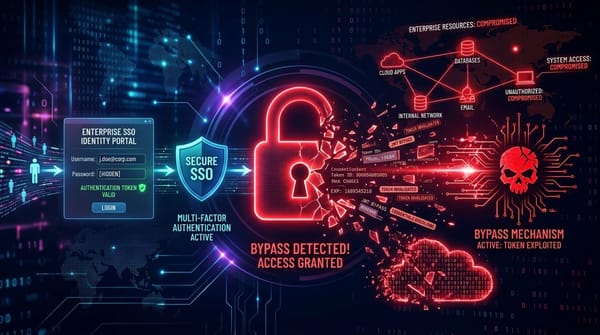
Technical breakdown of CVE-2026-18963, a CVSS 9.1 authentication bypass in Keycloak allowing unauthenticated account takeover via forced password reset.
en
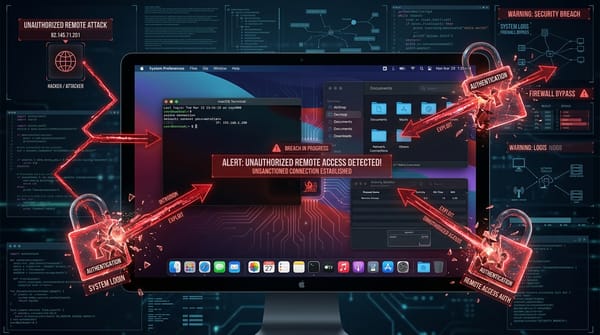
How attackers exploit CVE-2026-65400 in macOS Screen Sharing to bypass authentication checks and establish unauthorized remote desktop control.
en
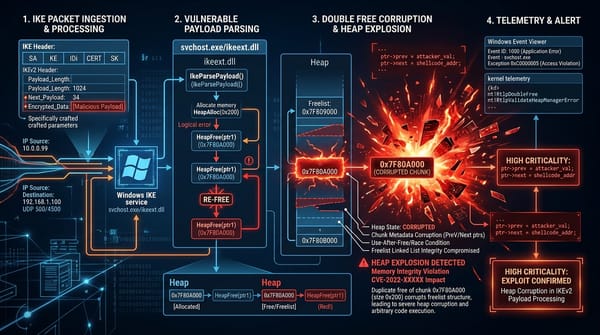
Technical root-cause analysis of CVE-2026-33824, a CVSS 9.8 double-free vulnerability in the Windows IKE service enabling unauthenticated remote code execution.
en
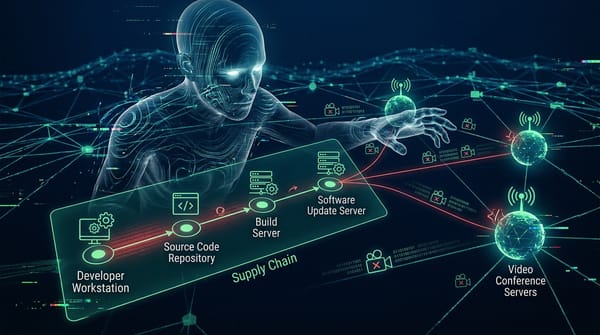
Deep dive into CVE-2026-72529 and CVE-2026-72530 in TrueConf Server, exploited by Head Mare for SYSTEM takeover and supply chain poisoning.