
Windows Defender ShieldBreak Zero-Day (CVE-2026-69414): Threat Update & Interim Defense
Threat briefing on the unpatched Windows Defender ShieldBreak zero-day (CVE-2026-69414) allowing local privilege escalation to SYSTEM.

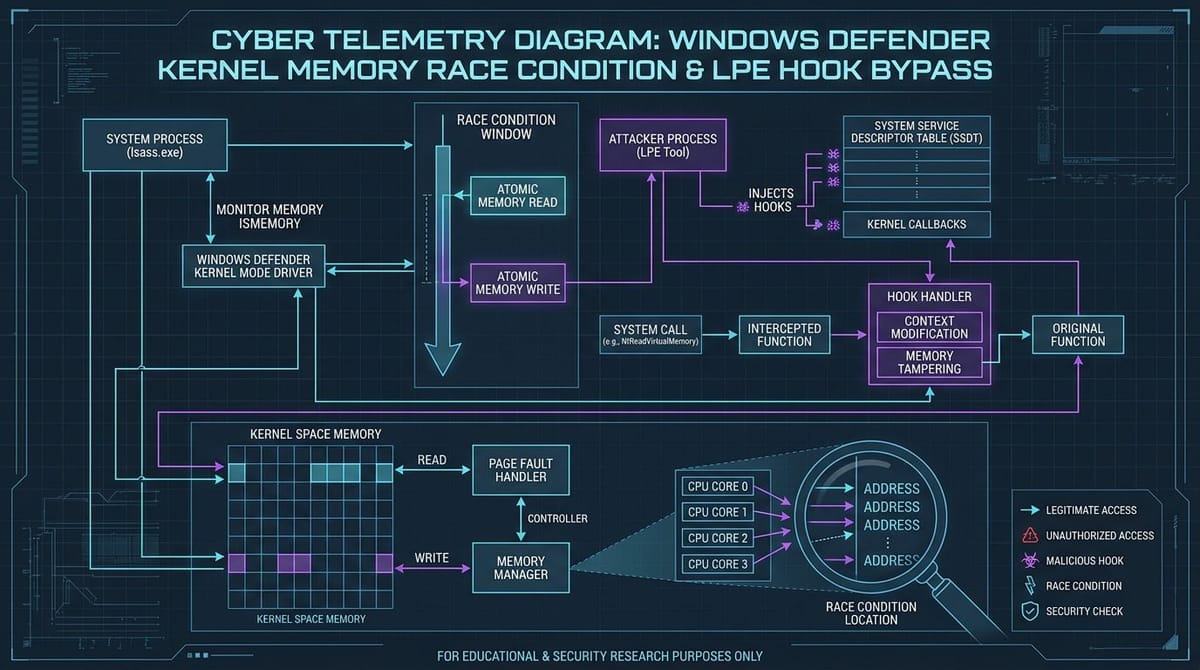
The zero-day elevation-of-privilege vulnerability in Microsoft Defender (ShieldBreak, CVE-2026-69414) continues to face active research and weaponization as security teams await official engine definition updates.
CVE-2026-69414 (CWE-362: Race Condition / CWE-59: Link Following)
Severity: High (CVSS 7.8 (Local Privilege Escalation to SYSTEM))
Status: ⚠️ Zero-Day / Public PoC Available / Patch in Progress
Affected Systems: Microsoft Defender Antivirus / Malware Protection Engine (MpEngine.dll)
Fixed In: Pending Microsoft Security Engine Definition Rollout
Technical Update on Race Condition Exploit
ShieldBreak builds upon race-condition techniques in Defender's file quarantine quarantine mechanism. When an unprivileged local user writes a signature-triggering file into a temporary directory, the Defender service (MsMpEng.exe) handles quarantine staging with full NT AUTHORITY\SYSTEM privileges.
By coordinating filesystem opportunistic locks (OpLocks) with rapid directory junction swapping, attackers trick the privileged service into redirecting file writes into C:\Windows\System32, overwriting legitimate DLLs to achieve full system takeover.
Interim Mitigations & Threat Hunting
%TEMP% and C:\ProgramData\.
Restrict unprivileged write permissions in shared local staging folders.
Remediation Checklist
System32 originating from MsMpEng.exe.

