
CVE-2026-21962: Oracle WebLogic Proxy Plug-in & HTTP Server Improper Access Control — CISA 72-Hour Federal Directive Breakdown
Deep dive into CVE-2026-21962: how threat actors bypass Oracle WebLogic reverse proxy security boundaries, and why CISA mandated an emergency 72-hour patch deadline.

📌
Security Roundup Series: Week of August 28, 2026 • 5 min read deep dive
A critical CVSS 9.8 improper access control vulnerability in Oracle HTTP Server and the Oracle WebLogic Server Proxy Plug-in is under active exploitation, prompting CISA to issue an emergency 72-hour federal remediation deadline under BOD 26-04.
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-21962 (CWE-284: Improper Access Control)
Severity: Critical (CVSS 9.8)
Status: 🚨 CISA KEV Catalog / 72-Hour Emergency Federal Mandate
Affected Systems: Oracle HTTP Server 12.2.1.4.0, WebLogic Server Proxy Plug-in 12.2.1.4.0
Vulnerability Mechanics & Proxy Bypass Flow
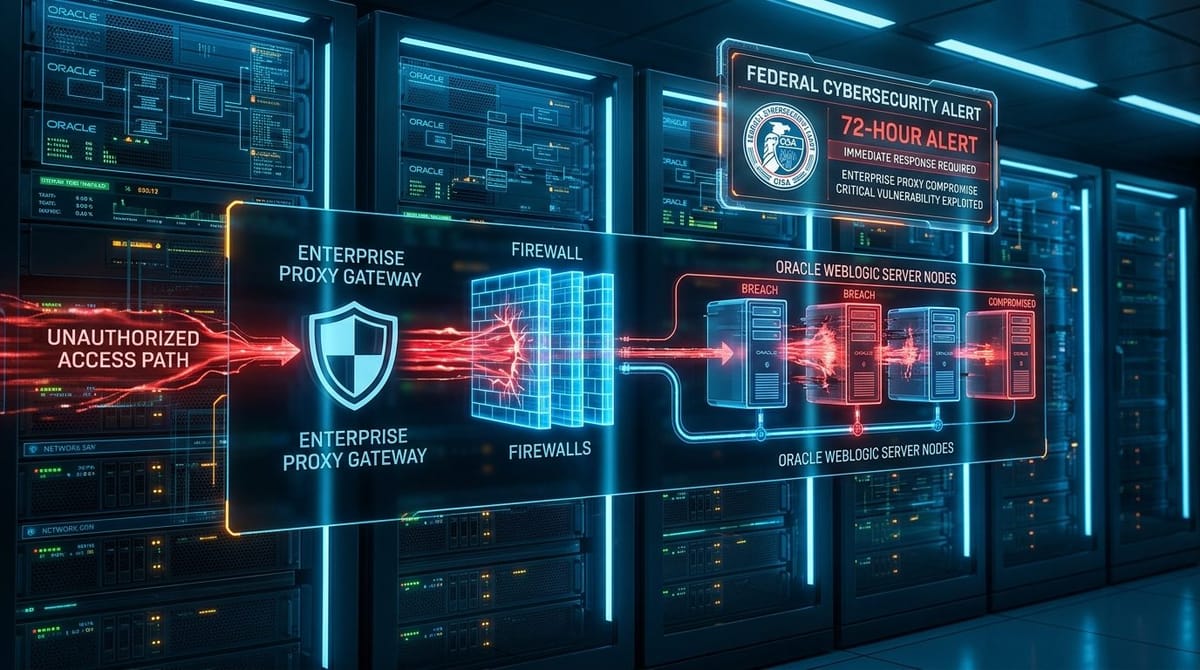
The flaw exists within the request routing parser of the WebLogic Server Proxy Plug-in (mod_wl_ohs). By manipulating specific HTTP request header delimiters, remote unauthenticated attackers bypass reverse proxy security boundaries and forward unauthorized administrative requests directly into backend WebLogic clusters.
Attack Chain Breakdown
- Header Normalization Discrepancy: Attackers craft HTTP requests with non-standard header spacing and URI encodings that the frontend Oracle HTTP Server accepts as benign static requests.
- Backend Routing Hijack: The proxy plug-in misinterprets the path delimiters, forwarding the payload to restricted backend WebLogic administrative endpoints (
/console,/management). - Remote Cluster Takeover: Attackers execute deployment APIs to stage malicious WAR packages or execute arbitrary server-side code without valid credentials.
Remediation Checklist
- Deploy Oracle Security Patches: Apply the latest Oracle Critical Patch Update advisory for Oracle HTTP Server and WebLogic Proxy components.
- Review Reverse Proxy Header Sanitization: Ensure all frontend WAFs and edge load balancers normalize incoming HTTP request paths before forwarding.
🧭
More Deep Dives from this Roundup:
PaperCut NG/MF Critical Pre-Auth RCE Zero-Day Analysis
CVE-2026-21962: Oracle WebLogic Proxy Plug-in Access Control Bypass
CVE-2026-8452: Citrix NetScaler ADC & Gateway Memory Failure
Halliburton & Microchip Technology Cyberattacks & Extortion Surge
Windows Kernel AFD.sys Zero-Day (CVE-2026-68820) Lazarus Deep Dive
← Return to Weekly Overview: Full Roundup

