
TrueConf Server RCE: How Threat Actor 'Head Mare' Deploys PhantomCore and Poisons Client Installers
Deep dive into CVE-2026-72529 and CVE-2026-72530 in TrueConf Server, exploited by Head Mare for SYSTEM takeover and supply chain poisoning.

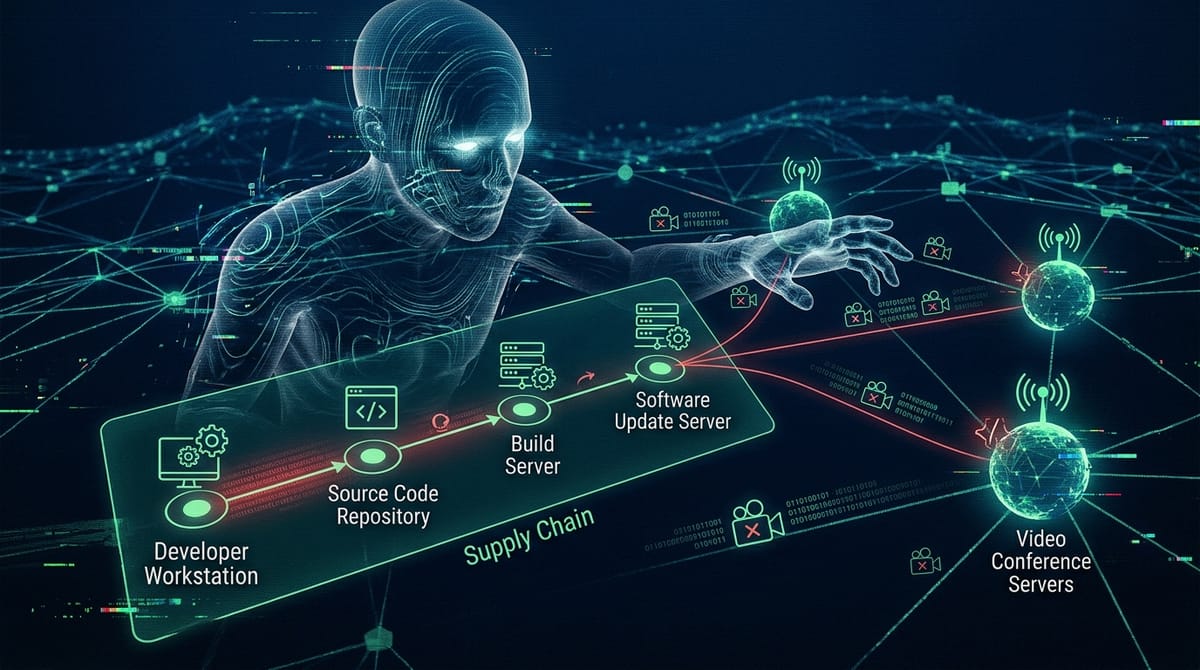
Threat actor group 'Head Mare' is actively weaponizing critical vulnerabilities in TrueConf Server, chaining missing authentication and code injection to hijack video conferencing infrastructure and poison software update installers.
CVE-2026-72529 & CVE-2026-72530 (CWE-306 (Missing Authentication) & CWE-94 (Code Injection))
Severity: Critical (CVSS 9.8)
Threat Actor: Head Mare Espionage & Extortion Syndicate
Status: ⚠️ CISA KEV Catalog Added (Active Supply Chain Poisoning)
Affected Systems: TrueConf Server versions prior to 5.3.9, 5.4.9, and 5.5.5
Fixed In: TrueConf Server 5.3.9, 5.4.9, 5.5.5
Attack Chain & Supply Chain Poisoning
TrueConf Server listens on TCP port 4307 for inter-service communication and management commands. Due to missing access controls (CVE-2026-72529), unauthenticated remote attackers can issue administrative API calls directly, pairing them with code injection flaws (CVE-2026-72530) to execute arbitrary commands under SYSTEM authority.
In observed campaigns, Head Mare operators deployed custom backdoors known as PhantomCore and PhantomGraph. Alarmingly, attackers modified server-hosted client installer packages, serving trojanized update binaries to downstream enterprise users connecting to the conference server.
Forensic Indicators & Detection
PhantomCore DLL loaders.

