
CVE-2026-66149 & CVE-2026-66150: SonicWall Email Security Appliance Code Injection & Root Execution
Analysis of CVE-2026-66149 and CVE-2026-66150 in SonicWall Email Security: CLI breakout mechanics, root privilege escalation, and patch details.

📌
Security Roundup Series: Weekend Edition • August 31, 2026 • 4 min read deep dive
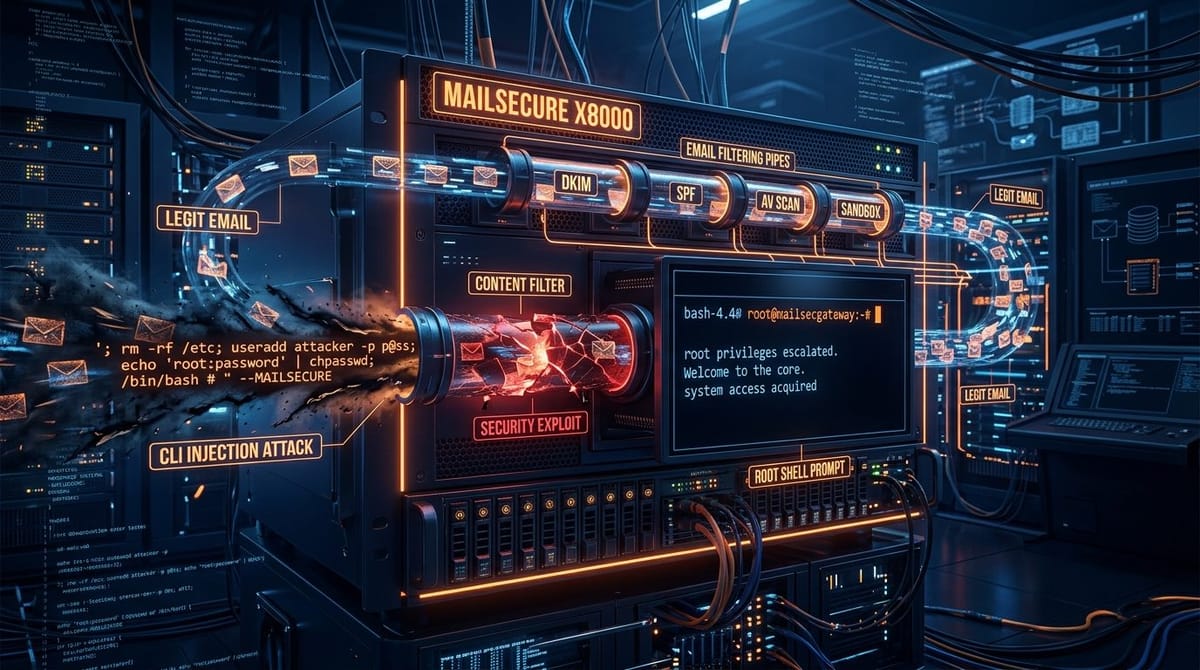
SonicWall has patched two high-severity code injection vulnerabilities in its Email Security appliances (CVE-2026-66149 and CVE-2026-66150) that allow authenticated attackers with restricted CLI privileges to escalate to root shell access.
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-66149 / CVE-2026-66150 (CWE-94: Improper Control of Generation of Code)
Severity: High (CVSS 7.8)
Status: 🚨 Security Advisory Patched in Version 10.0.36
Affected Systems: SonicWall Email Security versions prior to 10.0.36
Vulnerability Breakdown
The flaws exist in the appliance CLI command parser. Restricted administrative users can supply unsanitized arguments to diagnostic utility commands, breaking out of the restricted shell into a full bash environment with root permissions.
🧭
More Deep Dives from this Roundup:
CVE-2026-59285: Spring for GraphQL Critical RCE Analysis
SonicWall SMA 1000 Chained SSRF & Root RCE by UTA0533
CVE-2026-59270: Spring Security LDAP Directory Authentication Bypass
SonicWall Email Security Appliance Code Injection & Root Execution
RansomHub Healthcare Extortion Wave & Dual-Ransom Tactics
← Return to Weekly Overview: Full Roundup

