
Guía de Defensa para CISOs del 16 de Noviembre de 2026: Blindaje de Gaia OS, N-central, Outlook/CLFS, Apache 2.4.71, SAP 10.0 y Pipelines de IA/CI

📌
Security Roundup Series: Fin de Semana del 16 de Noviembre de 2026 • 9 min de lectura deep dive
Para ayudar a los Centros de Operaciones de Seguridad (SOC), proveedores MSP y equipos de infraestructura a operacionalizar cada revelación del Resumen de Seguridad del 16 de Noviembre de 2026, esta guía consolida los comandos de blindaje, reglas de firewall/WAF, parámetros SAP y auditorías de CI/CD listos para producción.
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-123039, CVE-2026-114713, CVE-2026-90436, CVE-2026-124194, CVE-2026-119618, CVE-2026-89103 y CVE-2026-126261 (Blindaje en Profundidad, Parcheo Virtual, Aislamiento de Sockets y Rotación de Secretos)
Severity: PLAYBOOK OBLIGATORIO DE REMEDIACIÓN PARA EL LUNES (CVSS 9.8 – 10.0 en Gateways Perimetrales, RMMs, Servidores Web, Sistemas ERP y Pipelines de Desarrollo)
Status: Acción Inmediata Requerida en Entornos Empresariales
Affected Systems: Check Point Gaia OS, UnrealIRCd, N-able N-central, Microsoft Outlook/Exchange/LDAP/CLFS, Apache httpd, Chrome, Node.js, SAP, Fortinet, Cursor y GitHub Actions
Fixed In: Actualizaciones de Fabricantes y Controles Compensatorios Detallados Abajo
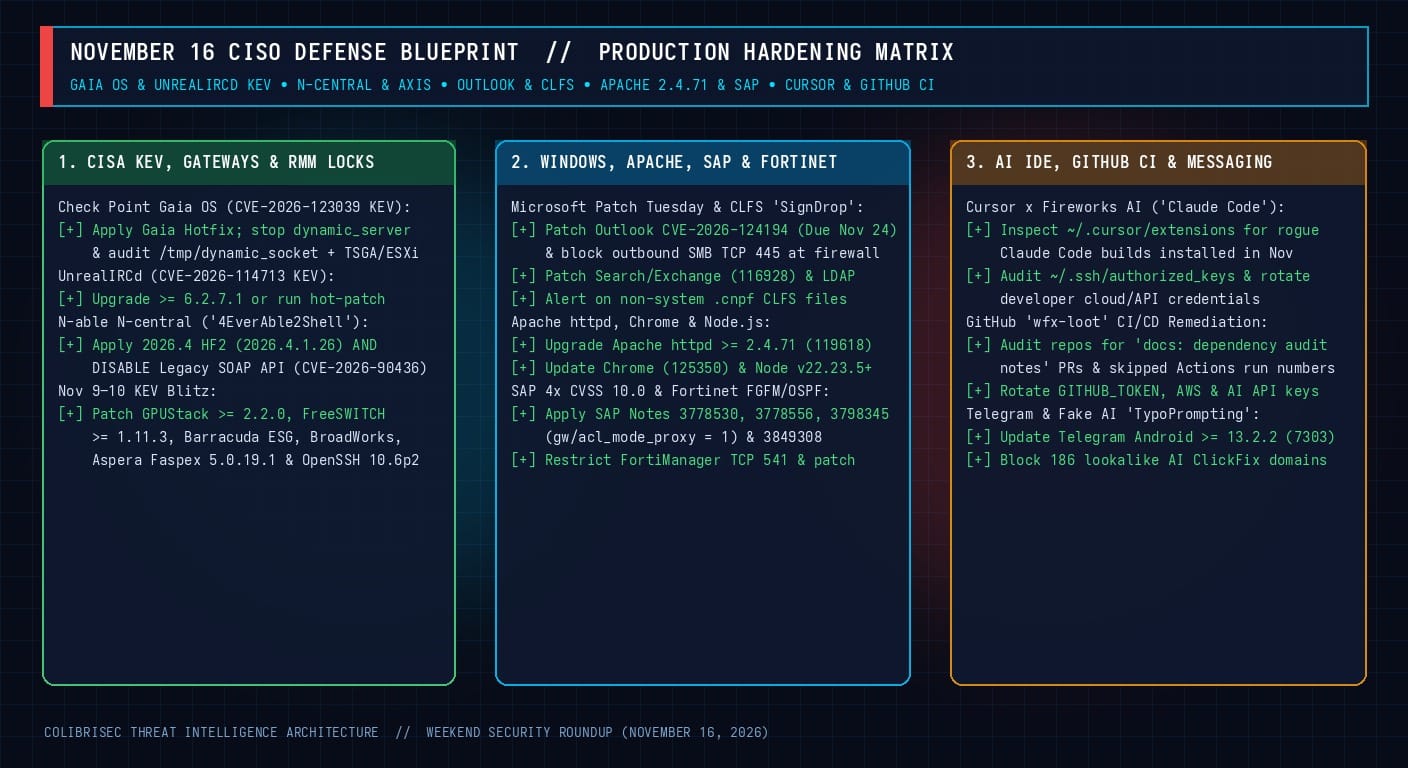
Nivel 1: Check Point Gaia OS (CVE-2026-123039), UnrealIRCd (CVE-2026-114713) y N-central (CVE-2026-90436)
# 1. Check Point Gaia OS (CVE-2026-123039 - CISA KEV):
tellpm process:dynamic_server
killall -9 dynamic_server 2>/dev/null
rm -f /tmp/dynamic_socket
find / -name "*TSGA*" -o -name "*TSProxy*" -o -name "*destroy_v6*" -o -name "DREAM_ANNEXATION.txt" 2>/dev/null

# 2. UnrealIRCd (CVE-2026-114713 - CISA KEV):
./unrealircd hot-patch bundle-20261107

# 3. N-able N-central "4EverAble2Shell" (CVE-2026-90436):
# Actualizar a 2026.4 Hotfix 2 (2026.4.1.26) y DESHABILITAR la Legacy SOAP API
Nivel 2: Microsoft Patch Tuesday (CVE-2026-124194), CLFS "SignDrop", Apache 2.4.71, SAP 10.0 y GitHub CI
# 1. Bloquear SMB saliente (TCP 445/139) y deshabilitar WebClient contra CVE-2026-124194 en Outlook
New-NetFirewallRule -DisplayName "ColibriSec-Block-Outbound-SMB" -Direction Outbound -Protocol TCP -RemotePort 445,139 -Action Block
Stop-Service -Name "WebClient" -Force
Set-Service -Name "WebClient" -StartupType Disabled

# 2. En SAP Gateway (CVE-2026-89103 - Nota 3798345), definir en DEFAULT.PFL:
# gw/acl_mode_proxy = 1
# En Apache HTTP Server actualizar a >= 2.4.71 (CVE-2026-119618) y en Node.js a >= v22.23.5 / v24.22.3 / v26.13.1
🧭
More Deep Dives from this Roundup:
CISA KEV y Wipers en Hipervisores: LPE en Check Point Gaia (CVE-2026-123039) hacia ESXi, UnrealIRCd (CVE-2026-114713), GPUStack y FreeSWITCH
Crisis Zero-Day en RMM: 33 Fallos "Able2Shell" en N-able N-central, RCE Root "4EverAble2Shell" vía Apache Axis (CVE-2026-90436) y "Agent2Shell"
Patch Tuesday de Microsoft (1,235 CVEs) y Zero-Days: Fuga NTLMv2 en Outlook (CVE-2026-124194), RCEs en Search/LDAP y "SignDrop" en Windows CLFS
Servidores Web, Navegadores y Runtimes: RCE en Apache mod_http2 (CVE-2026-119618), Zero-Day XML en Chrome (CVE-2026-125350) y Fuga TLS en Node.js
Megaparches ERP y Firewalls: 4x CVSS 10.0 en SAP ("ICM2SHELL" y "PROXYGATE"), Fortinet FGFM/OSPF (CVE-2026-126261) y Adobe Connect/AEM
Ataques a la Cadena de Suministro de IA y CI/CD: Extensión "Claude Code" Troyanizada en Cursor x Fireworks AI y "wfx-loot" en 61,000+ Repos de GitHub
Escape de Sandbox en Mensajería y Señuelos de IA: RCE en Widgets QuickJS de Telegram ("WebRAT") y 186 Dominios Falsos "TypoPrompting"
Operación Endgame Incauta 235 Servidores, Brecha de 37.62M en Nitori, Maersk 100GB y la Verdad tras las Caídas de la FAA y Microsoft 365
← Return to Weekly Overview: Full Roundup

