
CVE-2026-85706: GitLab Maximum-Severity CVSS 10.0 Arbitrary File Read Vulnerability Added to CISA KEV
Technical breakdown of CVE-2026-85706 in GitLab: CVSS 10.0 unauthenticated path traversal, source code exfiltration, and CISA KEV emergency guidance.

📌
Security Roundup Series: Weekend Edition • September 14, 2026 • 6 min read deep dive
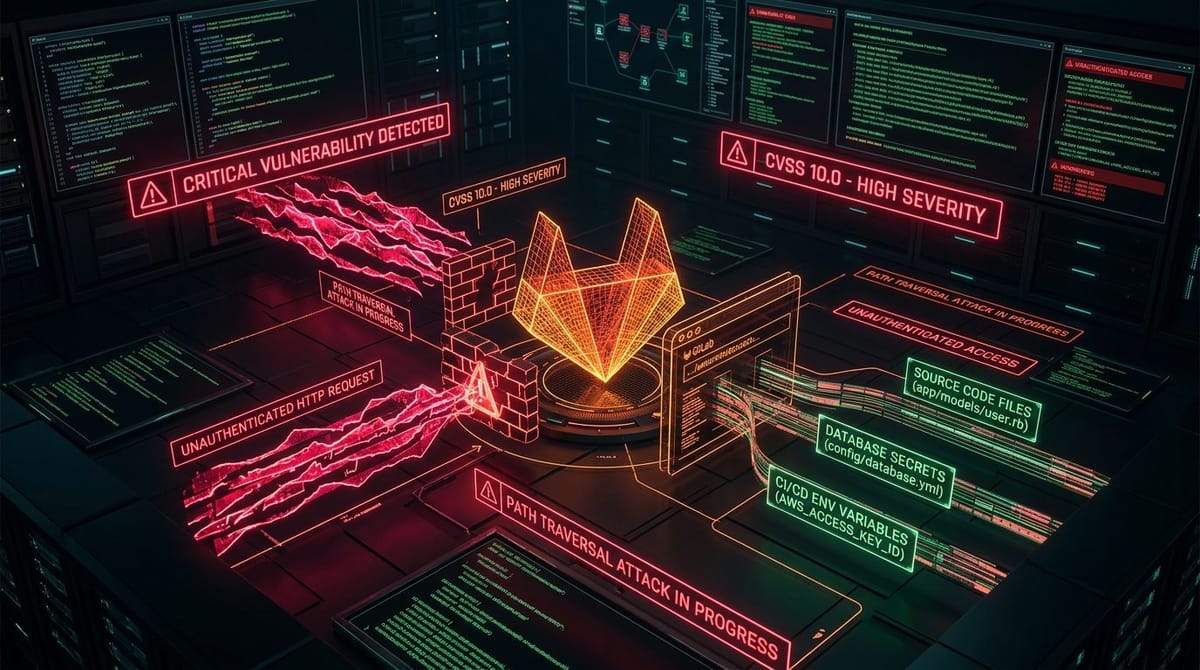
A maximum-severity CVSS 10.0 path traversal vulnerability in self-managed GitLab Community and Enterprise editions (CVE-2026-85706) has been cataloged in CISA KEV following active exploitation to steal source code repositories, database secrets, and CI/CD signing keys.
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-85706 (CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal'))
Severity: Critical / Maximum Severity (CVSS 10.0)
Status: 🚨 Added to CISA KEV Catalog / Active Remote Exploitation
Affected Systems: GitLab CE/EE versions 19.1.x before 19.1.8, 19.2.x before 19.2.6, 19.3.x before 19.3.2
Vulnerability Mechanics & Secret Exfiltration
The flaw exists within GitLab's package registry file endpoint. By submitting crafted HTTP requests with URL-encoded directory traversal sequences, unauthenticated remote attackers can read arbitrary files accessible to the GitLab system user, including config/database.yml, CI/CD environment secrets, and private SSH keys.
🧭
More Deep Dives from this Roundup:
CVE-2026-85706: GitLab CVSS 10.0 Arbitrary File Read in CISA KEV
CVE-2026-75650: Adobe Commerce & Magento Critical RCE (APSB26-146)
CVE-2025-25249: Fortinet FortiOS & FortiSASE Heap Overflow Exploited
APSB26-141: Adobe Acrobat & Reader Code Execution Wave
SecOps Advisory: Securing Git Repositories and E-Commerce Gateways
← Return to Weekly Overview: Full Roundup

