
APSB26-141: Adobe Acrobat & Reader Multi-Vulnerability Wave — Arbitrary Code Execution & Memory Corruption
Analysis of security bulletin APSB26-141 in Adobe Acrobat and Reader: memory buffer corruption, weaponized PDF handling, and endpoint protection.

📌
Security Roundup Series: Weekend Edition • September 14, 2026 • 4 min read deep dive
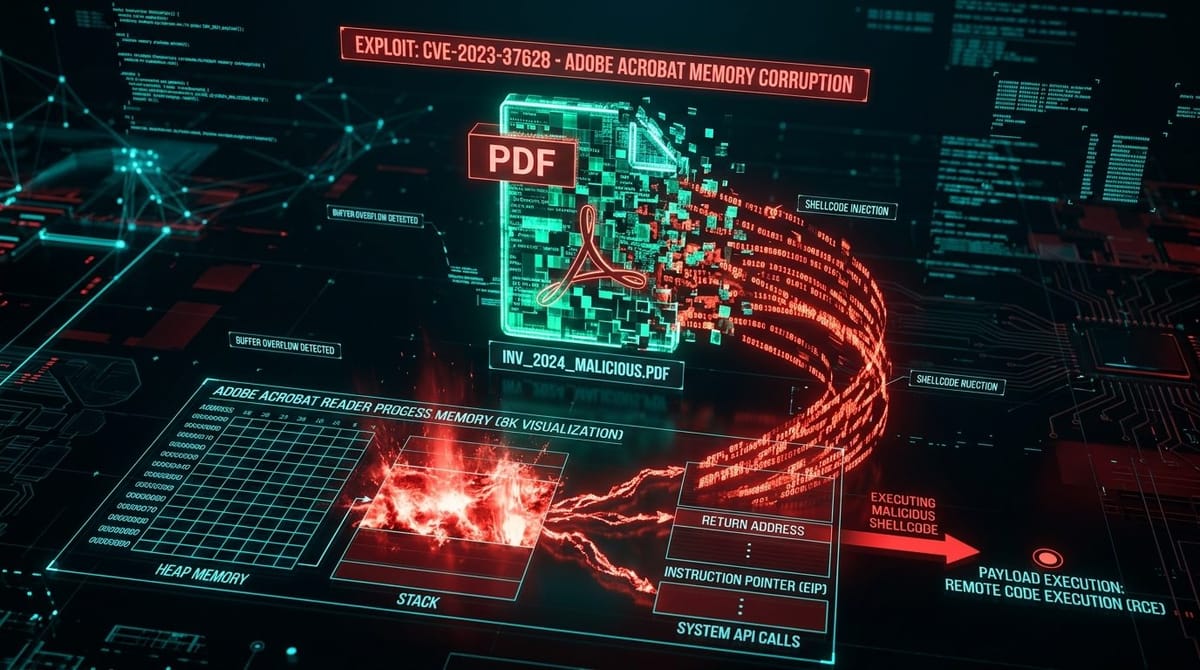
Adobe's monthly security release for Acrobat and Reader (APSB26-141) addresses multiple critical memory corruption vulnerabilities, including CVE-2026-81996, enabling arbitrary code execution through weaponized PDF attachments.
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-81996 & APSB26-141 Wave (CWE-119: Improper Restriction of Operations within the Bounds of a Memory Buffer)
Severity: Critical (CVSS 8.8)
Status: 🚨 Critical PDF Document Exploit Wave / High Priority
Affected Systems: Adobe Acrobat DC, Acrobat Reader DC on Windows and macOS
Memory Buffer Corruption Mechanics
Vulnerabilities in the PDF rendering engine allow malformed font stream tables and embedded JavaScript objects to overflow internal buffers, executing arbitrary native shellcode in the context of the current desktop user.
🧭
More Deep Dives from this Roundup:
CVE-2026-85706: GitLab CVSS 10.0 Arbitrary File Read in CISA KEV
CVE-2026-75650: Adobe Commerce & Magento Critical RCE (APSB26-146)
CVE-2025-25249: Fortinet FortiOS & FortiSASE Heap Overflow Exploited
APSB26-141: Adobe Acrobat & Reader Code Execution Wave
SecOps Advisory: Securing Git Repositories and E-Commerce Gateways
← Return to Weekly Overview: Full Roundup

