
CVE-2025-25249: FortiOS, FortiSwitchManager & FortiSASE Heap Buffer Overflow Under Active Exploitation
Technical teardown of CVE-2025-25249 in Fortinet FortiOS: heap buffer overflow in SSL VPN daemons, implant deployment, and CISA KEV directive.

📌
Security Roundup Series: Weekend Edition • September 14, 2026 • 5 min read deep dive
A heap-based buffer overflow vulnerability affecting FortiOS, FortiSwitchManager, and FortiSASE (CVE-2025-25249) has been added to CISA KEV following active perimeter exploitation targeting enterprise SSL VPN tunnels.
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2025-25249 (CWE-122: Heap-based Buffer Overflow)
Severity: Critical (CVSS 9.8)
Status: 🚨 Active In-the-Wild Exploitation / Added to CISA KEV
Affected Systems: FortiOS 7.4.0 through 7.4.4, FortiOS 7.2.0 through 7.2.8, FortiSASE releases
Memory Corruption in SSL VPN Daemon
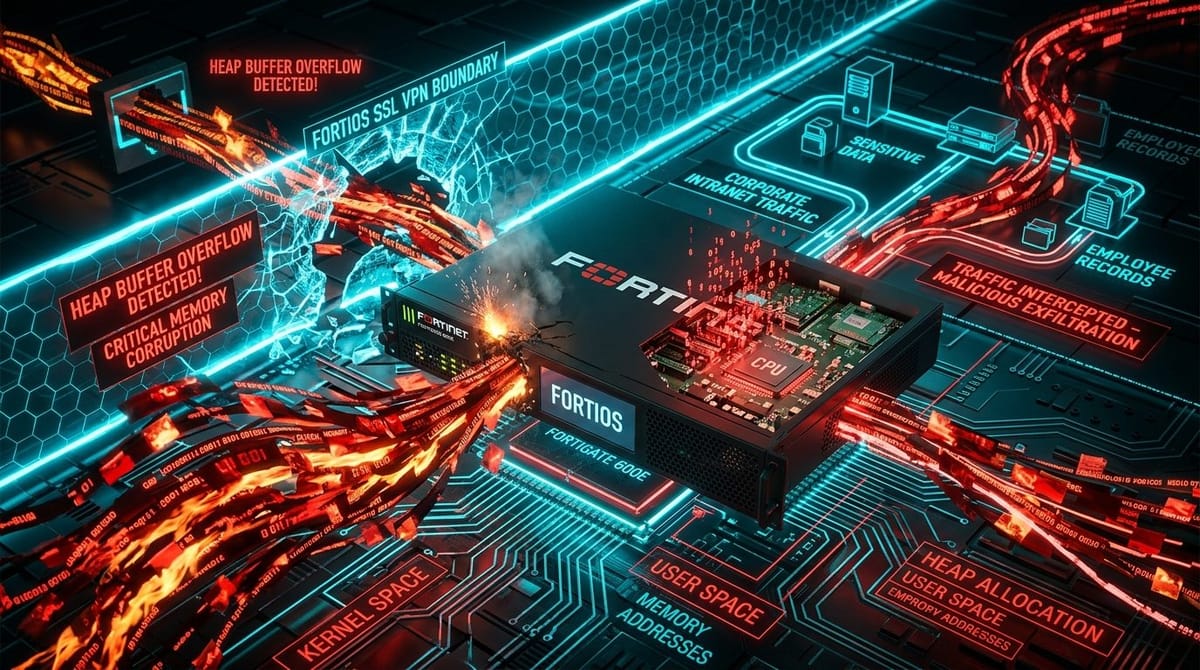
Crafted SSL VPN handshakes corrupt heap memory structures inside the sslvpnd process, allowing attackers to overwrite execution control registers and deploy persistent implants on the firewall.
🧭
More Deep Dives from this Roundup:
CVE-2026-85706: GitLab CVSS 10.0 Arbitrary File Read in CISA KEV
CVE-2026-75650: Adobe Commerce & Magento Critical RCE (APSB26-146)
CVE-2025-25249: Fortinet FortiOS & FortiSASE Heap Overflow Exploited
APSB26-141: Adobe Acrobat & Reader Code Execution Wave
SecOps Advisory: Securing Git Repositories and E-Commerce Gateways
← Return to Weekly Overview: Full Roundup

