
CVE-2026-85046: Google Chrome V8 Engine Type Confusion Zero-Day Under Active In-the-Wild Exploitation
Technical teardown of CVE-2026-85046 in Google Chrome V8: JIT compiler type confusion, memory corruption primitives, and in-the-wild exploitation mechanics.

📌
Security Roundup Series: Week of September 4, 2026 • 5 min read deep dive
Google has issued an emergency security update addressing an actively exploited type confusion zero-day vulnerability in the Chromium V8 JavaScript engine (CVE-2026-85046), marking the browser's sixth exploited zero-day of 2026.
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-85046 (CWE-843: Access of Resource Using Incompatible Type (Type Confusion))
Severity: High / Actively Exploited (CVSS 8.8)
Status: 🚨 In-the-Wild Zero-Day Exploitation / Emergency Chrome Update
Affected Systems: Google Chrome versions prior to 128.0.6613.119/.120
Vulnerability Mechanics in the V8 JIT Compiler
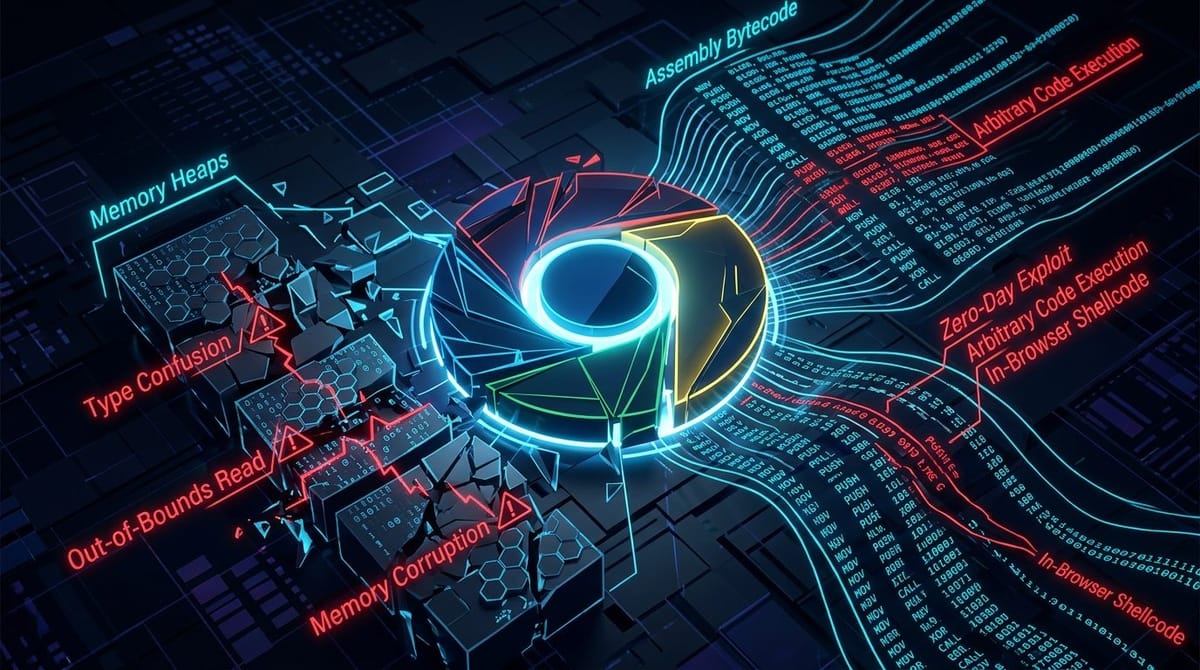
The vulnerability exists within the Maglev/Turbofan Just-In-Time (JIT) optimization compiler. By passing specialized array buffer objects through speculative type optimizations, an attacker forces the engine to miscalculate memory offsets, resulting in out-of-bounds read and write capabilities within the browser sandbox.
Exploit Chain & Sandbox Escape
- Heap Layout Manipulation: Malicious JavaScript constructs an array with mixed fast-element and dictionary types, confusing the optimizer during loop unrolling.
- Arbitrary Read/Write Primitive: The type confusion enables memory read/write across the V8 isolate memory space.
- Renderer Compromise: Attackers execute arbitrary native code inside the sandboxed renderer process before pivoting to OS-level escalation primitives.
Remediation Checklist
- Update All Browsers: Ensure Google Chrome is updated to version 128.0.6613.119/.120 or newer on Windows, macOS, and Linux.
- Enable Isolated Web Apps & Site Isolation: Verify that strict per-origin process isolation is enforced across corporate endpoints.
🧭
More Deep Dives from this Roundup:
CVE-2026-85046: Chrome V8 Type Confusion Zero-Day Analysis
CrowdStrike FalconFlank Zero-Day & EDR Sensor Tampering
CVE-2026-59822: LiteLLM AI Proxy Improper Authentication in CISA KEV
CVE-2026-82329: JFrog Artifactory Supply Chain Repository Hijack
CVE-2026-48710: Kludex Starlette HTTP Request & Response Smuggling
← Return to Weekly Overview: Full Roundup


