
CVE-2026-48710: Kludex Starlette HTTP Request & Response Smuggling Flaw Weaponized Against Python Web Gateways
Technical analysis of CVE-2026-48710 in Kludex Starlette: HTTP desynchronization mechanics, FastAPI backend impact, and CISA KEV guidance.

📌
Security Roundup Series: Week of September 4, 2026 • 4 min read deep dive
An HTTP request and response smuggling vulnerability in the Kludex Starlette ASGI framework (CVE-2026-48710), widely used under FastAPI and Python web applications, has been cataloged in CISA KEV due to active perimeter exploitation.
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-48710 (CWE-444: Inconsistent Interpretation of HTTP Requests (HTTP Request/Response Smuggling))
Severity: High (CVSS 8.6)
Status: 🚨 Added to CISA KEV Catalog / Active Exploitation
Affected Systems: Starlette versions prior to 0.38.0
Desynchronization Mechanics
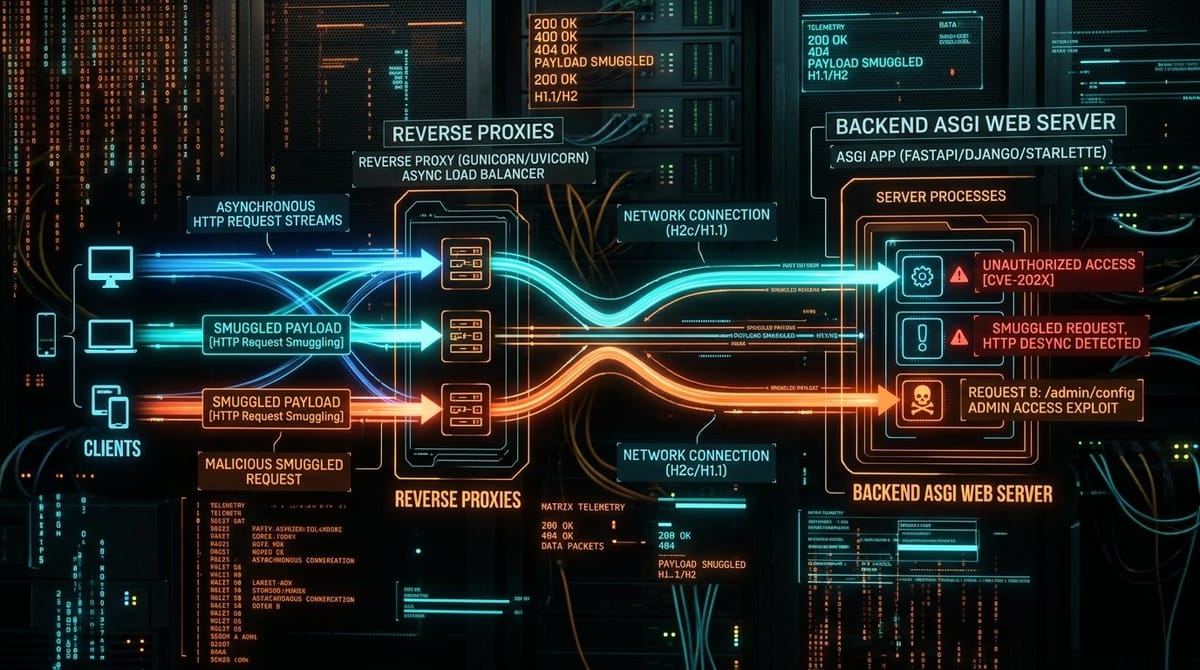
Differences in how frontend reverse proxies (Nginx, HAProxy) and Starlette parse malformed Transfer-Encoding and Content-Length headers allow threat actors to prepend unauthorized HTTP requests onto subsequent client connections, leading to session hijacking and cache poisoning.
🧭
More Deep Dives from this Roundup:
CVE-2026-85046: Chrome V8 Type Confusion Zero-Day Analysis
CrowdStrike FalconFlank Zero-Day & EDR Sensor Tampering
CVE-2026-59822: LiteLLM AI Proxy Improper Authentication in CISA KEV
CVE-2026-82329: JFrog Artifactory Supply Chain Repository Hijack
CVE-2026-48710: Kludex Starlette HTTP Request & Response Smuggling
← Return to Weekly Overview: Full Roundup

