
CVE-2026-59822: BerriAI LiteLLM Improper Authentication — CISA KEV Addition & LLM Proxy Compromise
Technical teardown of CVE-2026-59822 in BerriAI LiteLLM: authentication bypass in enterprise AI proxies, LLM key exfiltration, and CISA KEV implications.

📌
Security Roundup Series: Week of September 4, 2026 • 5 min read deep dive
CISA has added an improper authentication vulnerability in BerriAI LiteLLM (CVE-2026-59822) to its Known Exploited Vulnerabilities catalog, marking a critical milestone in nation-state and cybercrime targeting of enterprise AI proxy and LLM gateway infrastructure.
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-59822 (CWE-287: Improper Authentication)
Severity: Critical (CVSS 9.8)
Status: 🚨 Added to CISA KEV Catalog / Active AI Gateway Exploitation
Affected Systems: BerriAI LiteLLM proxy deployments prior to version 1.44.15
Threat Context: Weaponizing the AI Gateway
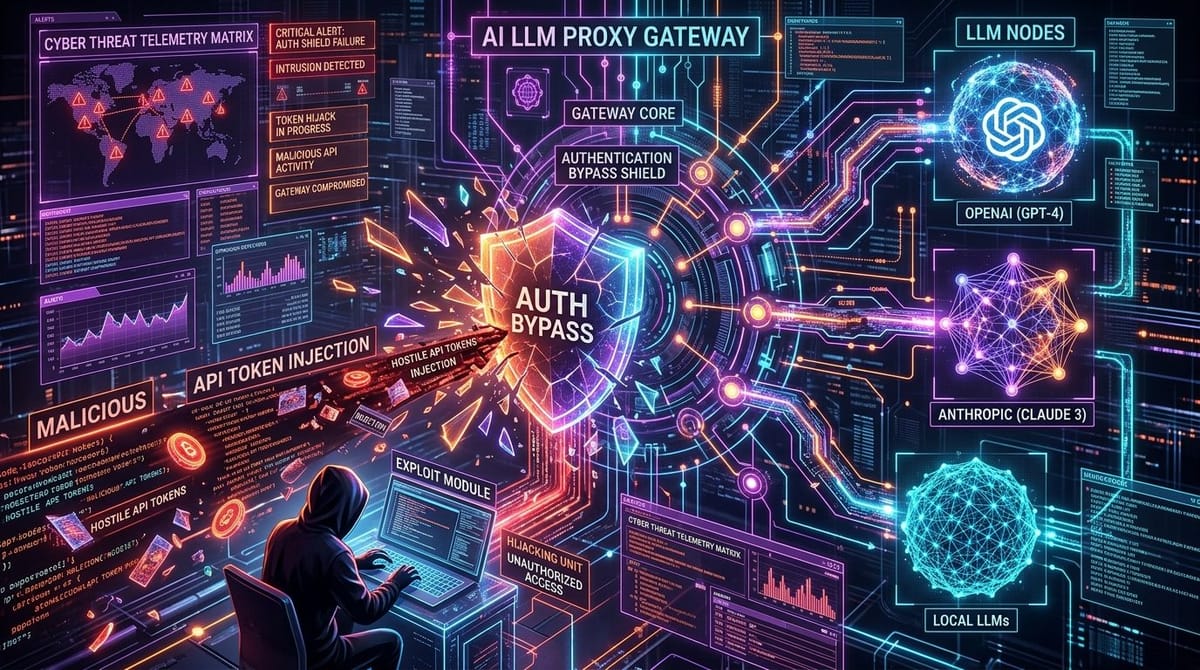
LiteLLM serves as an orchestration proxy forwarding developer prompts to upstream LLM providers (OpenAI, Anthropic, AWS Bedrock). An authentication bypass in the LiteLLM admin dashboard API allows unauthenticated remote actors to query internal model endpoints, exfiltrate API keys, and poison conversational context memory.
🧭
More Deep Dives from this Roundup:
CVE-2026-85046: Chrome V8 Type Confusion Zero-Day Analysis
CrowdStrike FalconFlank Zero-Day & EDR Sensor Tampering
CVE-2026-59822: LiteLLM AI Proxy Improper Authentication in CISA KEV
CVE-2026-82329: JFrog Artifactory Supply Chain Repository Hijack
CVE-2026-48710: Kludex Starlette HTTP Request & Response Smuggling
← Return to Weekly Overview: Full Roundup

