en

Bitget $387.5M Cryptocurrency Exchange Hot Wallet Breach

News

Bitget $387.5M Security Breach: Third-Party Zero-Day and Hot Wallet Risk Analysis

📌Security Roundup Series: Week of October 2, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Bitget Global Cryptocurrency Exchange Threat Actor / Attribution: Suspected State-Sponsored Syndicate (Lazarus Group / DPRK) Impact / Records Compromised: $387.5 Million in Digital Assets (ETH, XRP, USDT, USDC across 11 Blockchains) Initial Attack Vector: Zero-Day

By James Luther
ColibriSec Weekend Security Roundup September 28 2026

News

Security Roundup: Citrix NetScaler Active Zero-Days, Microsoft SharePoint KEV, Kiteworks Precautionary Shutdown (Weekend Edition - September 28, 2026)

Executive Summary: The weekend of September 26–28, 2026, unleashed one of the most critical sequences of edge appliance emergencies and AI-augmented cyber offensives of the year. Citrix released urgent out-of-band updates and CTX697096 advisories for two actively exploited zero-day Remote Code Execution (RCE) flaws in NetScaler ADC and Gateway

By James Luther
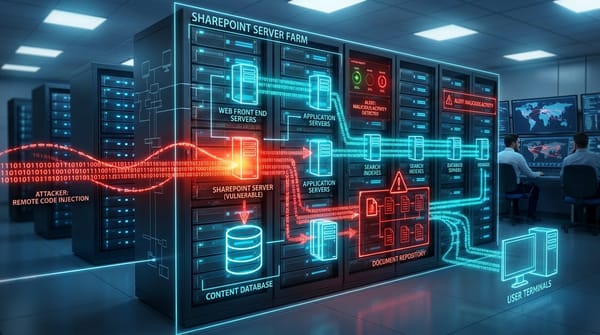
Microsoft SharePoint CVE-2026-65660 Technical Analysis

News

CVE-2026-65660: Microsoft SharePoint Server Code Injection RCE Added to CISA KEV Under Active Exploitation

📌Security Roundup Series: Weekend of September 28, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-65660 (CWE-94 / CWE-502) Severity: HIGH / CRITICAL (CVSS 8.8) Status: September 25, 2026 (Added to CISA KEV) Affected Systems: Microsoft SharePoint Server 2016, 2019, Subscription Edition Fixed In: Microsoft September 2026 Cumulative Update

By James Luther
Kiteworks Precautionary Emergency Shutdown Analysis

News

Inside the Kiteworks Emergency Shutdown: Anatomy of a Precautionary Zero-Day Defense Action

📌Security Roundup Series: Weekend of September 28, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Kiteworks Global Customer Base (Self-Managed Deployments) Threat Actor / Attribution: Credible Federal Threat Intelligence / Unnamed APT Syndicate Impact / Records Compromised: Zero Confirmed Breaches (Preemptive Defensive Action) Initial Attack Vector: Targeted Zero-Day Weaponization against "

By James Luther
Adif and Renfe Spanish Railway Cyberattack Deep Dive

News

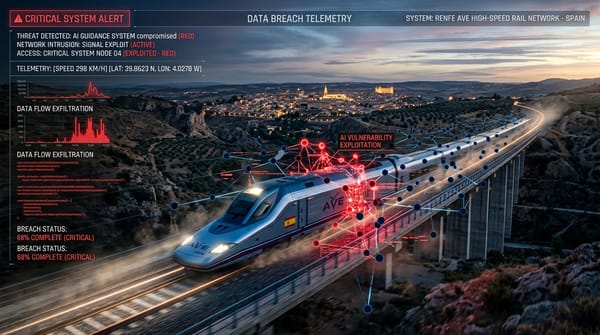
Adif & Renfe Railway Cyberattack: First Documented AI-Augmented Intrusion on Spanish Critical Infrastructure

📌Security Roundup Series: Weekend of September 28, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Adif (Infrastructure Manager) & Renfe (National Railway) - Spain Threat Actor / Attribution: Unattributed Cyber Threat Actor / AI-Assisted Reconnaissance Unit Impact / Records Compromised: ~500GB Exfiltrated (Passenger Telemetry, Route Scheduling, System Logs) Initial Attack Vector:

By James Luther
ShinyHunters Syndicate Amsterdam Arrest and Retaliation Analysis

News

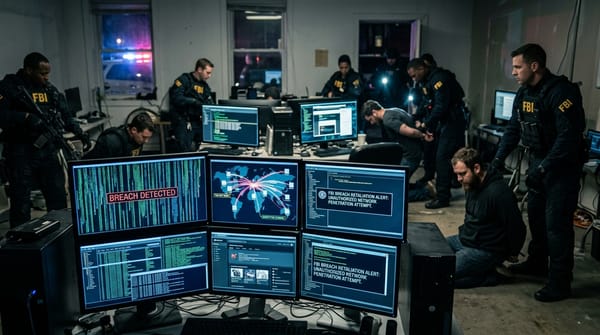
ShinyHunters Syndicate Retaliation: Amsterdam Arrest Sparks Extortion Surge and Federal Contractor Leaks

📌Security Roundup Series: Weekend of September 28, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: ShinyHunters Syndicate Infrastructure / Odido / FBI Job Portal Threat Actor / Attribution: Pepijn van der Stap (Arrested) & ShinyHunters Retaliatory Affiliates Impact / Records Compromised: Terabytes of Historical & Retaliatory Extortion Data Initial Attack Vector: Offensive

By James Luther
Qilin Ransomware AI Active Directory Destruction Analysis

News

Qilin Ransomware Tops 2026 Threat Landscape: AI-Generated Active Directory Kill-Chains and Industrial Extortion

📌Security Roundup Series: Weekend of September 28, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Global Industrial, Healthcare & Manufacturing Sectors Threat Actor / Attribution: Qilin Ransomware Syndicate (RaaS) Impact / Records Compromised: Record High: 15% of all August/September 2026 Global Ransomware Attacks Initial Attack Vector: AI-Generated Active Directory

By James Luther
Hardening Enterprise Perimeters Architecture Blueprint

guides

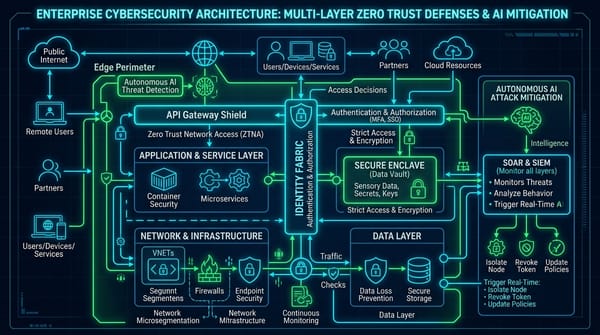
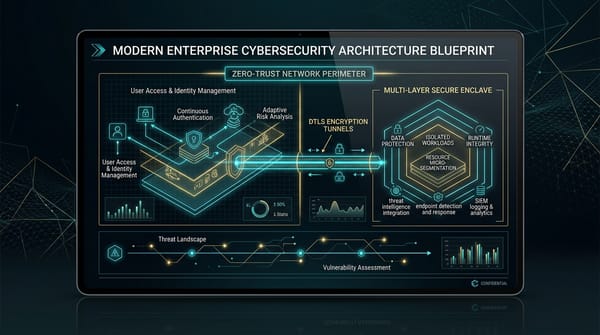
Hardening Enterprise Perimeters: NetScaler DTLS, SharePoint Farm Isolation, and AI-Resilient Architecture

📌Security Roundup Series: Weekend of September 28, 2026 • 4 min read deep dive The weekend disclosures of September 26–28, 2026—spanning dual zero-days in Citrix NetScaler, deserialization RCE in Microsoft SharePoint, and AI-accelerated intrusions—make it clear that perimeter edge devices and core identity systems are under unprecedented strain.

By James Luther
ColibriSec Weekly Security Roundup September 25 2026

News

Security Roundup: F5 BIG-IP APM Buffer Overflow, Check Point Management Zero-Day, Arista VeloCloud in CISA KEV (Week of September 25, 2026)

Executive Summary: The final week of September 2026 witnessed an unprecedented wave of critical edge infrastructure and enterprise appliance disclosures. CISA added three high-impact zero-days to the Known Exploited Vulnerabilities catalog: an unauthenticated heap-based buffer overflow in F5 BIG-IP Access Policy Manager (CVE-2026-94127, CVSS 9.8), an actively exploited path

By James Luther