
CVE-2026-65660: Microsoft SharePoint Server Code Injection RCE Added to CISA KEV Under Active Exploitation

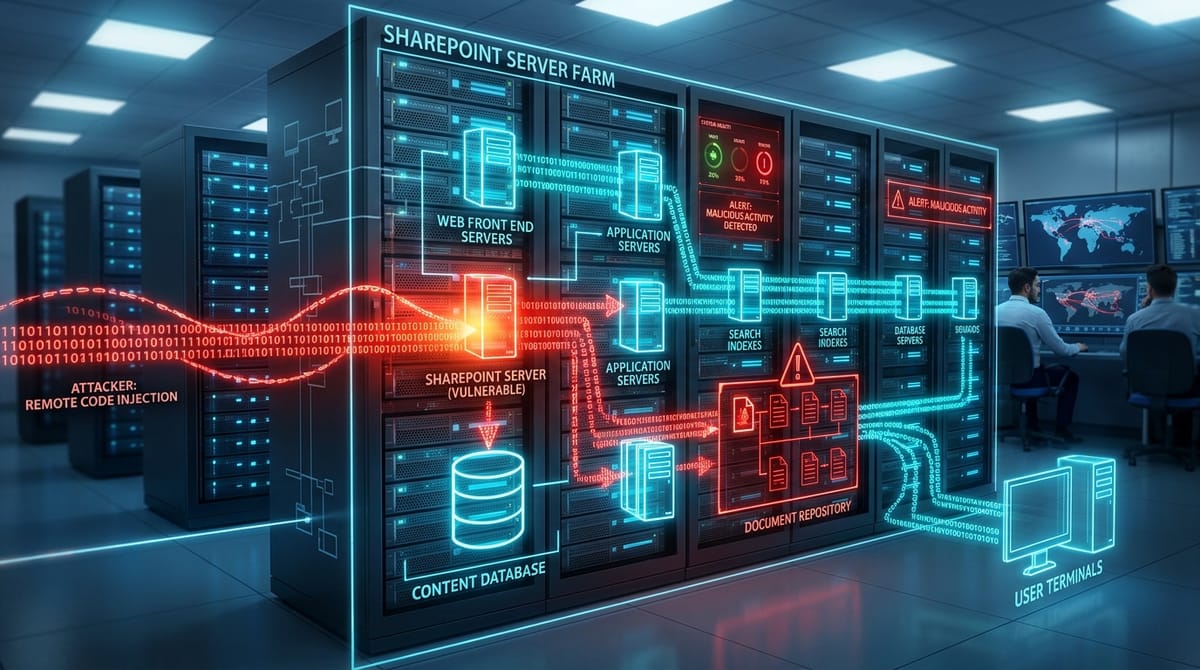
CVE-2026-65660 (CWE-94 / CWE-502)
Severity: HIGH / CRITICAL (CVSS 8.8)
Status: September 25, 2026 (Added to CISA KEV)
Affected Systems: Microsoft SharePoint Server 2016, 2019, Subscription Edition
Fixed In: Microsoft September 2026 Cumulative Update
CISA has added CVE-2026-65660 to its Known Exploited Vulnerabilities (KEV) catalog with a strict federal remediation deadline of September 28, 2026. Initially classified by Microsoft as a lower-severity spoofing flaw, threat intelligence researchers and incident responders revealed the vulnerability is a weaponized Remote Code Execution (RCE) flaw allowing authenticated and unauthenticated network attackers to run arbitrary code on on-premises SharePoint farms.
Vulnerability Mechanics & Deserialization Gadgets
The flaw lies in SharePoint's server-side workflow execution engine and custom form serialization pipeline. When processing incoming web requests containing serialized .resx or workflow definition XML files, SharePoint deserializes untrusted object streams using unsafe binary or XML formatters without validating type constraints:
// Vulnerable deserialization pattern inside Microsoft.SharePoint.Workflow
public object DeserializeWorkflowDefinition(Stream incomingStream) {
    // Flawed formatter without TypeFilterLevel.Low or custom Binder
    BinaryFormatter formatter = new BinaryFormatter();
    return formatter.Deserialize(incomingStream); // RCE via gadget payload
}
Adversaries chain this unsafe deserialization with common .NET gadget classes (such as TypeConfuseDelegate or ActivitySurrogateSelector) to instantiate an in-memory process execution payload. The resulting shellcode executes inside the context of the IIS application pool running SharePoint, typically granting access to farm database credentials and Active Directory domain tokens.
Observed In-the-Wild Campaign Patterns
State-sponsored espionage units and cyber extortion affiliates have targeted exposed SharePoint web applications via intranet pivot points and exposed corporate extranets. After achieving code execution in w3wp.exe, adversaries deploy lightweight web shells into SharePoint's layout directories:
C:\Program Files\Common Files\microsoft shared\Web Server Extensions\16\TEMPLATE\LAYOUTS\
Detection Telemetry & Threat Hunting
title: SharePoint Worker Process Spawning Shell
status: production
logsource:
  category: process_creation
  product: windows
detection:
  selection:
    ParentImage|endswith: '\w3wp.exe'
    Image|endswith:
      - '\cmd.exe'
      - '\powershell.exe'
      - '\pwsh.exe'
      - '\certutil.exe'
      - '\curl.exe'
  condition: selection
level: critical
PowerShell Audit Command for IIS Logs
# Search IIS logs for suspicious requests targeting SharePoint layouts
Get-ChildItem -Path "C:\inetpub\logs\LogFiles" -Recurse -Filter "*.log" |
Select-String -Pattern "POST /_layouts/15/.*.ashx|POST /_layouts/15/ToolShell" |
Select-Object -First 25
Remediation Checklist
- Apply Microsoft September 2026 Security Updates: Immediately apply the September 2026 Cumulative Update for Microsoft SharePoint Server 2016, 2019, and Subscription Edition across all Web Front End (WFE) and Application servers in the farm.
- Run SharePoint Configuration Wizard: Remember that installing the .exe/.msi patch is insufficient; you must execute
psconfig.exe -cmd upgrade -inplace b2b -waiton each server to finalize schema changes. - Enforce AMSI for SharePoint: Verify that the Antimalware Scan Interface (AMSI) integration is enabled in IIS to inspect in-memory .NET script execution.
- Restrict Extranet SharePoint Exposure: Place all SharePoint extranet endpoints behind web application firewalls (WAF) and require multi-factor pre-authentication.



