
ShinyHunters Syndicate Retaliation: Amsterdam Arrest Sparks Extortion Surge and Federal Contractor Leaks

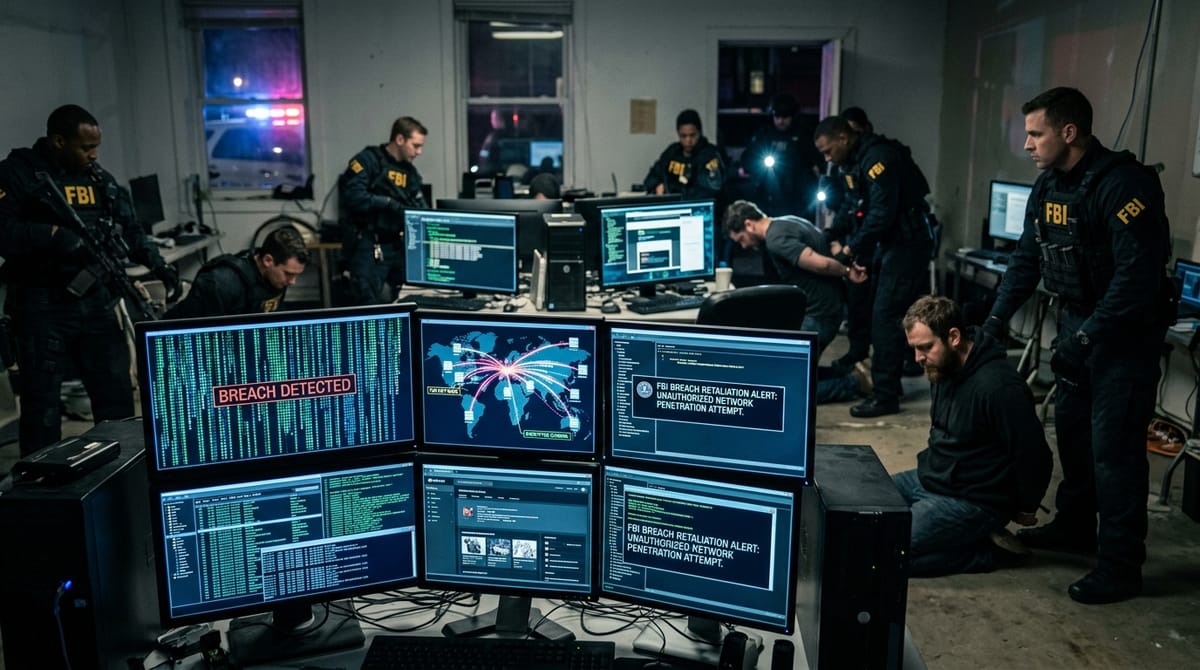
On September 28, 2026, Dutch police in Amsterdam confirmed the arrest of 24-year-old Pepijn van der Stap, an offensive security team lead previously convicted of data theft in 2023, for his alleged core role in the notorious ShinyHunters cybercrime syndicate. The arrest triggered an immediate retaliatory backlash from remaining syndicate members, who escalated extortion campaigns and published stolen datasets targeting law enforcement portals and major telecommunications providers.
The Double Life of an Offensive Security Lead
According to Dutch law enforcement releases, the suspect was employed full-time as an offensive security leader at a cybersecurity firm while simultaneously acting as a key broker, data negotiator, and intrusion coordinator for ShinyHunters. The arrest links back to major historical breaches, including the February 2026 intrusion into Dutch telecom giant Odido.
ShinyHunters Syndicate Ecosystem:
  ├── Core Brokers & Exploit Devs (e.g. Amsterdam cell)
  ├── Initial Access Brokers (Credential stuffing, SIM swapping, infostealers)
  └── Retaliatory Extortion Arm (Public leak sites, Telegram channels, media harassment)
Retaliatory Strikes: FBI Portal & Extortion Dumps
Within hours of news circulating regarding the Amsterdam arrest, ShinyHunters channels launched what the group termed a "retaliatory marketing campaign." The syndicate claimed responsibility for breaching an FBI applicant and contractor portal, threatening to leak sensitive vetting dossiers unless federal investigations were halted. This bold retaliation exemplifies the aggressive shift in cybercrime dynamics, where syndicates weaponize publicity and targeted harassment against law enforcement.
Corporate Defense Implications
- Vetting in Offensive Security Roles: Organizations must institute rigorous continuous background checks and privileged access auditing, even for vetted offensive security personnel.
- Infostealer Credential Exposure: ShinyHunters relies heavily on stealer logs purchased from dark web markets. Enterprises must monitor dark web channels for exposed employee sessions.
- Cloud Identity Protection: The syndicate frequently pivots through OAuth tokens and third-party SaaS integrations to bypass multifactor authentication.
Detection & Telemetry Indicators
SigninLogs
| where TimeGenerated >= ago(7d)
| where RiskLevelDuringSignIn in ("high", "medium")
| where UserAgent has_any ("Infostealer", "Go-http-client", "Python-urllib")
| summarize count() by UserPrincipalName, IPAddress, Location


