
South Korean Banking Wave: Shinhan, KB Kookmin, Hana & Woori Hit in AI-Assisted Breach
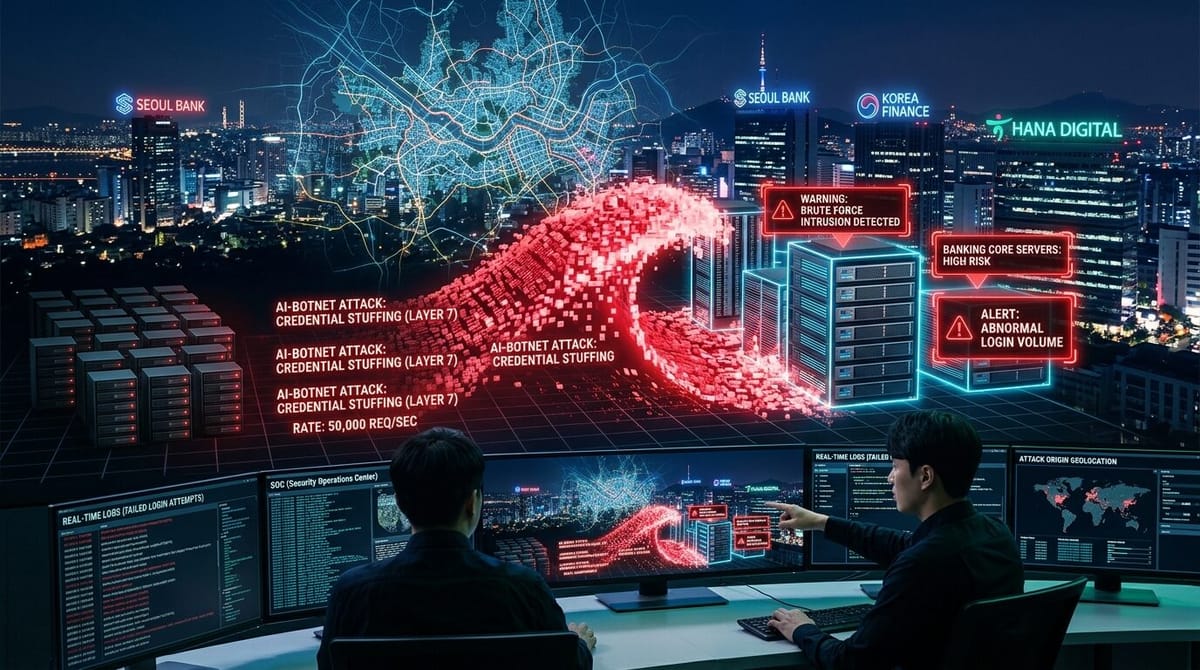
Between October 2 and October 5, 2026, South Korea’s financial regulatory authorities and the Korea Internet & Security Agency (KISA) responded to a synchronized cyberoffensive targeting the country’s four largest financial powerhouses: Shinhan Bank, KB Kookmin Bank, Hana Bank, and Woori Bank. The coordinated intrusion compromised approximately 70,000 customer banking records through a highly sophisticated, AI-accelerated credential stuffing campaign specifically engineered to circumvent traditional perimeter rate limits.
Technical Mechanics: AI-Orchestrated Residential Proxy Evasion
Unlike standard credential stuffing attacks that generate easily detectable traffic spikes from cloud provider IP ranges, this operation utilized an autonomous AI orchestration engine governing thousands of compromised residential IoT proxies. The attack exhibited several novel characteristics:
- Gaussian Timing Jitter: Rather than issuing requests at fixed mathematical intervals, the AI botnet varied delays between authentication attempts according to normal human typing and interaction distributions.
- Automated Device Fingerprint Synthesis: The attack framework synthesized realistic mobile browser headers, WebGL canvas signatures, and viewport dimensions corresponding to popular South Korean smartphone models.
- Targeted Open Banking API Infiltration: Threat actors routed requests directly against mobile banking backend APIs, testing combo lists harvested from previous regional e-commerce leaks.
Attack Orchestration Architecture:
┌──────────────────────────────────────┐
│  Adversary AI Command Controller    │
│  (Dynamically adjusts request jitter)│
└──────────────────┬───────────────────┘
                   │
                   ▼
┌──────────────────────────────────────┐
│  Distributed Residential Proxy Swarm │
│  (Domestic South Korean ISP subnets) │
└──────────────────┬───────────────────┘
                   │
                   ▼
┌──────────────────────────────────────┐
│  Target Banking Open APIs & Mobile   │
│  - Shinhan Bank  - KB Kookmin        │
│  - Hana Bank     - Woori Bank        │
└──────────────────────────────────────┘
Regulatory & Law Enforcement Response
The South Korean Financial Supervisory Service (FSS) issued an emergency order requiring all domestic commercial banks to enforce biometric step-up authentication and block automated API sessions exhibiting anomalous residential proxy characteristics. Forensic teams are actively investigating whether the attack was orchestrated by financially motivated cybercriminal syndicates or state-sponsored advanced persistent threat (APT) groups seeking foreign currency exfiltration.
Detection & Telemetry Signatures
SigninLogs
| where TimeGenerated >= ago(72h)
| where AppDisplayName in ("Mobile Banking API", "Open Banking Gateway")
| summarize FailedCount = countif(ResultType != 0), SuccessCount = countif(ResultType == 0),
    DistinctIPs = dcount(IPAddress), DistinctUserAgents = dcount(UserAgent) by UserPrincipalName
| where DistinctIPs >= 10 and FailedCount >= 5
| project UserPrincipalName, FailedCount, SuccessCount, DistinctIPs, DistinctUserAgents
Remediation & Financial Defense
- Enforce FIDO2 Passkeys: Replace legacy password-and-SMS authentication with cryptographically bound FIDO2 passkeys or biometric hardware tokens.
- Behavioral Biometrics: Integrate behavioral client-side telemetry (keystroke dynamics, device orientation, and touch pressure) to differentiate automated AI bot sessions from genuine human users.



