
ShinyHunters Syndicate Operator Detained in Jordan: FBI Cooperation and Extortion Fallout
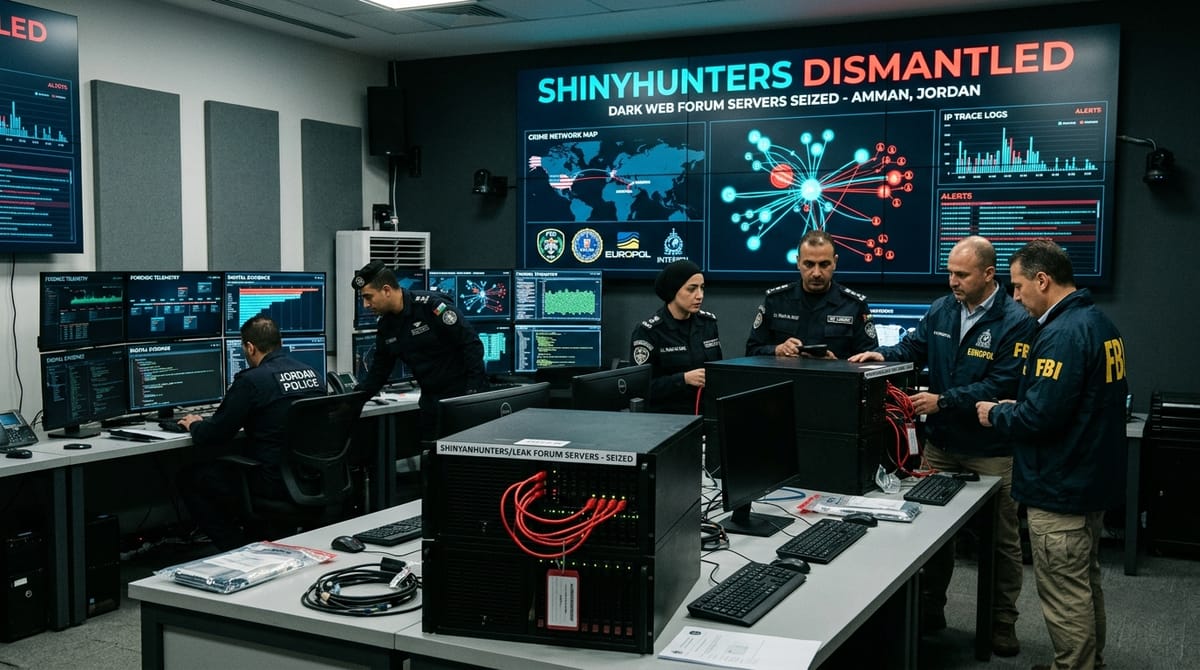
In a major blow to one of the most prolific cyber extortion cartels in history, international law enforcement authorities confirmed over the October 3–5, 2026 weekend that a senior operator of the ShinyHunters syndicate has been detained in Amman, Jordan. The operative is currently cooperating with the Federal Bureau of Investigation (FBI), providing forensic investigators with access to dark web infrastructure, encrypted communications, and unreleased victim extortion databases.
Background: From Amsterdam Arrest to Retaliatory Threats
The detention in Jordan follows the September 2026 arrest of a core ShinyHunters administrator in Amsterdam, Netherlands. In response to that arrest, the syndicate launched an aggressive retaliatory extortion campaign, publicly threatening to release compromised data allegedly stolen from US federal contractor networks and law enforcement communication systems. However, rapid joint coordination between the Jordanian General Intelligence Directorate (GID), Interpol, and the FBI intercepted the operative before additional exfiltrated data could be dumped.
Forensic Value of Recovered Infrastructure
According to sources familiar with the ongoing operation, federal investigators have obtained control over key command servers and private messaging channels used to coordinate extortion demands. The recovered material includes:
- Private cryptographic keys used to sign extortion communications on underground breach forums.
- Unreleased corporate datasets encompassing telecom, retail, and technology firms targeted during summer 2026.
- Transaction ledgers tracing cryptocurrency ransom payments laundered through cross-chain privacy pools.
The Shift in Cybercrime Syndicates Under Pressure
The capture of key personnel in both Western Europe and the Middle East illustrates the shrinking safe haven for high-profile cybercriminals. As international treaties and cyber intelligence sharing intensify, syndicates like ShinyHunters are fracturing into smaller, more chaotic splinter cells, often engaging in hasty, desperate extortion attempts before complete operational dissolution.
Defensive Posture for Potentially Compromised Organizations
- Continuous Credential Monitoring: Actively monitor underground intelligence feeds for historical ShinyHunters credential caches that may now be abandoned or leaked by disgruntled affiliates.
- Revoke Stale Third-Party Access: Enforce complete credential rotations on all corporate cloud portals (Salesforce, Snowflake, AWS) where legacy API tokens were historically stored.



