CVE-2026-85880: Windows ALPC Elevation of Privilege Zero-Day Under Active Exploitation — CISA KEV Analysis
Technical teardown of CVE-2026-85880 in Windows ALPC: kernel port object memory corruption, SYSTEM token privilege escalation, and CISA KEV remediation.

📌
Security Roundup Series: Week of September 11, 2026 • 6 min read deep dive
Microsoft's September 2026 Patch Tuesday addressed an actively exploited zero-day elevation of privilege flaw in the Windows Advanced Local Procedure Call (ALPC) subsystem (CVE-2026-85880), cataloged immediately in CISA KEV.
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-85880 (CWE-269: Improper Privilege Management in ALPC Port Objects)
Severity: High / Actively Exploited (CVSS 7.8)
Status: 🚨 In-the-Wild Zero-Day Exploitation / Added to CISA KEV
Affected Systems: Windows 10, Windows 11, Windows Server 2019, 2022, and 2025
Kernel Memory Corruption via ALPC Port Objects
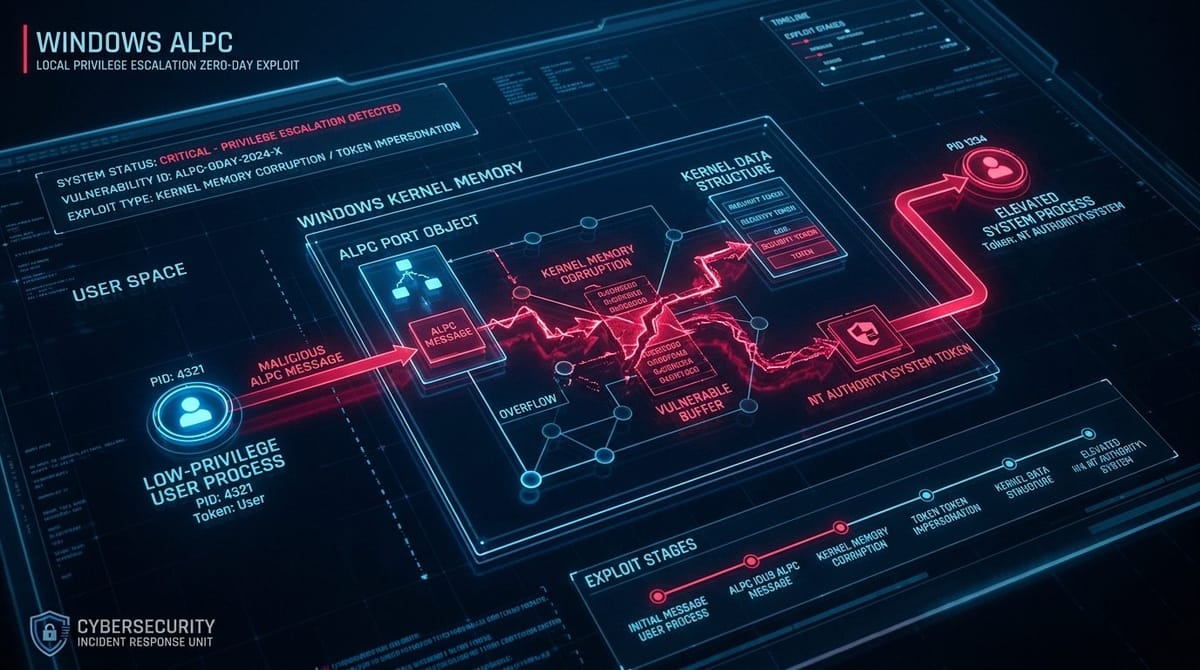
The vulnerability exists in how the Windows kernel handles message attribute structures during inter-process communication over ALPC. A local attacker operating with low privileges can construct malformed port attributes, triggering an integer underflow that overwrites token security pointers in kernel memory and elevating the process token to NT AUTHORITY\SYSTEM.
Exploit Chain Dynamics
- Initial Sandbox Execution: Attackers compromise a standard user application or browser tab.
- ALPC Message Dispatch: The payload initiates rapid asynchronous ALPC message passing to a privileged system port.
- Token Impersonation: Memory corruption overwrites the process security descriptor, granting full administrative and kernel capabilities.
🧭
More Deep Dives from this Roundup:
CVE-2026-85880: Windows ALPC Privilege Escalation Zero-Day
CVE-2026-81963: Windows Update Stack Zero-Day Breakdown
CVE-2026-12744 / 12745: Ivanti Neurons for ITSM Dual CVSS 9.8 RCE
CVE-2026-83527: Ivanti Sentry Authentication Bypass Analysis
Enterprise Defense: Mitigating September 2026 Patch Tuesday Zero-Days
← Return to Weekly Overview: Full Roundup