
CVE-2026-81963: Windows Update Stack Improper Link Resolution Zero-Day Exploit Breakdown
Technical breakdown of CVE-2026-81963 in the Windows Update Stack: symlink race conditions, arbitrary file overwrite, and SYSTEM escalation.

📌
Security Roundup Series: Week of September 11, 2026 • 5 min read deep dive
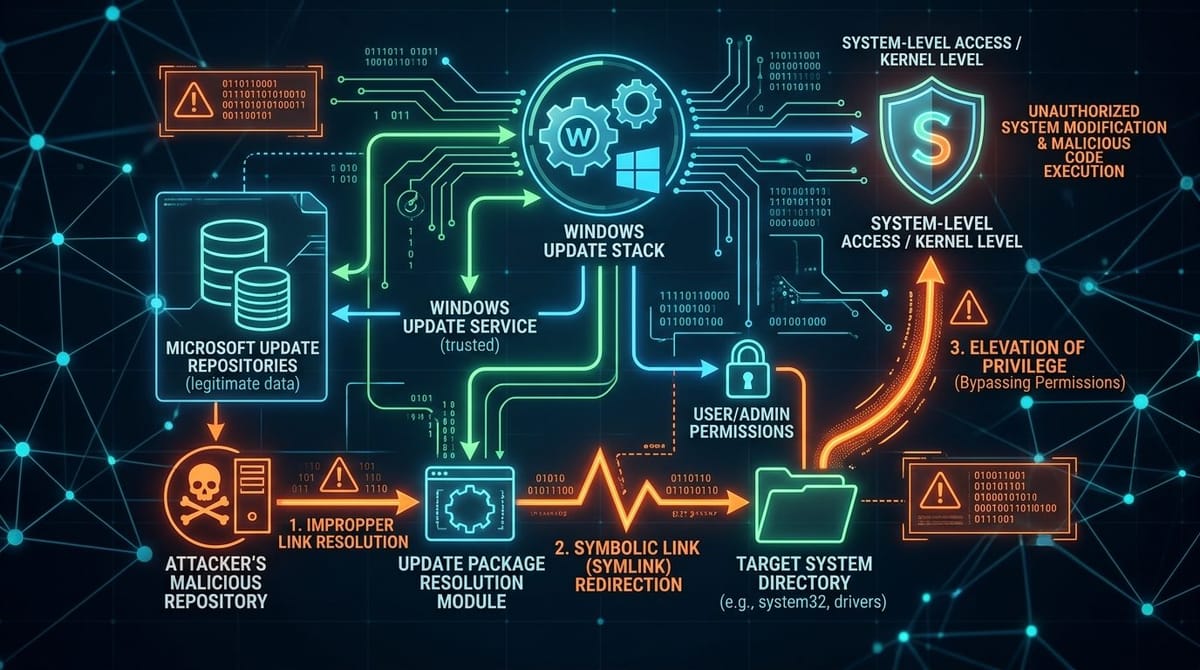
A second actively exploited zero-day vulnerability in the Windows Update Stack (CVE-2026-81963) allows local attackers to weaponize improper link resolution and symbolic link redirection to bypass filesystem ACLs and gain SYSTEM privileges.
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-81963 (CWE-59: Improper Link Resolution Before File Access ('Link Following'))
Severity: High / Actively Exploited (CVSS 7.8)
Status: 🚨 Active In-the-Wild Exploitation / Added to CISA KEV
Affected Systems: Windows 10, Windows 11, and Windows Server platforms
Symbolic Link Redirection Mechanics
The Windows Update service creates temporary staging directories during package validation. Attackers plant directory junctions and NTFS symlinks pointing to protected system directories (e.g., System32\drivers). When the update service sets permissive DACLs on the destination, the attacker gains arbitrary write access to critical OS binaries.
🧭
More Deep Dives from this Roundup:
CVE-2026-85880: Windows ALPC Privilege Escalation Zero-Day
CVE-2026-81963: Windows Update Stack Zero-Day Breakdown
CVE-2026-12744 / 12745: Ivanti Neurons for ITSM Dual CVSS 9.8 RCE
CVE-2026-83527: Ivanti Sentry Authentication Bypass Analysis
Enterprise Defense: Mitigating September 2026 Patch Tuesday Zero-Days
← Return to Weekly Overview: Full Roundup

