en
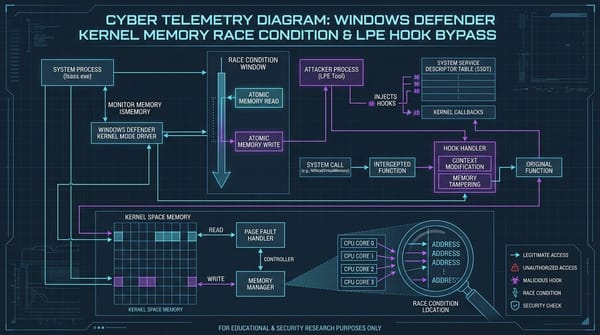
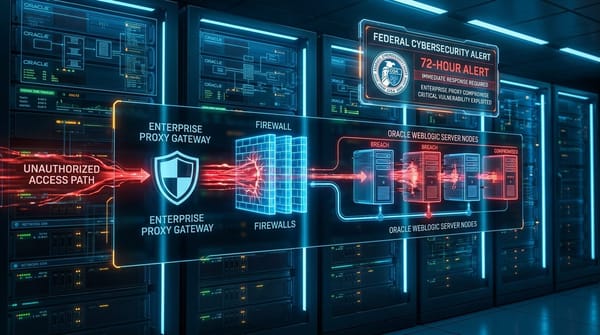
CVE-2026-21962: Oracle WebLogic Proxy Plug-in & HTTP Server Improper Access Control — CISA 72-Hour Federal Directive Breakdown
Deep dive into CVE-2026-21962: how threat actors bypass Oracle WebLogic reverse proxy security boundaries, and why CISA mandated an emergency 72-hour patch deadline.