Latest

Enterprise Cybersecurity Hardening Architecture Blueprint

guides

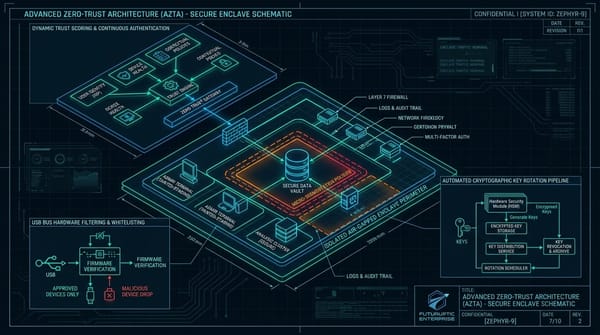
Enterprise Hardening Blueprint: Air-Gapped Network Isolation, Migration Appliance Security & Kernel DSP Mitigations

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive This weekend's threat landscape demonstrated that advanced attackers exploit blind spots across every layer of the enterprise stack: unmonitored CI/CD developer tokens (Internet Archive), kernel DSP hardware memory management (Qualcomm CVE-2024-43047), internal perimeter migration
By James Luther
American Water Critical Infrastructure Intrusion and SCADA Defense

News

American Water Cyber Intrusion: Precautionary IT Disconnection and Billing Pause Protects Physical SCADA Enclaves

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: American Water (Camden, New Jersey) Threat Actor / Attribution: Unattributed Threat Actor / Suspected Extortion Group Impact / Records Compromised: Corporate Enterprise IT Networks, Customer Billing Systems, MyWater Web Application Initial Attack Vector: Network Intrusion Detected

By James Luther
GoldenJackal APT Air-Gapped Cyberespionage USB Malware

News

GoldenJackal APT Infiltrates Air-Gapped Diplomatic Networks: ESET Exposes Custom USB Bridge Toolset

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Diplomatic Missions & European Union Governmental Entities Threat Actor / Attribution: GoldenJackal (Russian-Aligned Cyberespionage APT) Impact / Records Compromised: Classified Diplomatic Cables, Internal Mails, Encryption Keys, and Sensitive Government Dossiers Initial Attack Vector: Air-Gap Bridging

By James Luther
Fidelity Investments Customer Data Breach and SSN Exposure

News

Fidelity Investments Discloses Security Breach: 77,000 Customer Records and SSNs Compromised via Rogue Accounts

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Fidelity Investments (Boston, Massachusetts) Threat Actor / Attribution: Unidentified Cybercrime Actor Impact / Records Compromised: 77,099 Customer Records (Full Names, Addresses, Social Security Numbers, Financial Document Images) Initial Attack Vector: Creation of Two Fraudulent

By James Luther
Casio Computer Cyberattack and Underground Ransomware Extortion

News

Casio Computer Hit by Underground Ransomware: 200 GB Exfiltrated in Supply Chain and Operations Interruption

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Casio Computer Co., Ltd. (Tokyo, Japan) Threat Actor / Attribution: Underground Ransomware Syndicate Impact / Records Compromised: 200 GB Exfiltrated; 8,478 Individuals Compromised (6,456 Employees, 1,931 Partners, 91 Customers) Initial Attack Vector:

By James Luther
Palo Alto Networks Expedition Remote Code Execution Vulnerabilities

News

Palo Alto Networks Expedition RCE Chain: CVE-2024-9463 & CVE-2024-5910 Expose Enterprise Firewall Secrets

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2024-9463 & CVE-2024-5910 (CWE-78 (OS Command Injection) & CWE-306 (Missing Authentication)) Severity: CRITICAL (CVSS 9.9 (CVE-2024-9463) / 9.3 (CVE-2024-5910)) Status: Actively Exploited in the Wild; Added to CISA KEV (Mandatory Federal Remediation)

By James Luther
Qualcomm Snapdragon FastRPC DSP Memory Corruption Zero-Day

News

CVE-2024-43047: Qualcomm FastRPC DSP Memory Corruption Zero-Day Exploited in Targeted Spyware Campaigns

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🛡️Vulnerability Intelligence: CVE ID: CVE-2024-43047 (CWE-416 (Use-After-Free)) Severity: HIGH (CVSS 7.8) Status: Actively Exploited In-The-Wild Zero-Day; Added to CISA KEV on Oct 8, 2024 (BOD 22-01) Affected Systems: Qualcomm Snapdragon Chipsets (FastRPC driver handling HLOS memory

By James Luther
Internet Archive Cyber Breach and SN_BlackMeta Attack

News

Internet Archive Under Multi-Vector Siege: 31M User Accounts Leaked via Compromised GitLab Token and DDoS Campaign

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Internet Archive (archive.org & The Wayback Machine) Threat Actor / Attribution: Hacktivist Syndicate "SN_BlackMeta" & Unattributed Intruders Impact / Records Compromised: 31,081,179 User Accounts (Emails, Screen Names, Bcrypt Passwords,

By James Luther
ColibriSec Weekend Security Roundup October 12 2026

News

Security Roundup: Internet Archive 31M Breach, Qualcomm FastRPC Zero-Day, Casio Ransomware, Palo Alto Expedition RCE (Weekend Edition - October 12, 2026)

Executive Summary: The weekend of October 9–12, 2026, unleashed a devastating confluence of nation-state cyberespionage, catastrophic consumer database exfiltrations, targeted commercial spyware zero-days, and critical infrastructure intrusions. Headlining this weekend's alerts, the Internet Archive (archive.org) fell victim to a catastrophic multi-vector attack: a 31-million user account

By James Luther
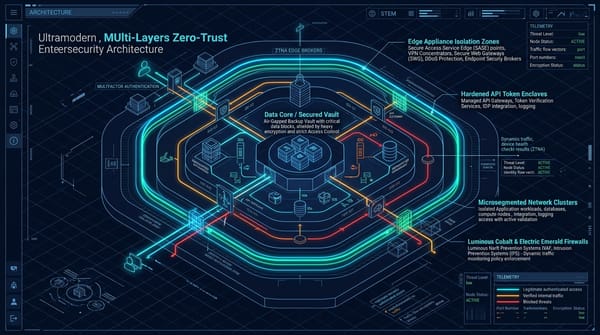
Enterprise Hardening Blueprint Architectural Diagram

guides

Enterprise Hardening Blueprint: Protecting Edge Gateways, Backup Systems, and Mobile Push Token Pipelines

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🛡️ColibriSec Engineering Defense Blueprint: Actionable architectural specifications, network segmentation rules, and configuration templates to fortify enterprise infrastructure against the vulnerabilities and threat tactics disclosed during the week of October 9, 2026. The events of the past seven

By James Luther
Q3 2026 Ransomware Threat Statistics and Extortion Trends

News

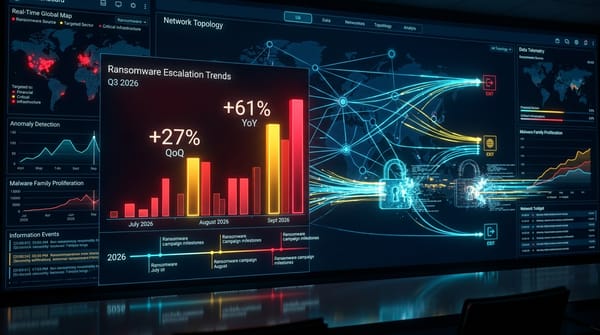
Q3 2026 Threat Landscape Analysis: Ransomware Surge (+61% YoY) and the Strategic Pivot to Pure Exfiltration

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️Q3 2026 RANSOMWARE THREAT INTELLIGENCE SYNTHESIS Quarterly cybercrime analytics released October 9, 2026, documenting a massive surge in extortion activity and structural operational pivots. Ransomware incident volume rose 27% compared to Q2 2026 and surged 61% year-over-year

By James Luther
Apache HTTP Server Security Vulnerabilities Architecture

News

Apache HTTP Server Security Advisory: Critical RCE and Request Splitting Vulnerabilities in Version 2.4.68

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-42356 & CVE-2026-42528 (CWE-444 (Inconsistent Interpretation of HTTP Requests) / CWE-120 (Buffer Overflow)) Severity: HIGH / CRITICAL (CVSS 8.8 / 7.5) Status: Official Vendor Security Release Issued October 9, 2026 Affected Systems: Apache HTTP

By James Luther