GoldenJackal APT Infiltrates Air-Gapped Diplomatic Networks: ESET Exposes Custom USB Bridge Toolset

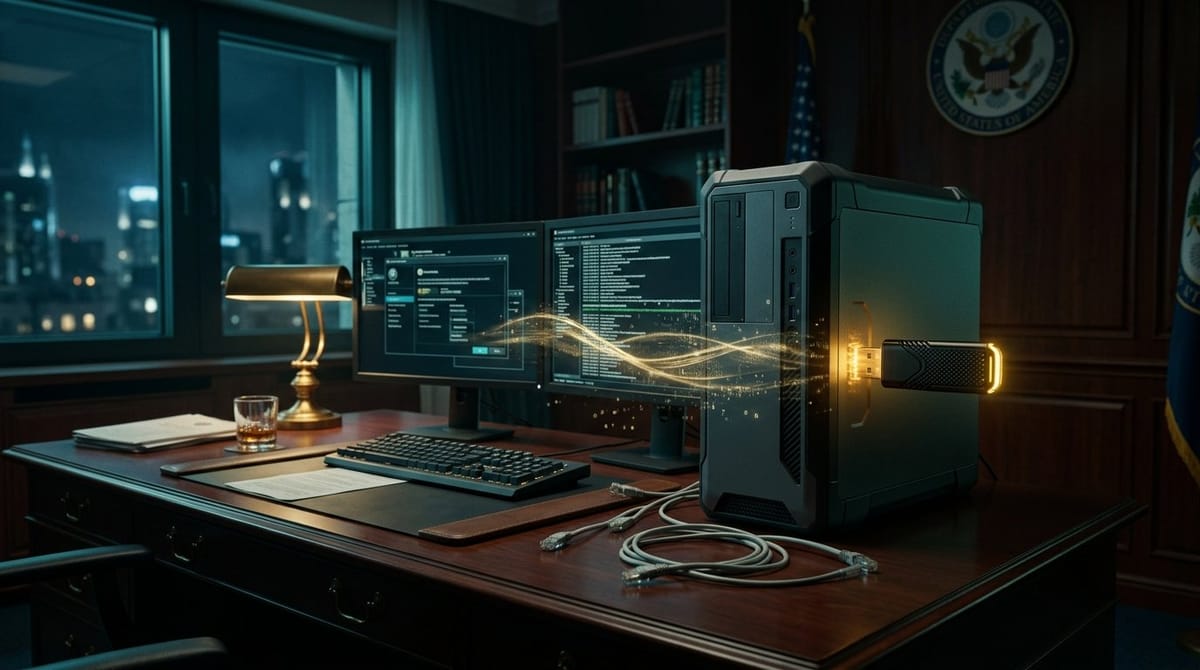
In a comprehensive technical research publication released by ESET over the weekend, threat researchers unveiled an extraordinary cyberespionage campaign executed by GoldenJackal, a sophisticated advanced persistent threat (APT) actor. The group successfully compromised and continuously exfiltrated data from physically isolated, air-gapped networks belonging to a South Asian embassy in Belarus and an unnamed European Union government agency. To bypass the physical air-gap, GoldenJackal developed and deployed two successive generations of purpose-built USB drive bridging malware, transforming ordinary removable storage devices into covert data mules.
The Architecture of the Air-Gap Bridge
Air-gapped systems are completely disconnected from the public internet and local enterprise networks to safeguard highly classified data. GoldenJackal bypassed this barrier through an automated three-stage lifecycle:
GoldenJackal Air-Gap Bridging Lifecycle:
┌─────────────────────────┐          USB Inserted          ┌───────────────────────────────┐
│ Internet-Connected Host │ ─────────────────────────────> │ Removable USB Drive           │
│ (Infected with          │                                │ (Injected with GoldenDealer   │
│  GoldenDealer)          │ <───────────────────────────── │  & Staged Collector Payloads) │
└─────────────────────────┘      Exfiltrates Stolen Data   └──────────────┬────────────────┘
                                                                          │
                                                      Physically Carried  │  Inserted into
                                                      Across Air-Gap      │  Air-Gapped Machine
                                                                          ▼
                                                           ┌───────────────────────────────┐
                                                           │ Air-Gapped Secure Workstation │
                                                           │ (GoldenAce / GoldenHowl Run,  │
                                                           │  Harvest Cables & Write to USB│
                                                           └───────────────────────────────┘
The Malware Toolset Deconstructed
ESET's analysis documented a major evolutionary leap between GoldenJackal's early 2019–2021 campaigns and their 2022–2024 operations:
1. GoldenDealer (The Infection Vector)
Installed on internet-connected hosts via phishing or secondary backdoors, GoldenDealer runs as a silent background daemon monitoring Windows device arrival notifications (WM_DEVICECHANGE). When a USB storage volume is connected, GoldenDealer silently copies a hidden malicious payload and an autorun/shortcut launcher into a hidden folder on the drive.
2. GoldenAce (The Air-Gapped Stager)
In the newer campaign targeting EU government agencies, GoldenJackal transitioned from Python to modular Go (Golang) binaries. Once executed on the air-gapped endpoint, GoldenAce acts as an execution coordinator. It scans the air-gapped machine for target extensions (.doc, .docx, .pdf, .xls, .pgp, .eml), packages them into password-protected encrypted archives, and writes the staged loot back into hidden sectors on the USB drive.
3. GoldenHowl & GoldenRobo (The Collection Modules)
Specialized modular backdoors capable of dumping local password hashes, capturing system hardware configurations, and harvesting Outlook/Thunderbird mailbox stores.
Detection Telemetry & Threat Hunting
title: Suspicious Process Execution from Removable Drive Root
status: production
logsource:
    product: windows
    service: sysmon
detection:
    selection:
        EventID: 1
        Image|endswith:
            - 'cmd.exe'
            - 'powershell.exe'
            - '
undll32.exe'
        CommandLine|contains:
            - ':~'
            - ':System Volume Information'
            - ':RECYCLER'
    condition: selection
level: critical
Remediation & Air-Gap Defense Blueprint
- Hardware USB Port Lockdown: Physically disable or epoxy-seal USB ports on air-gapped endpoints. Enforce hardware-enforced USB port blocking via Group Policy and kernel-level endpoint protection.
- Deploy Optical Data Diodes: If data must enter an air-gapped enclave, use hardware-enforced unidirectional optical data diodes rather than bidirectional removable USB drives.
- Automated USB Sanitation Kiosks: If removable media is strictly unavoidable, mandate scanning through dedicated, multi-AV "sheep-dip" air-gap transfer kiosks that wipe and reformat media before and after transit.