American Water Cyber Intrusion: Precautionary IT Disconnection and Billing Pause Protects Physical SCADA Enclaves

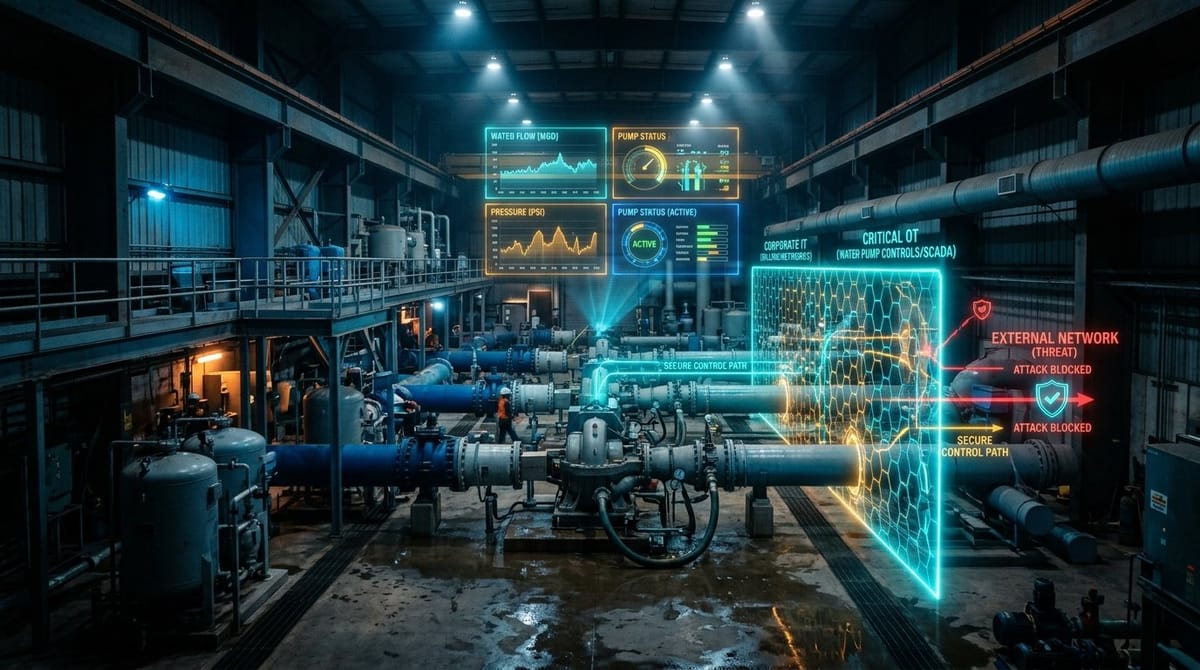
American Water Works Company, Inc.—the largest publicly traded water and wastewater service provider in the United States, providing drinking water to over 14 million people across 14 states—disclosed a major cyber incident that forced an emergency shutdown of its corporate IT network, customer portal, and billing operations. Prompt action by security teams prevented the threat actors from pivoting into operational technology (OT) networks: water treatment facilities, chemical dosers, and SCADA valve controls operated uninterrupted behind air-gapped industrial enclaves.
Incident Overview: The Anatomy of a Precautionary IT Shutdown
On October 3, 2024, American Water detected unauthorized activity on corporate servers. Recognizing the acute national security risks inherent to water utilities, leadership executed an aggressive containment playbook:
- Customer Systems Taken Offline: The online customer portal (MyWater), automated payment processing gateways, and customer support call centers were severed from internal systems.
- Billing Moratorium: The company officially paused billing schedules, announcing that no customers would face late payment fees or service disconnections during the incident.
- OT/SCADA Segregation Verification: Industrial control system (ICS) engineers verified that all operational networks controlling physical water treatment and distribution maintained complete physical and logical isolation from corporate IT domains.
- System Restoration: By October 10–12, 2026, after third-party forensic clearance by cybersecurity specialists, billing and customer portals were securely reactivated.
The IT vs. OT Threat Model in Critical Infrastructure
The American Water incident serves as a textbook study in critical infrastructure defense. In modern utility architectures, the Purdue Enterprise Reference Architecture (PERA) defines strict security boundaries:
Purdue Model Defense Implementation at American Water:
┌─────────────────────────────────────────────────────────┐
│ Level 4/5: Enterprise IT Network                        │  <-- ATTACK OCCURRED HERE
│ (Customer Billing, MyWater Portal, Email, Corporate AD) │      (Contained & Shutdown)
└───────────────────────────┬─────────────────────────────┘
                            │
              ══════════════╪══════════════ [AIR-GAP / FIREWALL ISOLATION]
                            │
┌───────────────────────────┴─────────────────────────────┐
│ Level 3: Industrial DMZ & Operations Management         │
│ (Historians, Engineering Workstations, Asset Inventory) │
└───────────────────────────┬─────────────────────────────┘
                            │
┌───────────────────────────┴─────────────────────────────┐
│ Level 1/2: Control Systems & Physical OT                │  <-- ZERO COMPROMISE
│ (PLCs, RTUs, SCADA Valves, Chemical Dosing Pumps)       │      (100% Water Safety Maintained)
└─────────────────────────────────────────────────────────┘
Because American Water maintained strict firewall rule sets prohibiting direct routable connections from Level 4 enterprise IT into Level 1/2 SCADA controllers, the attackers could not manipulate water quality, valve pressures, or chemical levels, avoiding catastrophic public health impacts.
Key Incident Response Lessons for Utility Operators
- Decouple Billing from Water Delivery: Enterprise billing outages must never impede physical utility delivery. Automated fail-safes must keep pumps running even when corporate Active Directory is taken down.
- Pre-Staged Outage Communications: American Water minimized public panic by immediately announcing billing suspensions and confirming water potability across municipal news channels.
- Continuous SCADA Perimeter Verification: Utility CISOs must regularly execute tabletop simulations verifying that compromising an enterprise web application cannot lead to lateral movement into operational PLCs.