
Enterprise Zero-Trust Defense: Securing Network Access Control (NAC) Appliances and Hypervisor Perimeters
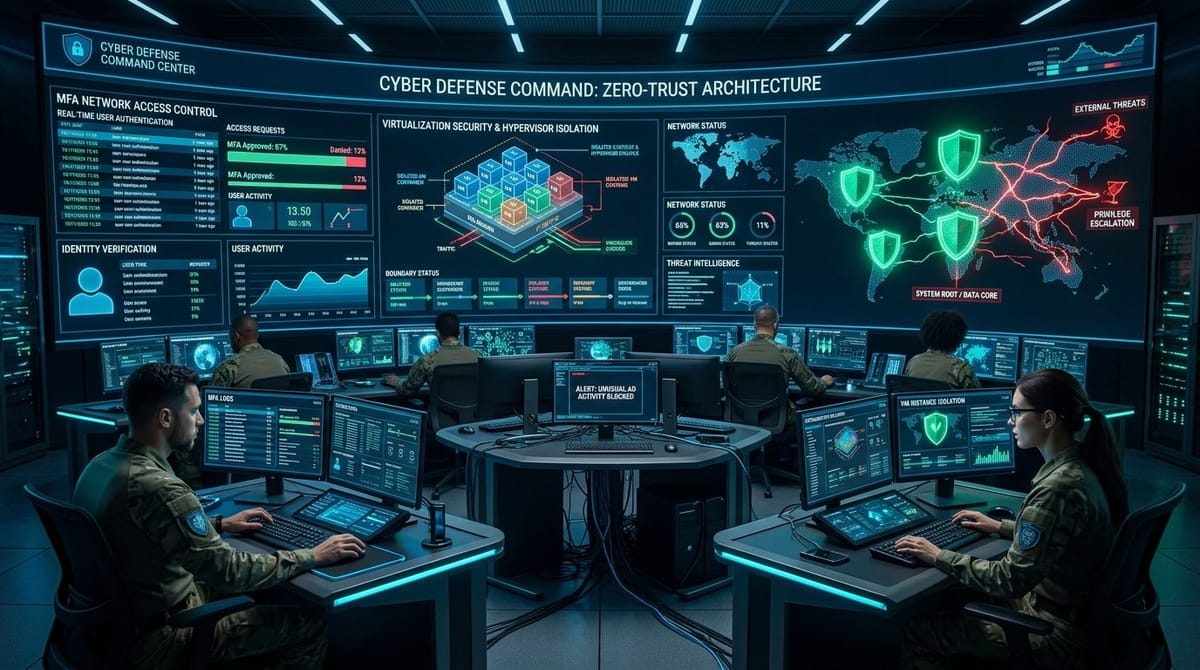
Strategic defense blueprint for hardening enterprise Network Access Control (NAC) gateways, hypervisors, and backup infrastructure against active zero-days.

📌
Security Roundup Series: Week of September 18, 2026 • 5 min read deep dive
With attackers weaponizing zero-day RCE flaws against network access control systems (Cisco ISE) and hypervisor escapes in VMware, security architects must implement strict out-of-band segmentation and zero-trust identity policies.
🏛️
Incident Overview:
Threat Actor / Attribution: Advanced Persistent Threat (APT) Groups & Ransomware Cartels
Zero-Trust Defense Roadmap
- Patch Cisco ISE Policy Nodes Immediately: Restrict management port access (TCP 80, 443, 9060) to dedicated administrative subnets.
- Harden Hypervisor Boundaries: Update VMware Workstation and Fusion, disable unused virtual USB/SVGA hardware sharing, and isolate hypervisor host networks.
🧭
More Deep Dives from this Roundup:
CVE-2026-76460: Cisco ISE Maximum CVSS 10.0 Zero-Day Analysis
VMSA-2026-0007: VMware Workstation & Fusion Hypervisor Flaws
CVE-2026-87886: Acronis Cyber Protect Backup LPE in CISA KEV
Palo Alto GlobalProtect & Prisma Access Security Wave
Zero-Trust Defense: Securing NAC Appliances & Hypervisors
← Return to Weekly Overview: Full Roundup



