
CVE-2026-87886: Acronis Cyber Protect Backup Local Privilege Escalation Added to CISA KEV Catalog
Technical teardown of CVE-2026-87886 in Acronis Cyber Protect: backup agent privilege escalation, shadow copy tampering, and CISA KEV remediation.

📌
Security Roundup Series: Week of September 18, 2026 • 5 min read deep dive
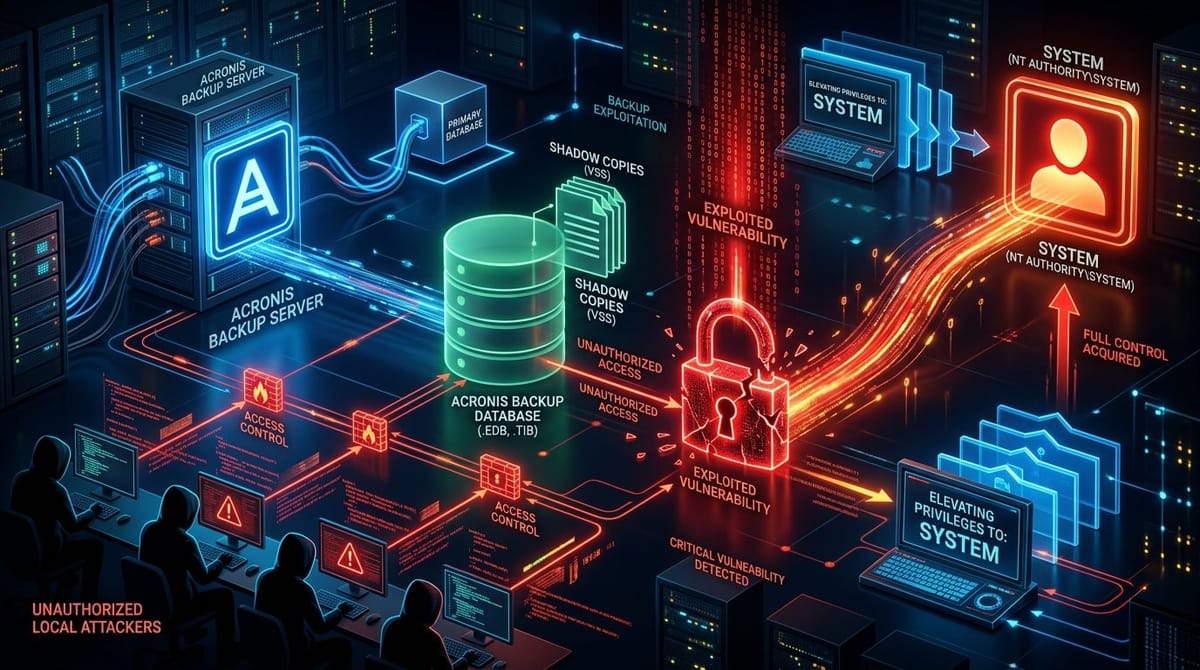
A local privilege escalation vulnerability in Acronis Cyber Protect Backup Agent (CVE-2026-87886) has been cataloged in CISA KEV following in-the-wild exploitation by ransomware operators to hijack backup repositories and wipe shadow copies.
🛡️
Vulnerability Intelligence:
CVE ID:
CVE-2026-87886 (CWE-269: Improper Privilege Management in Backup Agent Service)
Severity: High (CVSS 7.8)
Status: 🚨 Added to CISA KEV Catalog / Active Ransomware Targeting
Affected Systems: Acronis Cyber Protect Windows Agent versions prior to update C24.08
Ransomware Pre-Encryption Tactics
Threat actors deploy low-privilege malware that exploits unquoted service paths and permissive IPC handles in the Acronis backup daemon. By elevating to SYSTEM, the adversary deletes immutable backup snapshots before launching full-scale volume encryption.
🧭
More Deep Dives from this Roundup:
CVE-2026-76460: Cisco ISE Maximum CVSS 10.0 Zero-Day Analysis
VMSA-2026-0007: VMware Workstation & Fusion Hypervisor Flaws
CVE-2026-87886: Acronis Cyber Protect Backup LPE in CISA KEV
Palo Alto GlobalProtect & Prisma Access Security Wave
Zero-Trust Defense: Securing NAC Appliances & Hypervisors
← Return to Weekly Overview: Full Roundup



