
CVE-2026-63520: Microsoft SharePoint's Remote Code Execution Vulnerability
Technical breakdown of CVE-2026-63520 and how threat actors chain SharePoint input validation bugs to achieve pre-auth remote code execution.

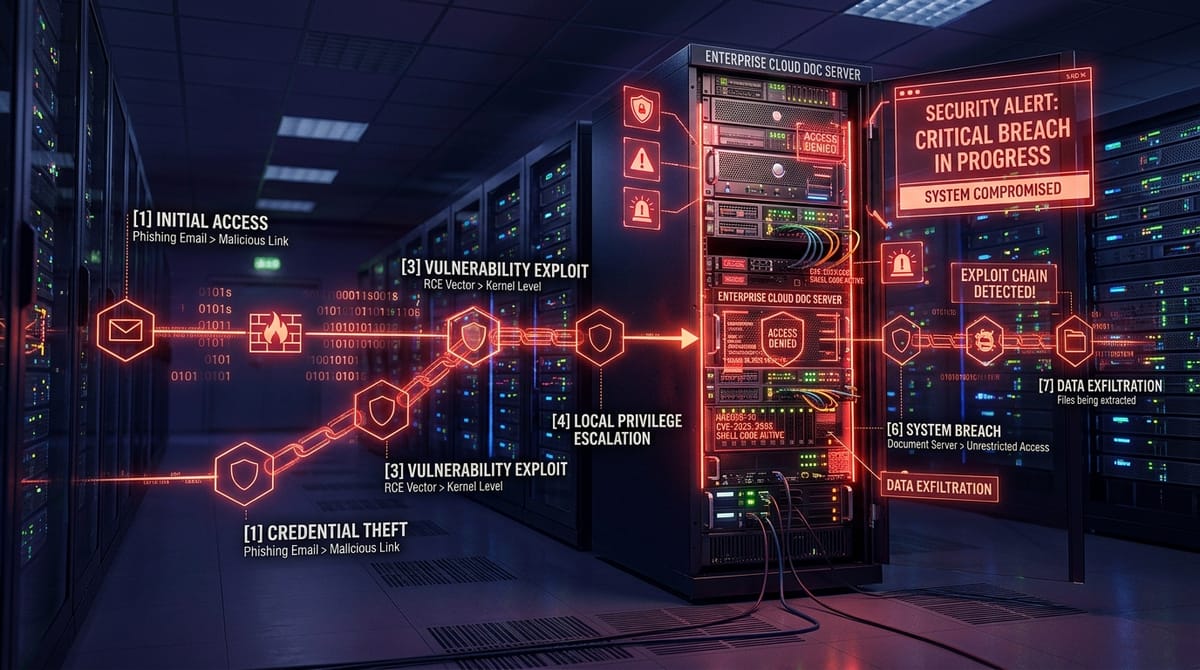
A high-severity remote code execution flaw in Microsoft SharePoint Server can be chained with upstream authentication bypass vectors to achieve full server takeover across corporate intranet environments.
CVE-2026-63520 (Chained with CVE-2026-55040) (CWE-20: Improper Input Validation)
Severity: High / Critical in Chain (CVSS 8.1 (Standalone) / 9.8 (Chained))
Status: ⚠️ Active Exploit Chains Reported in Enterprise Environments
Affected Systems: Microsoft SharePoint Enterprise Server 2016, 2019, and SharePoint Subscription Edition
Fixed In: August 2026 SharePoint Security Update
Attack Chain Anatomy
SharePoint Server's XML deserialization and business data connectivity endpoints process complex document schemas. In CVE-2026-63520, an improper input validation flaw inside the server's control rendering pipeline allows an authenticated user to inject malicious .NET serialization payloads into the page compilation pipeline.
Crucially, security researchers have demonstrated that when combined with recent SharePoint authentication-bypass techniques (such as CVE-2026-55040), remote attackers can trigger this execution path without prior credentials, executing arbitrary PowerShell and binary payloads under the w3wp.exe IIS application pool identity.
Forensic Indicators & Defense
/_layouts/15/ endpoints returning HTTP 500 errors accompanied by unusual payload sizes.
Hunt for child processes spawned by w3wp.exe (e.g. cmd.exe, powershell.exe, certutil.exe).
Inspect the SharePoint virtual directories for newly created .aspx or .ashx webshells.

