
CVE-2026-49869: Kestra OSS Workflow Orchestration Command Injection Vulnerability & CI/CD Defense
Technical teardown of CVE-2026-49869 in Kestra OSS: command injection in workflow task runners, container compromise, and CISA KEV mitigation.

📌
Security Roundup Series: Weekend Edition • September 7, 2026 • 5 min read deep dive
An OS command injection vulnerability in Kestra OSS (CVE-2026-49869), cataloged in CISA KEV, allows remote attackers to compromise workflow orchestration clusters and execute arbitrary bash commands inside task runner containers.
🚨
Vulnerability Intelligence:
CVE ID:
CVE-2026-49869 (CWE-78: Improper Neutralization of Special Elements used in an OS Command)
Severity: Critical (CVSS 9.8)
Status: 🚨 Added to CISA KEV Catalog / Active CI/CD Orchestration Risk
Affected Systems: Kestra OSS versions prior to 0.18.2
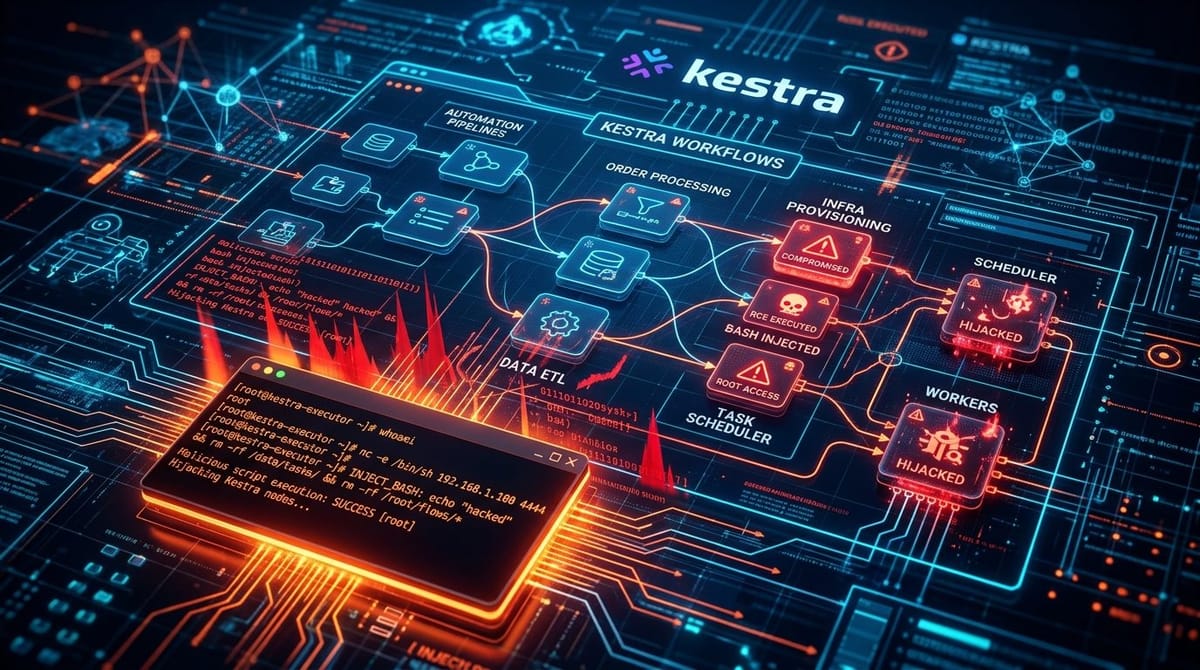
Attack Flow in Automation Workflows
In Kestra task flow definitions, user-supplied dynamic variables in shell script tasks were evaluated without strict argument sanitization. Remote actors crafting webhook trigger payloads can inject shell control sequences to breakout and execute commands on worker nodes.
🧭
More Deep Dives from this Roundup:
CVE-2026-20212: Cisco Nexus 9000 Silicon One Root RCE
CVE-2026-9586: Sangoma Switchvox SQL Injection & CISA KEV Analysis
CVE-2026-49869: Kestra OSS Command Injection & CI/CD Defense
Super Forms & Elementor Pro WordPress Mass RCE Campaign
Critical Infrastructure Alert: Telephony & Telecom Edge Attacks
← Return to Weekly Overview: Full Roundup

