
Hardening Next-Gen Edge Infrastructure: Defending SD-WAN, ADCs, and Central Security Management

📌
Security Roundup Series: https://colibrisec.org/security-roundup-f5-bigip-checkpoint-zeroday-velocloud-cisa-kev-week-of-september-25-2026/ • 4 min read deep dive
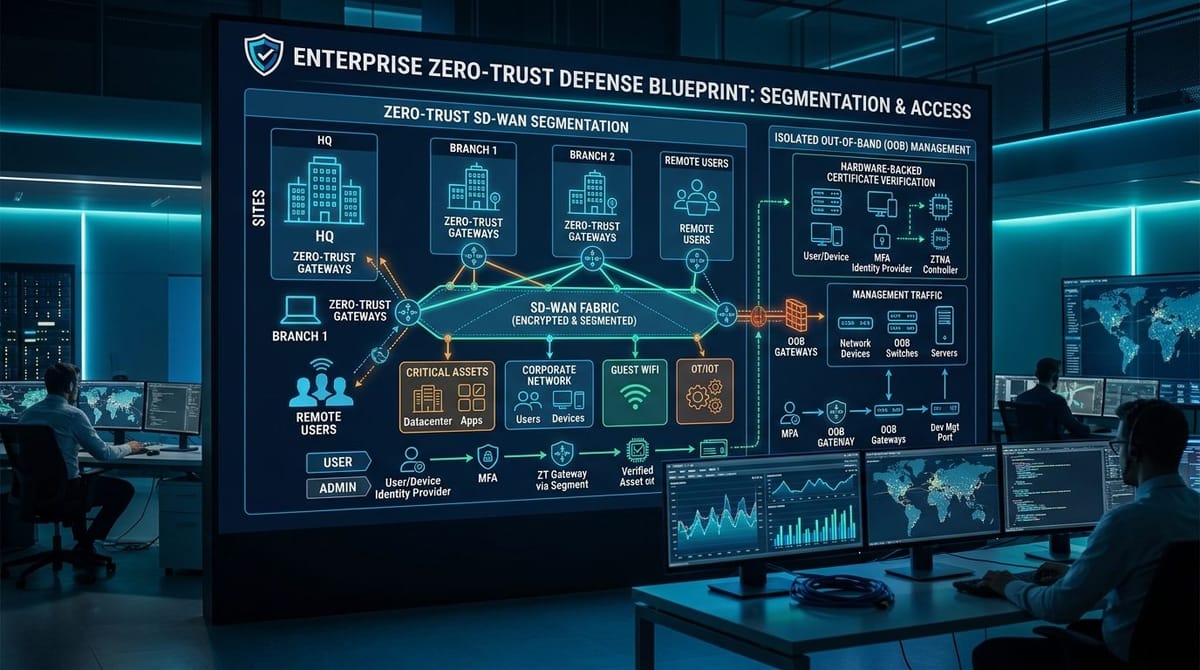
The widespread exploitation of core network devices—from F5 Application Delivery Controllers and Check Point Management Servers to Arista VeloCloud SD-WAN Orchestrators—demands a fundamental transformation in enterprise edge security. This blueprint outlines engineering strategies to insulate network control planes and enforce zero-trust segmentation.
Engineering Pillars for Next-Gen Edge Defense
1. Total Isolation of the Management Control Plane
Administrative consoles (F5 TMUI, Check Point Port 19009, VeloCloud VCO) must never reside on routable internet-facing segments.
- Place all management interfaces in dedicated, non-routable Out-of-Band (OOB) VLANs.
- Require multi-factor authentication (MFA) and hardware security tokens (FIDO2) for access to jump hosts.
- Enforce strict firewall rules dropping all ingress traffic on management ports from untrusted networks.
2. Cryptographic Certificate Validation & mTLS Hardening
To eliminate vulnerabilities like CVE-2026-93952 in SD-WAN fabrics:
1. Require Mutual TLS (mTLS) with strict client certificate signature verification.
2. Maintain automated CRL (Certificate Revocation List) and OCSP stapling validation.
3. Store edge device private keys within hardware-backed Trusted Platform Modules (TPM 2.0).
3. Zero-Trust SD-WAN Segmentation
Modern SD-WAN fabrics must segment branch traffic at the cryptographic layer rather than relying solely on IP routing:
- Apply end-to-end IPsec tunnel encryption with AES-256-GCM between edge nodes.
- Implement micro-segmentation policies that isolate guest Wi-Fi, corporate workloads, and IoT devices into distinct VRF (Virtual Routing and Forwarding) instances.
Infrastructure Verification Matrix
| Component | Vulnerability Target | Mitigation Control | Verification Command |
|---|---|---|---|
| F5 BIG-IP APM | OAuth Heap Overflow | Apply hotfix & deploy iRule filter | tmsh show sys version |
| Check Point Server | Port 19009 Path Traversal | Jumbo Hotfix & OOB isolation | fw ver -k |
| VeloCloud SD-WAN | Certificate Bypass | Upgrade VCO & rotate edge keys | Verify mTLS handshake logs |
| Enterprise Endpoints | ALPC / Browser Chains | Sept Patch Tuesday & Chrome 128+ | Verify build >= 10.0.22631.4169 |
🧭
More Deep Dives from this Roundup:
CVE-2026-94127: F5 BIG-IP APM OAuth Heap Buffer Overflow RCE
CVE-2026-93616: Check Point Management Server Zero-Day
CVE-2026-93952: Arista VeloCloud SD-WAN CVSS 10.0 Flaw
CLEANGULP Exploit Chain: Chrome V8 to Windows ALPC Zero-Day
Hardening Next-Gen Edge: SD-WAN, ADC & Management Defense
← Return to Weekly Overview: Full Roundup



