
CVE-2026-93952: Arista VeloCloud SD-WAN Orchestrator CVSS 10.0 Certificate Bypass in CISA KEV

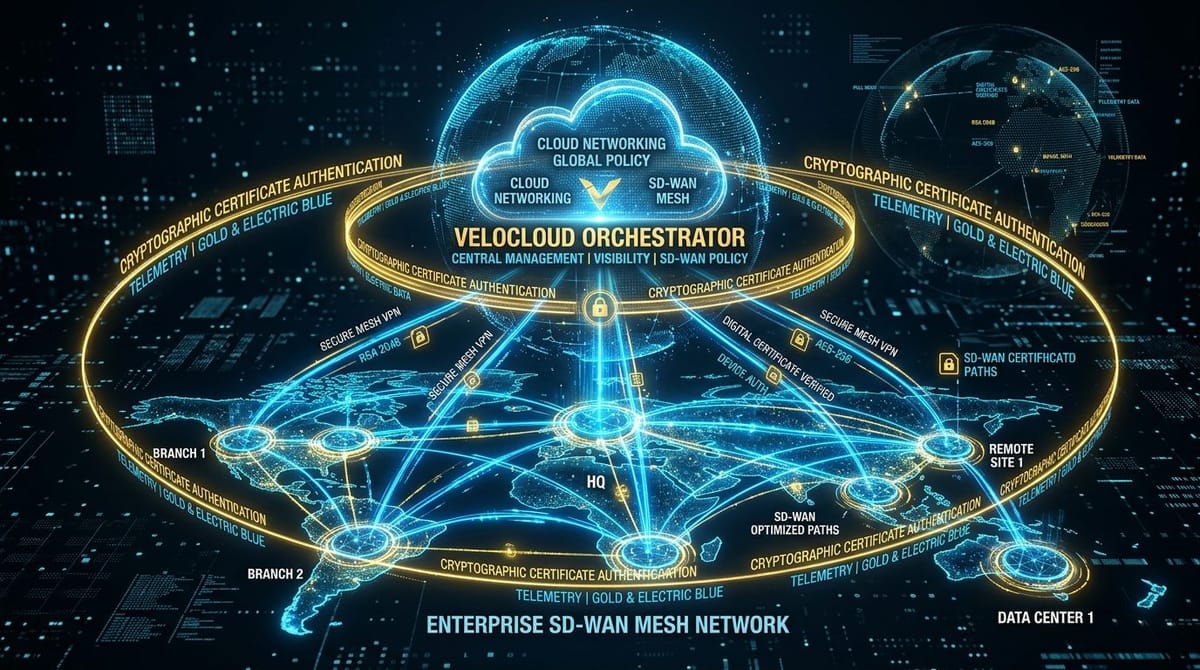
Rated with a maximum CVSS 10.0 score, CVE-2026-93952 is a critical improper input validation flaw affecting on-premises VeloCloud Orchestrator (VCO) instances. When certificate-based authentication is enabled, remote adversaries possessing the public key of a VeloCloud Edge device certificate can bypass identity boundaries and execute privileged administrative calls across the SD-WAN mesh.
Cryptographic Validation Bypass Mechanics
VeloCloud Orchestrator coordinates telemetry, routing overlays, and IPsec tunnel establishment between branch edge routers and data center hubs. During mutual TLS (mTLS) handshake negotiation, the VCO API gateway verifies client certificates against the centralized certificate authority.
CVE-2026-93952 arises because the VCO backend API gateway validated only the existence and subject common name of the presented edge certificate without verifying the cryptographic signature against the private key signature challenge. Consequently, an attacker presenting a widely distributed public edge certificate can authenticate as a legitimate edge device and invoke internal orchestration RPC endpoints.
SD-WAN Fabric Takeover Risk
Once authenticated to VCO with edge privileges, attackers can manipulate software-defined routing tables, redirect corporate branch traffic through malicious interception proxies (traffic hijacking), or push malicious configuration updates to thousands of connected branch edge appliances.
Remediation Guidance
- Upgrade VeloCloud Orchestrator: Apply the latest patched VCO software release immediately.
- Rotate Edge Device Certificates: Revoke and regenerate all VeloCloud Edge public-private keypairs across branch locations.
- Enable Strict Mutual Authentication: Ensure the orchestrator enforces strict signature verification across all incoming TLS handshakes.



