
CVE-2026-53266: Linux Kernel Netfilter Out-of-Bounds Memory Corruption in CISA KEV

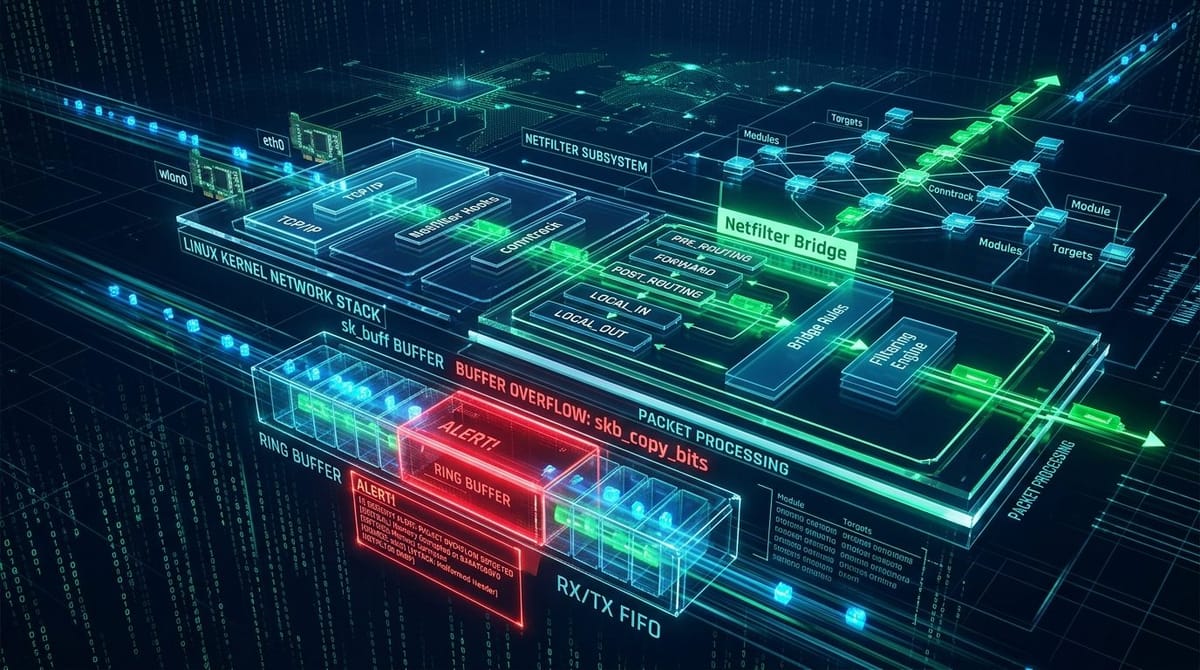
CISA has added CVE-2026-53266, an out-of-bounds write vulnerability in the Linux kernel netfilter bridge subsystem, to the Known Exploited Vulnerabilities catalog. The flaw allows local unprivileged users or compromised container processes to achieve local privilege escalation to root and escape containerized isolation environments.
Vulnerability Mechanics & Memory Corruption
The vulnerability exists within the ebtables SNAT module (net/bridge/netfilter/ebt_snat.c) during the handling of Ethernet bridge Address Resolution Protocol (ARP) packet rewriting. When a bridge network interface processes malformed ARP requests with non-standard hardware address lengths, the kernel function fails to validate the destination buffer boundary before performing an skb_copy_bits() operation.
/* Vulnerable code flow in ebt_snat.c */
static unsigned int
ebt_target_snat(struct sk_buff *skb, const struct xt_action_param *par)
{
    const struct ebt_nat_info *info = par->targinfo;
    /* Missing length validation against skb buffer limits */
    memcpy(eth_hdr(skb)->h_source, info->mac, ETH_ALEN);
    if (info->target == EBT_NAT_ARP) {
        /* Out-of-bounds write into adjacent slab cache page */
        arp_hdr_write(skb, info->mac);
    }
    return info->target;
}
By allocating contiguous kmalloc-512 slab caches and triggering rapid ARP frame transformations across bridge virtual interfaces, attackers corrupt adjacent kernel data structures (such as struct cred pointers), gaining full UID 0 root capabilities.
Container Escape Implications
In multi-tenant Kubernetes and container environments where unprivileged users can create network namespaces (CLONE_NEWNET), adversaries can initialize a private network bridge, configure an ebtables rule, and trigger the out-of-bounds write to break out of container sandboxes onto the host node.
Remediation & Hardening
- Apply Kernel Updates: Update host distributions (Ubuntu, RHEL, Debian) to patched upstream kernel releases (6.10.8+, 6.6.49+, 6.1.108+, 5.15.166+).
Disable Legacy ebtables Module: If bridge filtering is not required:
echo "blacklist ebtables" | sudo tee -a /etc/modprobe.d/blacklist.conf
echo "blacklist ebt_snat" | sudo tee -a /etc/modprobe.d/blacklist.conf
Restrict Unprivileged User Namespaces: If kernel upgrades cannot be deployed immediately, disable unprivileged user namespaces on worker nodes:
sudo sysctl -w kernel.unprivileged_userns_clone=0
echo "kernel.unprivileged_userns_clone=0" | sudo tee -a /etc/sysctl.d/99-security.conf


