Latest

Photon Health Healthcare Data Breach Concept

News

Photon Health Data Breach: Zero-Day SQL Injection in Self-Hosted Metabase Exposes Patient Prescriptions

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Photon Health, Inc. (Digital E-Prescription SaaS Infrastructure) Threat Actor / Attribution: Unidentified Threat Actor (Financial / Data Extortion) Impact / Records Compromised: Patient names, street addresses, phone numbers, dates of birth, sensitive prescription medications Initial Attack
By James Luther
ASOS Push Notification Security Breach Concept

News

ASOS Global Push Notification Breach: Xuanye Group Hijacks Customer Engagement Pipeline

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: ASOS.com (Global Online Fashion & Retail) Threat Actor / Attribution: Xuanye Group (Cyber Extortion Collective) Impact / Records Compromised: Customer names, email addresses, phone numbers, delivery addresses, search histories Initial Attack Vector: Social engineering

By James Luther
Operation MicroScan and FishHub Global Takedown

News

Operation MicroScan & FishHub: FBI Takedown of Integrity Tech Infrastructure and Emergency CISA KEV Order

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🏛️OPERATION MICROSCAN & FISHHUB: INFRASTRUCTURE TAKEDOWN Multinational law enforcement action led by FBI, DOJ, CISA, NSA, and Five Eyes + Spain + Japan targeting Beijing-based Integrity Technology Group. 7 core command and operational domains seized under federal court warrants

By James Luther
AhsayCBS Dual Zero-Day Exploit Chain Architecture

News

AhsayCBS Dual Zero-Day Exploit Chain: CVE-2026-105133 & CVE-2026-105134 Chained for Unauthenticated RCE

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-105133 & CVE-2026-105134 (CWE-287 (Improper Authentication) / CWE-78 (OS Command Injection)) Severity: CRITICAL (CVSS 9.3) Status: Actively Exploited in the Wild (First Observed Oct 7, 2026 by Huntress) Affected Systems: AhsayCBS Enterprise Backup

By James Luther
ColibriSec Weekly Security Roundup October 9 2026

News

Security Roundup: Atlassian Zero-Day, Citrix NetScaler Flaw, AhsayCBS RCE Chain, FBI MicroScan Takedown (Week of October 9, 2026)

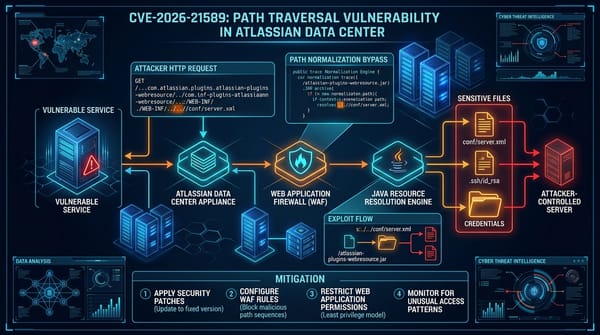
Executive Summary: The week of October 2 to October 9, 2026, delivered a rapid succession of perimeter breaches, critical zero-day weaponization, and historic multinational law enforcement actions. Atlassian self-hosted Data Center installations faced mass automated exploitation following proof-of-concept release for CVE-2026-21589 (CVSS 9.3), a path traversal vulnerability in web

By James Luther
Technical University of Denmark DTU DTUBasen Identity Management Breach

News

Technical University of Denmark (DTU) Breach: 200,000 Identities Exposed via DTUBasen IAM

📌Security Roundup Series: Weekend of October 5, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: Technical University of Denmark (Danmarks Tekniske Universitet - DTU) Threat Actor / Attribution: Unauthenticated Cyber Threat Actor / Credential Abuse Impact / Records Compromised: Up to 200,000 Current and Former Students, Faculty, and Researchers Initial

By ColibriSec
ShinyHunters Cybercrime Syndicate Detention Amman Jordan Law Enforcement

News

ShinyHunters Syndicate Operator Detained in Jordan: FBI Cooperation and Extortion Fallout

📌Security Roundup Series: Weekend of October 5, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: ShinyHunters Extortion Syndicate / International Law Enforcement Threat Actor / Attribution: FBI, Europol, Interpol, and Jordan General Intelligence Directorate (GID) Impact / Records Compromised: Critical Extortion Database Infrastructure & Forum Control Keys Seized Initial Attack Vector:

By ColibriSec
South Korean Commercial Banking Wave AI Credential Stuffing Attack

News

South Korean Banking Wave: Shinhan, KB Kookmin, Hana & Woori Hit in AI-Assisted Breach

📌Security Roundup Series: Weekend of October 5, 2026 • 4 min read deep dive🏛️Incident Overview: Target / Organization: South Korean Commercial Banking Sector (Shinhan, KB Kookmin, Hana, Woori) Threat Actor / Attribution: Specialized Financially Motivated Syndicate / Suspected State-Affiliated Actors Impact / Records Compromised: 70,000 High-Value Financial Accounts Compromised Initial Attack Vector: AI-Orchestrated

By ColibriSec