CVE-2026-54121: Certighost and the AD CS Flaw That Lets a Standard Account Impersonate a Domain Controller

How the CertiGhost AD CS vulnerability enables standard domain accounts to forge DC certificates and achieve instant domain takeover.

CVE-2026-54121: Certighost and the AD CS Flaw That Lets a Standard Account Impersonate a Domain Controller
Photo by Albert Stoynov / Unsplash
📌
Security Roundup Series: Week of July 27, 2026 • 5 min read deep dive

A critical Active Directory Certificate Services (AD CS) flaw nicknamed CertiGhost allows any standard domain user account to forge enterprise certificates and impersonate Domain Controllers with immediate forest-level compromise.

🚨
Vulnerability Intelligence: CVE ID: CVE-2026-54121 (AD CS Certificate Template Flaw) Severity: Critical 9.8 (Domain Takeover) Target: Active Directory Certificate Services (AD CS) PKI infrastructure Impact: Instant Domain Admin privilege escalation from unprivileged domain accounts

How CertiGhost Works

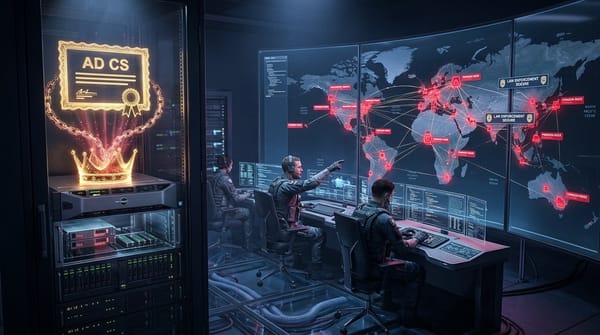
CertiGhost exploits misconfigured certificate template enrollment permissions combined with SAN (Subject Alternative Name) spoofing, allowing unprivileged domain accounts to request Kerberos authentication certificates on behalf of the Domain Controller computer object.

Remediation

✅
Remediation Steps: Audit AD CS certificate templates using tools like PSPKI or Certipy to identify templates with ENROLLEE_SUPPLIES_SUBJECT flags enabled. Enforce strong certificate mapping via registry settings on Domain Controllers (KB5014754 enforcement mode).
Read more

Guía de Defensa para CISOs del 9 de Noviembre de 2026 SonicWall KEV OpenSSH sshhole Linux TCP APT Keycloak Sandboxes de IA y Cadena de Frío OT

Guía de Defensa para CISOs del 9 de Noviembre de 2026: Blindaje de SonicOS SAML SSL-VPN, OpenSSH 10.6p2, Kernel Linux/APT, Keycloak/ForgeRock, IA y OT

📌Security Roundup Series: Fin de Semana del 9 de Noviembre de 2026 • 7 min de lectura deep dive🛡️Vulnerability Intelligence: CVE ID: CVE-2026-19868, CVE-2026-123158, CVE-2026-98432, CVE-2026-98276, CVE-2026-109518, CVE-2026-117691 y CVE-2026-123614 (Defensa Multicapa en Firewalls, OpenSSH Alpine, Kernel Linux/APT, SSO, Sandboxes de IA y Cadena de Frío OT) Severity: MANUAL

By James Luther
Reclamo de Extorsión de N0N contra Expedia, Investigación de 10M en el BIR de Filipinas, Iris Ohyama 7.7M, UChicago CS y Antonio Tajani

Extorsión Global, Fisco y Universidades: Reclamo de "N0N" contra Expedia, Investigación de 10M en el BIR de Filipinas, Iris Ohyama, UChicago CS y Canciller Tajani

📌Security Roundup Series: Fin de Semana del 9 de Noviembre de 2026 • 7 min de lectura deep dive🏛️RASTREADOR GLOBAL DE BRECHAS Y EXTORSIÓN (6 AL 9 DE NOVIEMBRE DE 2026) Análisis de cinco incidentes del fin de semana en el sector turístico, administración tributaria nacional, comercio electrónico en la

By James Luther