News

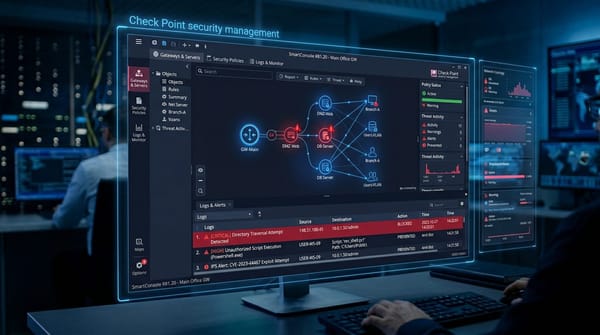
Check Point Security Management CVE-2026-93616 Technical Analysis

News

CVE-2026-93616: Check Point Security Management Server Path Traversal Zero-Day in CISA KEV

📌Security Roundup Series: https://colibrisec.org/security-roundup-f5-bigip-checkpoint-zeroday-velocloud-cisa-kev-week-of-september-25-2026/ • 4 min read deep dive🛡️Vulnerability Intelligence: Check Point has issued an urgent security notice detailing CVE-2026-93616, a critical zero-day vulnerability in the web service of Check Point Security Management Server. Discovered during targeted intrusions against enterprise security operations centers, the flaw enables
By James Luther
Arista VeloCloud Orchestrator CVE-2026-93952 Analysis

News

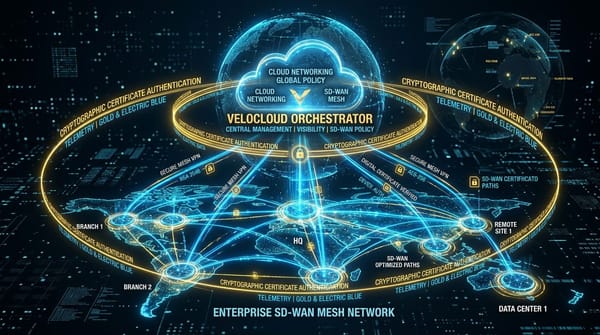
CVE-2026-93952: Arista VeloCloud SD-WAN Orchestrator CVSS 10.0 Certificate Bypass in CISA KEV

📌Security Roundup Series: https://colibrisec.org/security-roundup-f5-bigip-checkpoint-zeroday-velocloud-cisa-kev-week-of-september-25-2026/ • 4 min read deep dive🛡️Vulnerability Intelligence: Rated with a maximum CVSS 10.0 score, CVE-2026-93952 is a critical improper input validation flaw affecting on-premises VeloCloud Orchestrator (VCO) instances. When certificate-based authentication is enabled, remote adversaries possessing the public key of a VeloCloud

By James Luther
CLEANGULP Exploit Chain Chrome V8 to Windows ALPC

News

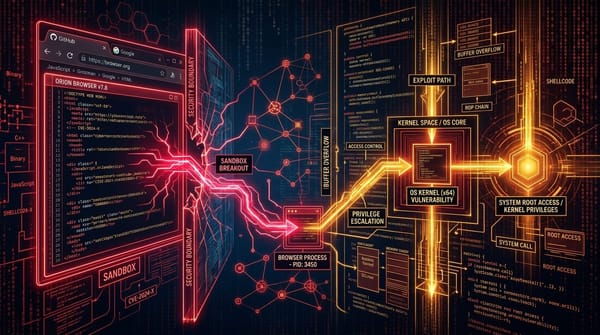
CLEANGULP Exploit Chain: Chaining Chrome V8 Sandbox Breakout with Windows ALPC Kernel Zero-Day

📌Security Roundup Series: https://colibrisec.org/security-roundup-f5-bigip-checkpoint-zeroday-velocloud-cisa-kev-week-of-september-25-2026/ • 4 min read deep dive Threat intelligence researchers have uncovered a state-backed cyber espionage campaign dubbed CLEANGULP. The threat actor chained an unpatched type-confusion vulnerability in Google Chrome’s V8 JavaScript engine with Microsoft’s recently disclosed Windows Advanced Local Procedure Call (ALPC)

By James Luther
ColibriSec Weekend Security Roundup September 21 2026

News

Security Roundup: Cisco AsyncOS Root RCE, Linux Kernel Netfilter in CISA KEV, Google Pixel Modem Zero-Day (Weekend Edition - September 21, 2026)

Executive Summary: Over the September 19–21 weekend, critical perimeter and infrastructure zero-day disclosures reached peak urgency. Cisco released emergency updates for an actively exploited unauthenticated root Remote Code Execution (RCE) flaw in Cisco Secure Email Gateway (AsyncOS), tracked as CVE-2026-76461. Simultaneously, CISA added Linux kernel Netfilter bridge memory corruption

By James Luther
Cisco AsyncOS CVE-2026-76461 Root RCE Technical Analysis

News

CVE-2026-76461: Cisco AsyncOS Root Remote Code Execution Under In-the-Wild Exploitation

📌Security Roundup Series: https://colibrisec.org/security-roundup-cisco-asyncos-root-rce-linux-netfilter-kev-pixel-modem-weekend-september-21-2026/ • 4 min read deep dive🛡️Vulnerability Intelligence: Cisco has published an urgent advisory warning of active in-the-wild exploitation targeting a critical vulnerability in Cisco AsyncOS Software for Cisco Secure Email Gateway. Tracked as CVE-2026-76461, this flaw allows unauthenticated remote adversaries to achieve root-level

By James Luther
Linux Kernel Netfilter CVE-2026-53266 Technical Analysis

News

CVE-2026-53266: Linux Kernel Netfilter Out-of-Bounds Memory Corruption in CISA KEV

📌Security Roundup Series: https://colibrisec.org/security-roundup-cisco-asyncos-root-rce-linux-netfilter-kev-pixel-modem-weekend-september-21-2026/ • 4 min read deep dive🛡️Vulnerability Intelligence: CISA has added CVE-2026-53266, an out-of-bounds write vulnerability in the Linux kernel netfilter bridge subsystem, to the Known Exploited Vulnerabilities catalog. The flaw allows local unprivileged users or compromised container processes to achieve local privilege escalation

By James Luther
Windows SSTP CVE-2026-73009 Remote Code Execution

News

CVE-2026-73009: Windows SSTP VPN Critical CVSS 9.8 Remote Code Execution Deep Dive

📌Security Roundup Series: https://colibrisec.org/security-roundup-cisco-asyncos-root-rce-linux-netfilter-kev-pixel-modem-weekend-september-21-2026/ • 4 min read deep dive🛡️Vulnerability Intelligence: Disclosed as part of Microsoft’s record-setting September 2026 security release, CVE-2026-73009 is a critical CVSS 9.8 Use-After-Free vulnerability in the Windows Secure Socket Tunneling Protocol (SSTP). The flaw allows unauthenticated remote attackers to execute

By James Luther
Google Pixel Modem CVE-2026-58704 Zero-Day Analysis

News

CVE-2026-58704: Google Pixel Cellular Modem Firmware Zero-Day Under Active Surveillance Exploitation

📌Security Roundup Series: https://colibrisec.org/security-roundup-cisco-asyncos-root-rce-linux-netfilter-kev-pixel-modem-weekend-september-21-2026/ • 4 min read deep dive🛡️Vulnerability Intelligence: Google’s September 2026 security bulletin and a subsequent CISA alert confirmed that CVE-2026-58704—a critical authorization bypass vulnerability in Google Pixel cellular modem firmware—has been actively exploited in targeted surveillance operations. Proximal attackers can

By James Luther