en
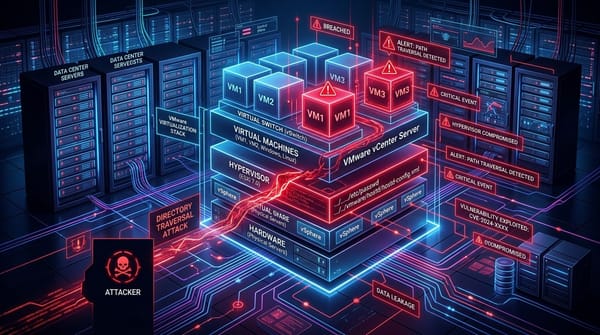
CVE-2026-59310: VMware vCenter Server Syslog Path Traversal Remote Code Execution
How attackers leverage CVE-2026-59310 in VMware vCenter Server's Syslog service to achieve unauthenticated root RCE and deploy reverse_ssh backdoors.

en
How attackers leverage CVE-2026-59310 in VMware vCenter Server's Syslog service to achieve unauthenticated root RCE and deploy reverse_ssh backdoors.
en
Technical analysis of CVE-2026-69836, a CVSS 10.0 deserialization flaw in Microsoft Entra ID actively targeted in cloud identity infrastructure.

en
How Wiz's autonomous AI red-team agent found a GitHub Actions command injection bug in a public Snowflake repository that Copilot-assisted review had missed.

en
Technical breakdown of CVE-2026-15748, the CVSS 9.8 unauthenticated arbitrary file upload flaw in Forminator Forms threatening 300,000 WordPress sites.

en
Deep dive on CVE-2026-18577, the actively exploited N-able N-central authentication bypass that lets attackers pivot from RMM servers into managed customer endpoints.

en
Deep technical analysis of CVE-2026-19478, GitLab's CVSS 9.4 unauthenticated GraphQL flaw that lets attackers delete public projects and user data.
en
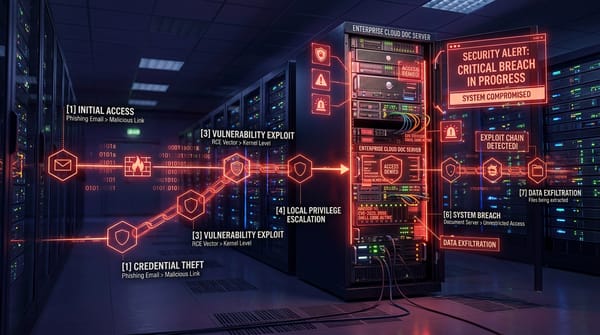
Technical breakdown of CVE-2026-63520 and how threat actors chain SharePoint input validation bugs to achieve pre-auth remote code execution.
en
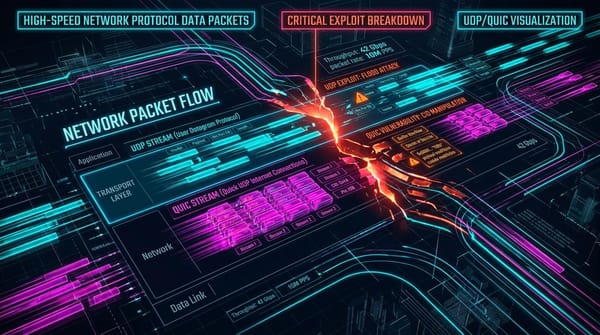
Deep technical analysis of CVE-2026-62815, a CVSS 9.8 Use-After-Free vulnerability in Microsoft QUIC allowing zero-click RCE over UDP.

en
Under the hood of ojo's zero-dependency engine: manifest parsing, Tree-sitter SAST queries, OS package diffing, and offline vulnerability databases.
guides
A complete architecture and deployment guide for OWASP Dependency-Track using Docker Compose, FluxCD, and ArgoCD.
Homelab
Step-by-step tutorial on securing a public-facing Raspberry Pi running Pi-hole, Squid, and Webmin with client TLS certificate authentication.

Hardware
How to build a budget multi-GPU cracking rig and machine learning workstation using repurposed hardware.