en
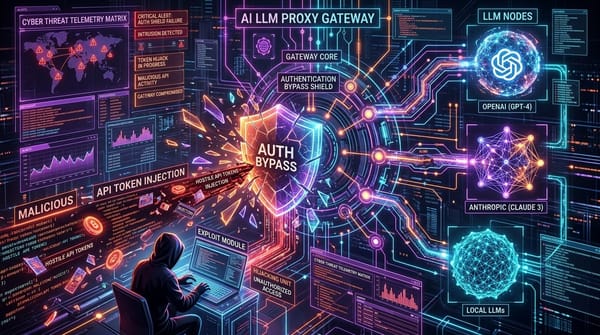
CVE-2026-59822: BerriAI LiteLLM Improper Authentication — CISA KEV Addition & LLM Proxy Compromise
Technical teardown of CVE-2026-59822 in BerriAI LiteLLM: authentication bypass in enterprise AI proxies, LLM key exfiltration, and CISA KEV implications.