Ransomware & Mega-Breach Forensics: CISA SafePay Advisory (AA26-293A), Emperador Hits AB InBev, Capcom ID (11.77M) & PingCAP TiDB Cloud

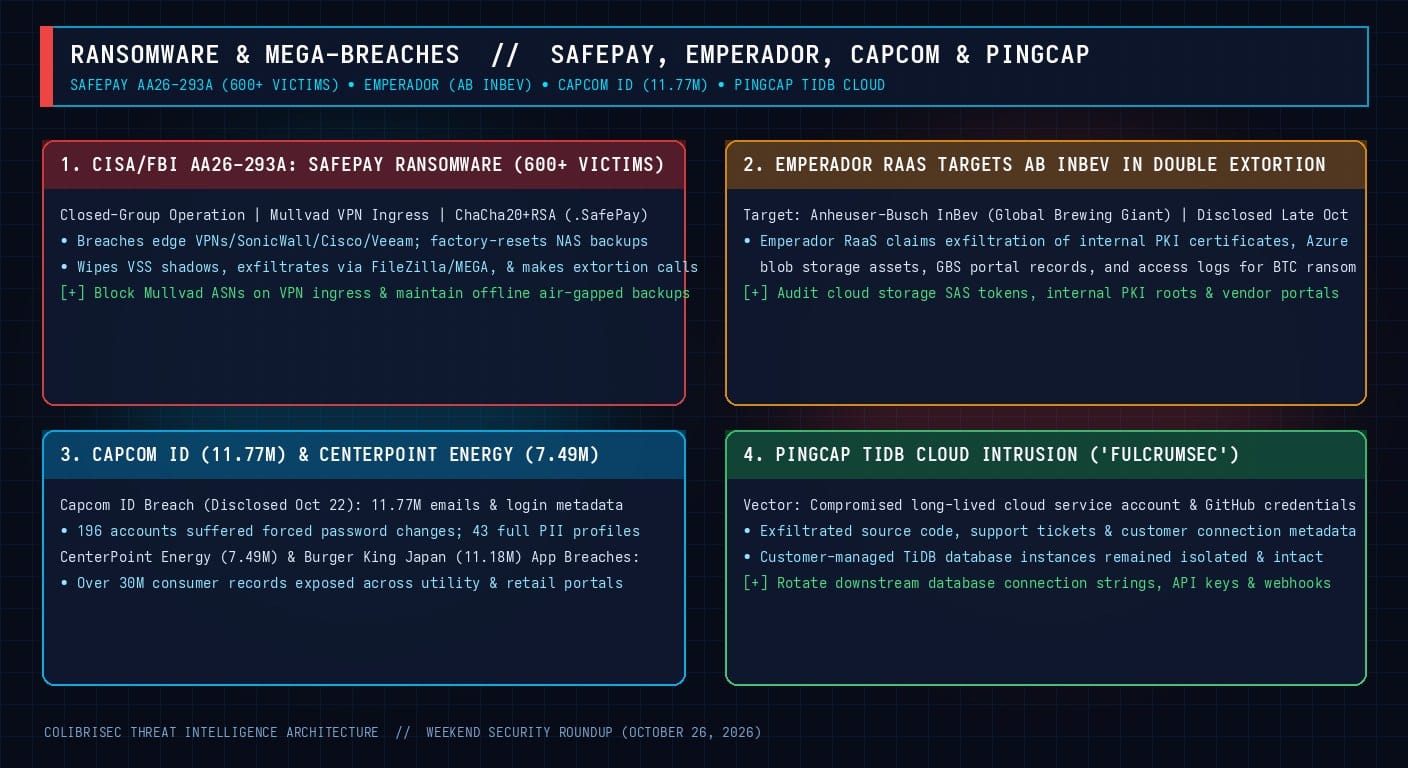
While zero-day vulnerabilities dominated patch queues, the operational fallout from double-extortion ransomware syndicates and cloud identity breaches reached staggering proportions entering the final week of October 2026. Joint cybersecurity advisory AA26-293A—issued by CISA, the FBI, the U.S. Secret Service, the UK’s NCA, and Germany’s BSI—revealed that the closed-group SafePay ransomware operation has compromised more than 600 organizations worldwide using a ruthless playbook that factory-resets Network-Attached Storage (NAS) backup arrays before deploying encryption. Over the weekend, the emerging Emperador RaaS group claimed a high-profile breach of global brewing giant AB InBev (Anheuser-Busch InBev), while forensic disclosures from Capcom (11.77 million CAPCOM ID accounts), PingCAP (TiDB Cloud internal infrastructure breached by FulcrumSec), CenterPoint Energy (7.49M records), and Burger King Japan (11.18M records) underscored a relentless wave of identity and data theft.
1. Joint Advisory AA26-293A: Inside SafePay’s 600-Victim Closed-Group Playbook
Unlike traditional Ransomware-as-a-Service (RaaS) cartels that recruit external affiliates on dark web forums, SafePay operates as a tightly controlled, closed syndicate. According to CISA and FBI telemetry in AA26-293A, this operational discipline has allowed SafePay to quietly compromise over 600 organizations across healthcare, manufacturing, energy, and government sectors since late 2024.
Distinctive SafePay TTPs: Mullvad Ingress & NAS Factory Resets
- Mullvad VPN Anonymized Ingress & Edge Exploitation: SafePay operators consistently route initial access and C2 traffic through commercial Mullvad VPN exit nodes, breaching victims via stolen VPN/RDP credentials (lacking phishing-resistant MFA) and unpatched edge vulnerabilities in Cisco, SonicWall, and Veeam appliances.
- Factory-Resetting NAS Backups Before Encryption: Before launching their LockBit-derived C/C++ encryptor (which uses hybrid ChaCha20 + RSA encryption, requires a runtime CLI passphrase
-pass <key>, and appends.SafePay), operators actively hunt for QNAP, Synology, and enterprise NAS storage consoles—issuing administrative API commands to wipe or factory-reset backup appliances while deleting Windows Volume Shadow Copies (vssadmin delete shadows /all /quiet). - Triple Extortion via Voice Calls: Following data exfiltration over FileZilla SFTP and MEGA.nz, SafePay operators place direct voice extortion calls to C-suite executives, employees, and customers to accelerate ransom negotiations.
2. Emperador Ransomware Claims AB InBev Breach (PKI & Azure Blob Exfiltration)
Late in the week and into the weekend, the emerging Emperador Ransomware-as-a-Service group (which recruits affiliates on the underground forum Dread) added AB InBev (Anheuser-Busch InBev)—the world’s largest brewer, headquartered in Leuven, Belgium—to its Tor extortion portal. Emperador alleged the theft of sensitive corporate infrastructure data, leaking sample archives purported to contain:
- Internal Public Key Infrastructure (PKI) certificates and cryptographic configuration artifacts.
- Microsoft Azure Blob Storage assets and internal Global Business Services (GBS) portal records.
- Internal authentication and access log telemetry, accompanied by a multi-million-dollar Bitcoin extortion demand.
3. Capcom ID (11.77M), PingCAP TiDB Cloud ("FulcrumSec") & 30M+ Consumer Records
Three major enterprise data breach post-mortems rounded out the weekend’s incident response landscape:
- Capcom ID Breach (11.77 Million Accounts): Disclosed on October 22 following detection on October 19, Japanese gaming giant Capcom confirmed unauthorized access to its global CAPCOM ID authentication and membership platform. The intrusion exposed email addresses, account creation dates, last login timestamps, and IP addresses for 11.77 million accounts worldwide, alongside forced password modifications on 196 accounts and full PII exposure for 43 users.
- PingCAP / TiDB Cloud Service-Account Intrusion ("FulcrumSec"): Distributed SQL vendor PingCAP disclosed that between September 9 and October 7, 2026, the extortion group FulcrumSec compromised a long-lived internal cloud service account and a GitHub account. While customer-managed TiDB database instances remained isolated and uncompromised, the attackers exfiltrated internal source code repositories, support ticket metadata, and customer connection logs—prompting urgent downstream API key and connection-string rotations.
- CenterPoint Energy (7.49M) & Burger King Japan (11.18M): U.S. electric and natural gas utility CenterPoint Energy confirmed that an external portal intrusion exposed 7.49 million customer records (including over 1 million Texas residents’ Social Security and driver’s license numbers), while Burger King Japan disclosed an October mobile app database breach affecting 11.18 million member profiles.
Detection & Hardening Directives
# 1. EDR Process Creation Hunt: Detect SafePay UAC bypass (CMSTPLUA COM) & VSS shadow wiping
(EventID=1 OR EventID=4688)
| search (CommandLine="*vssadmin*delete*shadows*" OR CommandLine="*bcdedit*recoveryenabled*No*" OR CommandLine="*-pass *-path *" OR ParentImage="*\dllhost.exe" CommandLine="*/Processid:{3E5FC7F9-9A51-4367-9063-A120244FBEC7}*")

# 2. Cloud IAM Audit: Identify long-lived AWS/GCP/Azure Service Account keys older than 30 days
gcloud iam service-accounts keys list [email protected] --managed-by=user
Remediation Priorities
- Block Commercial Anonymizer VPNs on Corporate Ingress: Per CISA AA26-293A, block Mullvad VPN and untrusted commercial anonymizer ASNs from initiating inbound authentication sessions to enterprise VPN, RDP, and SSO portals.
- Air-Gap NAS & Backup Management Planes: Place QNAP, Synology, Veeam, and enterprise SAN/NAS management interfaces on an out-of-band management VLAN with zero Active Directory credential trust and enable hardware-enforced immutable snapshots (WORM) that cannot be factory-reset remotely.
- Eliminate Long-Lived Cloud Service Account Keys: Replace static cloud service-account JSON keys and long-lived GitHub PATs with short-lived Workload Identity Federation (OIDC) tokens.