Vulnerability

Qualcomm Snapdragon FastRPC DSP Memory Corruption Zero-Day

News

CVE-2024-43047: Qualcomm FastRPC DSP Memory Corruption Zero-Day Exploited in Targeted Spyware Campaigns

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🛡️Vulnerability Intelligence: CVE ID: CVE-2024-43047 (CWE-416 (Use-After-Free)) Severity: HIGH (CVSS 7.8) Status: Actively Exploited In-The-Wild Zero-Day; Added to CISA KEV on Oct 8, 2024 (BOD 22-01) Affected Systems: Qualcomm Snapdragon Chipsets (FastRPC driver handling HLOS memory

By James Luther
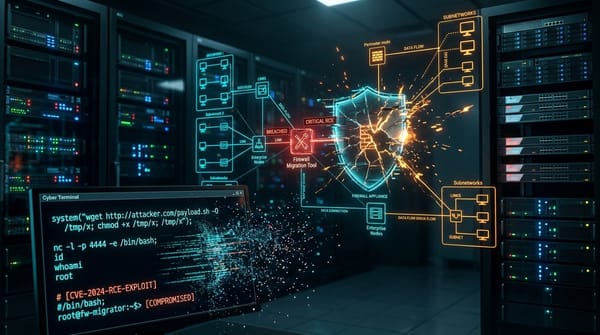
Palo Alto Networks Expedition Remote Code Execution Vulnerabilities

News

Palo Alto Networks Expedition RCE Chain: CVE-2024-9463 & CVE-2024-5910 Expose Enterprise Firewall Secrets

📌Security Roundup Series: Weekend of October 12, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2024-9463 & CVE-2024-5910 (CWE-78 (OS Command Injection) & CWE-306 (Missing Authentication)) Severity: CRITICAL (CVSS 9.9 (CVE-2024-9463) / 9.3 (CVE-2024-5910)) Status: Actively Exploited in the Wild; Added to CISA KEV (Mandatory Federal Remediation)

By James Luther
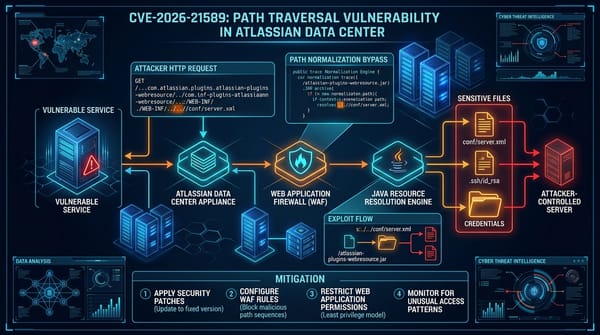
Apache HTTP Server Security Vulnerabilities Architecture

News

Apache HTTP Server Security Advisory: Critical RCE and Request Splitting Vulnerabilities in Version 2.4.68

📌Security Roundup Series: Week of October 9, 2026 • 4 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-42356 & CVE-2026-42528 (CWE-444 (Inconsistent Interpretation of HTTP Requests) / CWE-120 (Buffer Overflow)) Severity: HIGH / CRITICAL (CVSS 8.8 / 7.5) Status: Official Vendor Security Release Issued October 9, 2026 Affected Systems: Apache HTTP

By James Luther