en

ColibriSec Weekend Security Roundup October 19 2026

News

Security Roundup: BeyondTrust Zero-Day, ConnectWise M365 Supply-Chain Breach, Fortinet PEERSTITCH & SiteGuard WAF RCE (Weekend Edition - October 19, 2026)

Executive Summary: The weekend of October 16–19, 2026, confronted enterprise defenders with a relentless wave of nation-state appliance zero-days, cloud identity supply-chain compromises, memory-resident firewall implants, and emerging AI-targeted infrastructure heists. Leading the emergency alerts, CISA, Mandiant, and Google Threat Intelligence Group (GTIG) disclosed active zero-day exploitation of CVE-2026-102764

By James Luther
CVE-2026-102764 BeyondTrust Remote Support Zero-Day Armory Castle SAWFLY BARECLAW

News

CVE-2026-102764: BeyondTrust Remote Support Zero-Day Exploited by Armory Castle to Deploy SAWFLY & BARECLAW

📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-102764 (CWE-346 / CWE-290 (Origin Validation Error / Authentication Bypass by Spoofing)) Severity: CRITICAL (CVSS 9.3) Threat Actor: Armory Castle (UNC5221 / Warp Panda - China-Nexus Espionage) Status: Actively Exploited Zero-Day since Aug 29, 2026;

By James Luther
ConnectWise Cloud Backup Supply Chain Breach Microsoft 365 Service Principals

News

ConnectWise Cloud Backup Supply-Chain Attack: Compromised Service Principals Breach Hundreds of Microsoft 365 Tenants

📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🏛️Incident Overview: Target / Organization: ConnectWise Cloud Backup (Formerly SkyKick) & Downstream MSP Microsoft 365 Tenants Threat Actor / Attribution: Unattributed Supply-Chain Threat Actor (Automated Tenant Enumeration Campaign) Impact / Records Compromised: Hundreds of Enterprise & MSP Microsoft 365 Tenants

By James Luther
CVE-2025-61624 Fortinet Auto-Script Path Traversal PEERSTITCH Memory Resident Malware

News

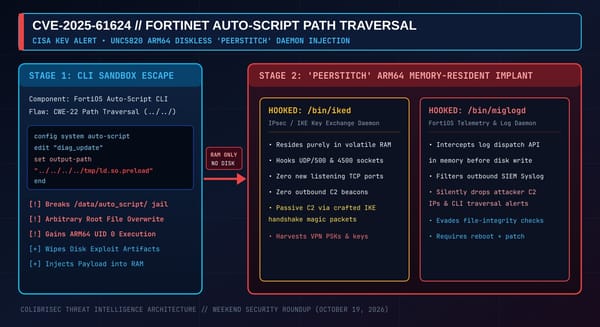
CVE-2025-61624: Fortinet Auto-Script Path Traversal Added to CISA KEV Following PEERSTITCH Memory-Resident Malware Attacks

📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2025-61624 (CWE-22 (Improper Limitation of a Pathname to a Restricted Directory)) Severity: HIGH / CRITICAL IN CHAIN (CVSS 5.4 (Chained for Root RCE)) Threat Actor: CL-STA-0954 / UNC5820 (Deploying PEERSTITCH ARM64 Implant) Status: Actively

By James Luther
CVE-2026-0322 Palo Alto Networks PAN-OS Management RCE and Drupal Critical Vulnerabilities

News

CVE-2026-0322 PAN-OS Management Interface RCE & Drupal Critical Advisories (CVE-2026-108097 / CVE-2026-108099)

📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🚨Vulnerability Intelligence: CVE ID: CVE-2026-0322 & CVE-2026-108097 / CVE-2026-108099 (CWE-94 (Code Injection in PAN-OS) & CWE-502 / CWE-94 (Drupal Render Callback Injection)) Severity: HIGH / CRITICAL (CVSS 8.6 (PAN-OS) / 9.8 (Drupal RCEs)) Status: CVE-2026-0322 Exploited in Targeted Attacks

By James Luther
OpenCode Console Breach AI Provider API Key Theft Model Distillation Attack

News

OpenCode Console Breach: Legacy Server Intrusion Fuels Large-Scale AI Model Distillation via Stolen Frontier API Keys

📌Security Roundup Series: Weekend of October 19, 2026 • 5 min read deep dive🏛️Incident Overview: Target / Organization: OpenCode Console (Hosted Developer AI Workspace Service) Threat Actor / Attribution: Financially & Strategically Motivated AI Distillation Threat Actors Impact / Records Compromised: ~1.4% of OpenCode Console Users (Exposed OpenAI, Anthropic, and Google Gemini

By James Luther
US Bankruptcy Noticing Center BAE Systems Federal Judiciary Contractor Cyberattack Outage

News

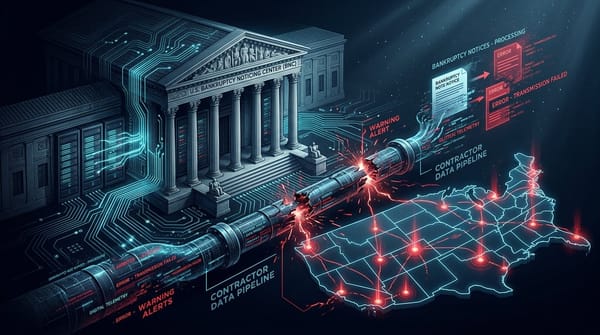
U.S. Bankruptcy Noticing Center Outage: BAE Systems Contractor Cyberattack Halts Federal Judiciary Notice Distribution

📌Security Roundup Series: Weekend of October 19, 2026 • 5 min read deep dive🏛️Incident Overview: Target / Organization: U.S. Bankruptcy Noticing Center (BNC) / BAE Systems IT (Federal Judiciary Contractor) Threat Actor / Attribution: Unattributed Threat Actor Targeting Federal Contractor Infrastructure Impact / Records Compromised: Nationwide Disruption of Federal Bankruptcy Notice Generation &

By James Luther
n0n Global Maritime Extortion Wave 38 Ports and Loxone Smart Building IT OT Isolation

News

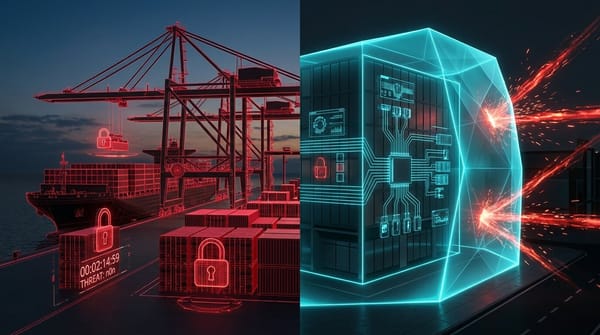
Global Maritime Extortion Wave ("n0n") & Loxone Cyberattack: Supply-Chain Port Extortion vs. Local OT Resilience

📌Security Roundup Series: Weekend of October 19, 2026 • 6 min read deep dive🏛️Incident Overview: Target / Organization: 38 Global Maritime Port/Shipping Entities ("n0n" Extortion Wave) & Loxone Building Automation Threat Actor / Attribution: Extortion Syndicate "n0n" (Maritime Campaign) & Unattributed Intruders (Loxone IT Breach) Impact / Records

By James Luther
Enterprise Hardening Blueprint Entra ID Service Principals Memory Malware Hunting WAF Isolation

guides

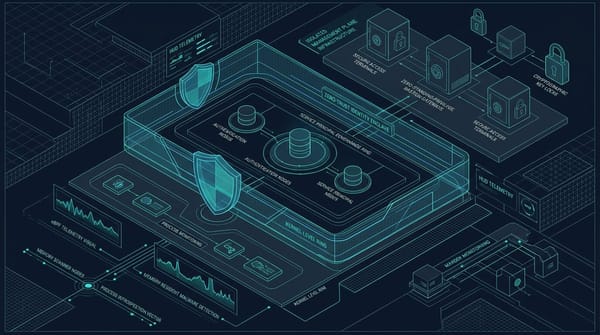
Enterprise Hardening Blueprint: Entra ID Service Principal Governance, Memory-Resident Malware Hunting & Management Plane Isolation

📌Security Roundup Series: Weekend of October 19, 2026 • 7 min read deep dive🛡️Defensive Engineering Scope: This blueprint translates the root causes of all major October 16–19, 2026 incidents into deployable production controls across four domains: Domain 1: Microsoft Entra ID Workload Identity & Service Principal Lockdown (Mitigating ConnectWise/

By James Luther